incident.io is an incident management platform that helps teams declare, manage, and learn from incidents.
Incident.io publishes 92 API contracts indexed on the APIs.io network, including Actions API, Alert Attributes API, Alert Routes API, and 89 more. Tagged areas include AIOps, Incident Management, Monitoring, and Incident Response.
The Incident.io catalog on APIs.io includes 1 Spectral governance ruleset.
Incident.io’s developer surface includes authentication, documentation, engineering blog, and 13 more developer resources.
Regulatory Posture applies to this provider. Its tags matched the
Horizontal (data, software, accessibility, platform) regime, so
Regulatory Posture carries 15 points of the composite.
If this regime is wrong for your business, say so on your
provider repo — the
applicability map is public and we will correct it.
Create-or-Update Ergonomics applies to this provider. This API accepts writes, so it
carries 10 points of the composite. It is scored from the published contracts
themselves: whether a caller can create-or-update in one call, whether the write accepts a key the caller already
holds, and whether the response says which branch ran. Without that, every write needs a search-and-branch in
front of it, and the first time that check is skipped a duplicate record is created.
Scored against the observed mean rather than raw — a provider at the catalog average is unchanged by this facet,
not penalised by it.
The six quality facets above are damped to 75 points between them,
because the conditional facet above carries the other
25. That is why each facet's contribution is shown against a damped
maximum: raising a quality facet moves the composite by 75% of its nominal
weight, not 100%. The full arithmetic is at apis.io/rating/.
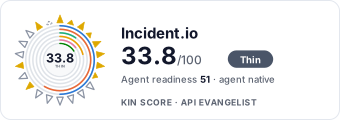
Show this score on your site.
It updates itself when the score changes. Paste this where you link to your API docs:
<a href="https://apis.io/providers/incident-io/"><img src="https://apis.io/badge/incident-io/card.svg" alt="Incident.io on APIs.io — Kin Score by API Evangelist"></a>
Other styles, a README pill and a shields.io endpoint are on the badge page.
Raise your score.
Agent readiness — checks not met, largest first (exact, from this profile):
A2A Agent Card+8 pts — a2a/-a2a.yml manifest, graded on conformance.grade against A2A 1.0.0
Delegated User Identity+6 pts — a served discovery document listing authorization_code in grant_types_supported (served), else an oauth2 authorizationCode flow or openIdConnect declared in an OpenAPI (documented)
Typed Event Surface+6 pts — AsyncAPI document, OR webhooks/callbacks objects in the as-published OpenAPI, OR common[].type includes Webhooks
Pagination+5 pts — share of collection GETs (an array, or one wrapped in data/items/results ...) that declare a page/limit/offset/cursor parameter, a Link header or a next/cursor field; na with no collection GETs
Agent Skills+5 pts — skills artifact present, graded by who authored it
4 more unmet checks in the Agent Readiness table above.
Kin Score — facets with the most composite points still available (weight × headroom):
incident.io is an area vendor: providers adopt it to run part of their developer surface. This is the Kin Score checks its features can move for a provider that adopts it, what each one really earns, and what it earns nothing for.
status pagecapability map4 features checked 2026-09-25 · rubric v0.22.0
incident.io status pages move one Kin Score check, status_page_present (6 of 38 operational-transparency points), once the provider declares the page as a StatusPage in apis.yml. The hosting clears the pointer-liveness probe: statuspage.incident.io/ and custom domains such as status.openai.com return a real 404 for nonsense paths, so the pointer grades live. Its Widget API, RSS subscriptions, maintenance windows and component uptime are good practice that no check reads, and its remote MCP server manages the provider's incident.io account rather than the provider's API.
Operational Transparency6.0 of 38 pts
Check
Earns
Through
Status page Operational TransparencyBinary check, cleared in full. The only check the status-page area touches.
Across 8977 providers that publish a contract, adopting incident.io would move 6390. Median lift: composite +2.0 (90th percentile +2.1), agent readiness +0.0 (+0.0). Conditional rows excluded.
What incident.io ships that earns nothing (2)
incident.io remote MCP server (mcp.incident.io) — It serves the provider’s own team their incident.io data. The dimension reads an MCP server for the provider’s API, described in the provider’s mcp/ manifest; this is neither.
Status Page API and public Widget API — A polled widget JSON is not an AsyncAPI document or webhooks in the provider’s OpenAPI.
A model, not a score. Adopting this vendor changes a provider's Kin Score only when the provider publishes the resulting artifacts on its own surface; nothing here writes a score, and no sponsorship or partnership can. The rating is not for sale → · Full vendor facets artifact
Markets this provider is in provisional
The Kin Score Market layer reads a provider inside its market:
its position, and how deep its integrations go. Depth is only comparable within a position. Provisional and unweighted:
not part of the Kin Score or agent readiness.
Registered MCP server and declares compatibility are report only — not weighted.
Undeclared means we found nothing we can read, so there is no number: we never infer integrations.
Standards this provider implements or carries. De facto ones are profiled and measured by the API Commons; formal ones come from the standards directory and are linked by the provider's own tags. The evidence column says how each claim was established — not that it was made.
Manage incident actions. These endpoints have been deprecated in favour of Actions V2 and Follow-ups V2, as these concepts have become increasingly separate. Incidents have two ...
Manage incident actions. These endpoints have been deprecated in favour of Actions V3, which returns the same action payload, and will be removed on 31 December 2026. The V3 Lis...
Manage incident actions. Incident actions are used during an incident, to track work such as 'restart the database' or 'contact the customer'. You can manage actions in the inci...
Create alerts within incident.io. The alerts API allows you to create alerts within incident.io by posting alert events. You can use alerts to automatically trigger incidents. T...
Manage notes attached to alerts. Notes let your team capture context, decisions, and investigation findings against an individual alert without needing to declare an incident. N...
Configure your alert routes in incident.io. Alert routes define how alerts from different sources are processed, grouped, and routed to the right teams and people.
Configure your alert routes in incident.io. Alert routes define how alerts from different sources are processed, grouped, and routed to the right teams and people.
Configure your alert sources in incident.io. Alert sources are the systems that send alerts to incident.io, which can then be routed to the right people and teams.
Read your alerts in incident.io. Alerts are events ingested from third parties by alert sources. They can trigger incidents and escalations, as configured in alert routes. To vi...
Create and manage announcement rules. An announcement rule posts an announcement of each incident that matches its conditions into the channels it lists, rendered with an announ...
Create and manage announcement templates. An announcement template controls which fields and actions appear on an announcement post. Each announcement rule renders its posts wit...
Manage API keys for your organization. This API lets you view, create, update, delete, and rotate API keys programmatically, including configuring account-level roles and roles ...
To give you visibility over the changes that are made within your incident.io account, we use an audit log. Our audit log is powered by WorkOS. The log
View and manage call routes: phone numbers your customers can call to reach whoever is on call. Use these endpoints to read how a route is configured, and to change who it pages...
List Scribe call sessions. Call sessions are the individual meetings Scribe attended: several can accumulate over time. Use this endpoint together with Call Transcript Entries t...
List the transcript entries Scribe captured during a call session. Entries are returned oldest first, ordered by when each participant started speaking. To export a full transcr...
Manage and browse catalog resources. These endpoints have been deprecated in favour of CatalogV3. The only breaking change is that the 'manual' attribute mode is now split into ...
Manage and browse catalog resources. Use the incident.io catalog to track services, teams, product features and anything else that helps build a map of your organisation. These ...
Manage custom field options. Single- and multi-select custom fields have a list of all available options, which have a value, and a sort key. The value must be unique to the cus...
Manage custom fields. Custom fields are used to attach metadata to incidents, which you can use when searching for incidents in the dashboard, triggering workflows, building ann...
Manage custom fields. Custom fields are used to attach metadata to incidents, which you can use when searching for incidents in the dashboard, triggering workflows, building ann...
Create and manage reusable, parameterised escalation path templates. An escalation path template declares parameters and a binding-aware path. Escalation paths built from a temp...
Create and manage escalation paths, and create, list, filter and respond to escalations. With incident.io On-call you can create escalation paths that describe how a page should...
Manage incident follow-ups. These endpoints have been deprecated in favour of Follow-ups V3, which returns the same follow-up payload, and will be removed on 31 December 2026. T...
Manage incident follow-ups. Incidents can have follow-ups associated with them, which track work that should be done after an incident (e.g. improving some documentation, or upg...
Send heartbeat pings for dead man's switch monitoring. Heartbeat alert sources expect periodic pings. If pings stop arriving, alerts fire automatically. Use the ping endpoints t...
Read everything that happened on an incident. The activity log is the full record: every status change, role handover, escalation, field edit and update, in the order they happe...
Create, list and delete incident attachments. Incident Attachments allows you to connect resources from external systems into incidents. Examples include: PagerDuty incidents an...
Configure the forms used to declare, accept, update, and resolve incidents. Each form carries its elements and the expressions those elements can reference. Escalate forms are n...
Manage incident roles. During an incident, you can assign responders to one of the incident roles that are configured in your organisation settings. Every organisation will have...
Manage incident roles. During an incident, you can assign responders to one of the incident roles that are configured in your organisation settings. Every organisation will have...
Manage incident statuses. Each incident has a status, picked from one of the statuses configured in your organisations settings. Statuses help communicate where an incident is i...
Read and write the items on an incident's timeline. The timeline is the curated narrative of an incident: the handful of moments that explain what happened, rather than the acti...
View incident timestamps. Each incident has a number of timestamps; some being defaults that we set on each incident for you, and other being configured for your organisation wi...
View incident types. With incident types enabled, you can tailor your process to the situation you're responding to with different custom fields and roles for each incident type.
List and create incident updates. Incident Updates allows you to see all the updates that have been shared against a particular incident. This will include any time that the Sev...
Create and read incidents. Incidents are a core resource, on which many other resources (actions, etc) are created. Care should be taken around these endpoints, as automation th...
Create and read incidents. Incidents are a core resource, on which many other resources (actions, etc) are created. Care should be taken around these endpoints, as automation th...
Manage maintenance windows for temporarily overriding alert routing during planned maintenance. Maintenance windows allow you to suppress or redirect alerts during scheduled mai...
Manage the policies that encode how your organisation should handle incidents. A policy scopes itself to a set of resources with conditions, states the requirements those resour...
View and manage the findings your policies raise. A finding records that a resource fell short of a policy: a follow-up that was never exported, a schedule with a gap in cover, ...
Manage post-mortem documents. Post-mortem documents capture the learnings from an incident, and are associated with a specific incident. Use this API to list and retrieve post-m...
Manage incident severities. Each incident has a severity, picked from one of the severities configured in your organisations settings. Severities help categorise incidents, and ...
Manage status page components. Components are organisation-scoped and can appear on multiple status pages via each page's structure. Use these endpoints to create and maintain c...
Manage and publish to status pages. Before using these endpoints, you must create a status page in the incident.io dashboard (find Status Pages in the left navigation bar). You ...
Manage teams. Teams are groups of users that can be associated with incidents, escalation paths, and other resources. Teams are built on top of catalog entries, allowing you to ...
View users. Users all have a single base role, and can be assigned multiple custom roles. They can be managed via your Slack workspace or SAML provider.
Webhooks can be used to receive notifications when certain events occur in incident.io. This might be useful for annotating graphs in a monitoring tool with incidents, or keepin...
Read the history of your workflow runs. A workflow run is one execution of a workflow, carrying the progress of every step it ran. Where a step sent a webhook, that progress als...
Not yet checked against Incident.io's own pricing page. Compiled by API Evangelist on 2026-05-04 from incident.io/pricing; confirm before you rely on a figure. A free plan or tier is listed.
Plan
Price
Basic freemium
Free
Team paid
$15.00 per per user (annual) / month · $19.00 per per user (monthly) / month
Pro paid
$25.00 per per user / month · $20.00 per on-call add-on / month
aid: incident-io
name: Incident.io
description: incident.io is an incident management platform that helps teams declare, manage, and learn from incidents.
type: Index
deliveryModel:
model: unknown
open_source: false
commercial: false
callable_host: true
label: Delivery model not determined — needs a product licence on record
confidence: low
source:
- openapi
generated: '2026-08-28'
method: derived
accessModel:
pricing: freemium
onboarding: self-serve
trial: false
try_now: true
public: false
gated: none
gated_source:
- onboarding
label: Freemium · Self-serve signup
confidence: medium
source:
- plans
- authentication
- security
generated: '2026-11-06'
method: derived
image: https://kinlane-images.s3.amazonaws.com/shared/apis-json/icons/incident-io.png
x-docs-platform: mintlify
x-docs-platform-confidence: medium
x-docs-platform-checked: 2026-10-03
x-docs-hosting: vercel
tags:
- AIOps
- Incident Management
- Monitoring
- Incident Response
url: https://raw.githubusercontent.com/api-evangelist/incident-io/refs/heads/main/apis.yml
created: '2026-03-27'
modified: '2026-05-19'
specificationVersion: '0.23'
apis:
- aid: incident-io:incident-io-actions-api
name: Incident.io Actions API
description: The Actions API from Incident.io — 2 operation(s) for actions.
humanURL: https://incident.io
tags:
- Actions
properties:
- type: OpenAPI
url: openapi/incident-io-actions-api-openapi.yml
- type: Documentation
url: https://api-docs.incident.io
- aid: incident-io:incident-io-alert-attributes-api
name: Incident.io Alert Attributes API
description: The Alert Attributes API from Incident.io — 2 operation(s) for alert attributes.
humanURL: https://incident.io
tags:
- Alert Attributes
properties:
- type: OpenAPI
url: openapi/incident-io-alert-attributes-api-openapi.yml
- type: Documentation
url: https://api-docs.incident.io
- aid: incident-io:incident-io-alert-routes-api
name: Incident.io Alert Routes API
description: The Alert Routes API from Incident.io — 2 operation(s) for alert routes.
humanURL: https://incident.io
tags:
- Alert Routes
properties:
- type: OpenAPI
url: openapi/incident-io-alert-routes-api-openapi.yml
- type: Documentation
url: https://api-docs.incident.io
- aid: incident-io:incident-io-alert-sources-api
name: Incident.io Alert Sources API
description: The Alert Sources API from Incident.io — 2 operation(s) for alert sources.
humanURL: https://incident.io
tags:
- Alert Sources
properties:
- type: OpenAPI
url: openapi/incident-io-alert-sources-api-openapi.yml
- type: Documentation
url: https://api-docs.incident.io
- aid: incident-io:incident-io-alerts-api
name: Incident.io Alerts API
description: The Alerts API from Incident.io — 3 operation(s) for alerts.
humanURL: https://incident.io
tags:
- Alerts
properties:
- type: OpenAPI
url: openapi/incident-io-alerts-api-openapi.yml
- type: Documentation
url: https://api-docs.incident.io
- aid: incident-io:incident-io-api-keys-api
name: Incident.io API Keys API
description: The API Keys API from Incident.io — 3 operation(s) for api keys.
humanURL: https://incident.io
tags:
- APIKeys
tags_raw:
- API Keys
properties:
- type: OpenAPI
url: openapi/incident-io-api-keys-api-openapi.yml
- type: Documentation
url: https://api-docs.incident.io
- aid: incident-io:incident-io-catalog-entries-api
name: Incident.io Catalog Entries API
description: The Catalog Entries API from Incident.io — 2 operation(s) for catalog entries.
humanURL: https://incident.io
tags:
- Catalog Entries
properties:
- type: OpenAPI
url: openapi/incident-io-catalog-entries-api-openapi.yml
- type: Documentation
url: https://api-docs.incident.io
- aid: incident-io:incident-io-catalog-types-api
name: Incident.io Catalog Types API
description: The Catalog Types API from Incident.io — 2 operation(s) for catalog types.
humanURL: https://incident.io
tags:
- Catalog Types
properties:
- type: OpenAPI
url: openapi/incident-io-catalog-types-api-openapi.yml
- type: Documentation
url: https://api-docs.incident.io
- aid: incident-io:incident-io-custom-fields-api
name: Incident.io Custom Fields API
description: The Custom Fields API from Incident.io — 2 operation(s) for custom fields.
humanURL: https://incident.io
tags:
- Custom Fields
properties:
- type: OpenAPI
url: openapi/incident-io-custom-fields-api-openapi.yml
- type: Documentation
url: https://api-docs.incident.io
- aid: incident-io:incident-io-escalation-paths-api
name: Incident.io Escalation Paths API
description: The Escalation Paths API from Incident.io — 2 operation(s) for escalation paths.
humanURL: https://incident.io
tags:
- Escalation Paths
properties:
- type: OpenAPI
url: openapi/incident-io-escalation-paths-api-openapi.yml
- type: Documentation
url: https://api-docs.incident.io
- aid: incident-io:incident-io-escalations-api
name: Incident.io Escalations API
description: The Escalations API from Incident.io — 2 operation(s) for escalations.
humanURL: https://incident.io
tags:
- Escalations
properties:
- type: OpenAPI
url: openapi/incident-io-escalations-api-openapi.yml
- type: Documentation
url: https://api-docs.incident.io
- aid: incident-io:incident-io-follow-ups-api
name: Incident.io Follow-ups API
description: The Follow-ups API from Incident.io — 2 operation(s) for follow-ups.
humanURL: https://incident.io
tags:
- Follow-ups
properties:
- type: OpenAPI
url: openapi/incident-io-follow-ups-api-openapi.yml
- type: Documentation
url: https://api-docs.incident.io
- aid: incident-io:incident-io-incident-roles-api
name: Incident.io Incident Roles API
description: The Incident Roles API from Incident.io — 2 operation(s) for incident roles.
humanURL: https://incident.io
tags:
- Incident Roles
properties:
- type: OpenAPI
url: openapi/incident-io-incident-roles-api-openapi.yml
- type: Documentation
url: https://api-docs.incident.io
- aid: incident-io:incident-io-incident-statuses-api
name: Incident.io Incident Statuses API
description: The Incident Statuses API from Incident.io — 2 operation(s) for incident statuses.
humanURL: https://incident.io
tags:
- Incident Statuses
properties:
- type: OpenAPI
url: openapi/incident-io-incident-statuses-api-openapi.yml
- type: Documentation
url: https://api-docs.incident.io
- aid: incident-io:incident-io-incident-types-api
name: Incident.io Incident Types API
description: The Incident Types API from Incident.io — 2 operation(s) for incident types.
humanURL: https://incident.io
tags:
- Incident Types
properties:
- type: OpenAPI
url: openapi/incident-io-incident-types-api-openapi.yml
- type: Documentation
url: https://api-docs.incident.io
- aid: incident-io:incident-io-incidents-api
name: Incident.io Incidents API
description: The Incidents API from Incident.io — 2 operation(s) for incidents.
humanURL: https://incident.io
tags:
- Incidents
properties:
- type: OpenAPI
url: openapi/incident-io-incidents-api-openapi.yml
- type: Documentation
url: https://api-docs.incident.io
- aid: incident-io:incident-io-maintenance-windows-api
name: Incident.io Maintenance Windows API
description: The Maintenance Windows API from Incident.io — 2 operation(s) for maintenance windows.
humanURL: https://incident.io
tags:
- Maintenance Windows
properties:
- type: OpenAPI
url: openapi/incident-io-maintenance-windows-api-openapi.yml
- type: Documentation
url: https://api-docs.incident.io
- aid: incident-io:incident-io-postmortem-documents-api
name: Incident.io Postmortem Documents API
description: The Postmortem Documents API from Incident.io — 2 operation(s) for postmortem documents.
humanURL: https://incident.io
tags:
- Postmortem Documents
properties:
- type: OpenAPI
url: openapi/incident-io-postmortem-documents-api-openapi.yml
- type: Documentation
url: https://api-docs.incident.io
- aid: incident-io:incident-io-schedules-api
name: Incident.io Schedules API
description: The Schedules API from Incident.io — 2 operation(s) for schedules.
humanURL: https://incident.io
tags:
- Schedule
tags_raw:
- Schedules
properties:
- type: OpenAPI
url: openapi/incident-io-schedules-api-openapi.yml
- type: Documentation
url: https://api-docs.incident.io
- aid: incident-io:incident-io-severities-api
name: Incident.io Severities API
description: The Severities API from Incident.io — 2 operation(s) for severities.
humanURL: https://incident.io
tags:
- Severities
properties:
- type: OpenAPI
url: openapi/incident-io-severities-api-openapi.yml
- type: Documentation
url: https://api-docs.incident.io
- aid: incident-io:incident-io-status-pages-api
name: Incident.io Status Pages API
description: The Status Pages API from Incident.io — 2 operation(s) for status pages.
humanURL: https://incident.io
tags:
- Status Pages
properties:
- type: OpenAPI
url: openapi/incident-io-status-pages-api-openapi.yml
- type: Documentation
url: https://api-docs.incident.io
- aid: incident-io:incident-io-teams-api
name: Incident.io Teams API
description: The Teams API from Incident.io — 2 operation(s) for teams.
humanURL: https://incident.io
tags:
- Team
tags_raw:
- Teams
properties:
- type: OpenAPI
url: openapi/incident-io-teams-api-openapi.yml
- type: Documentation
url: https://api-docs.incident.io
- aid: incident-io:incident-io-users-api
name: Incident.io Users API
description: The Users API from Incident.io — 2 operation(s) for users.
humanURL: https://incident.io
tags:
- User
tags_raw:
- Users
properties:
- type: OpenAPI
url: openapi/incident-io-users-api-openapi.yml
- type: Documentation
url: https://api-docs.incident.io
- aid: incident-io:incident-io-utilities-api
name: Incident.io Utilities API
description: The Utilities API from Incident.io — 3 operation(s) for utilities.
humanURL: https://incident.io
tags:
- Utilities
properties:
- type: OpenAPI
url: openapi/incident-io-utilities-api-openapi.yml
- type: Documentation
url: https://api-docs.incident.io
- aid: incident-io:incident-io-workflows-api
name: Incident.io Workflows API
description: The Workflows API from Incident.io — 2 operation(s) for workflows.
humanURL: https://incident.io
tags:
- Workflows
properties:
- type: OpenAPI
url: openapi/incident-io-workflows-api-openapi.yml
- type: Documentation
url: https://api-docs.incident.io
- aid: incident-io:incident-io-actions-v1-api
name: Incident.io Actions V1 API
description: "Manage incident actions.\n\nThese endpoints have been deprecated in favour of Actions V2 and Follow-ups V2,\
\ as these\nconcepts have become increasingly separate.\n\nIncidents have two types of actions associated to them:\n\n\
- Actions, used during an incident response as ephemeral todo lists\n- Follow-ups, actions which are for after the incident\
\ and can be exported to external\n\tissue trackers\n\nYou can manage actions in the incident Slack channel with <code>/incident\
\ actions</code>, or on\nthe incident homepage.\n\nExporting follow-ups to external issue trackers can be done in the\
\ incident homepage."
humanURL: https://incident.io
tags:
- Actions V1
properties:
- type: OpenAPI
url: openapi/incident-io-actions-v1-api-openapi.yml
- aid: incident-io:incident-io-actions-v2-api
name: Incident.io Actions V2 API
description: 'Manage incident actions.
These endpoints have been deprecated in favour of Actions V3, which returns the same
action payload, and will be removed on 31 December 2026. The V3 List endpoint is paginated
and supports filtering by created_at and updated_at, so use it instead of re-fetching the
full list.
Incident actions are used during an incident, to track work such as ''restart the database'' or ''contact the customer''.
You can manage actions in the incident Slack channel with <code>/incident actions</code>, or on
the incident homepage.'
humanURL: https://incident.io
tags:
- Actions V2
properties:
- type: OpenAPI
url: openapi/incident-io-actions-v2-api-openapi.yml
- aid: incident-io:incident-io-actions-v3-api
name: Incident.io Actions V3 API
description: 'Manage incident actions.
Incident actions are used during an incident, to track work such as ''restart the database'' or ''contact the customer''.
You can manage actions in the incident Slack channel with <code>/incident actions</code>, or on
the incident homepage.'
humanURL: https://incident.io
tags:
- Actions V3
properties:
- type: OpenAPI
url: openapi/incident-io-actions-v3-api-openapi.yml
- aid: incident-io:incident-io-alert-attributes-v2-api
name: Incident.io Alert Attributes V2 API
description: 'View and manage alert attributes.
Alert attributes are used to parse structured data from alerts coming in via alert sources.'
humanURL: https://incident.io
tags:
- Alert Attributes V2
properties:
- type: OpenAPI
url: openapi/incident-io-alert-attributes-v2-api-openapi.yml
- aid: incident-io:incident-io-alert-events-v2-api
name: Incident.io Alert Events V2 API
description: 'Create alerts within incident.io.
The alerts API allows you to create alerts within incident.io by posting alert events. You
can use alerts to automatically trigger incidents.
To create an alert, you must first configure an alert source in the incident.io dashboard.'
humanURL: https://incident.io
tags:
- Alert Events V2
properties:
- type: OpenAPI
url: openapi/incident-io-alert-events-v2-api-openapi.yml
- aid: incident-io:incident-io-alert-notes-v1-api
name: Incident.io Alert Notes V1 API
description: 'Manage notes attached to alerts.
Notes let your team capture context, decisions, and investigation findings against
an individual alert without needing to declare an incident.
Note content is stored and returned as Markdown. The following formatting is
supported:
- **Headings** (`#`, `##`, `###`)
- **Bold** and *italic* text formatting
- ~~Strikethrough~~ text
- Inline `code` and fenced code blocks
- Bullet lists and numbered lists
- Blockquotes
- [Links](url) using Markdown link syntax — bare URLs are not auto-linked
- Tables (GitHub-flavoured Markdown)
- Horizontal rules (`---`)
Raw HTML, image syntax (``), task lists, and footnotes are not
supported, and will be stripped or rendered as plain text.'
humanURL: https://incident.io
tags:
- Alert Notes V1
properties:
- type: OpenAPI
url: openapi/incident-io-alert-notes-v1-api-openapi.yml
- aid: incident-io:incident-io-alert-routes-v2-api
name: Incident.io Alert Routes V2 API
description: 'Configure your alert routes in incident.io.
Alert routes define how alerts from different sources are processed, grouped, and routed to the right teams and people.'
humanURL: https://incident.io
tags:
- Alert Routes V2
properties:
- type: OpenAPI
url: openapi/incident-io-alert-routes-v2-api-openapi.yml
- aid: incident-io:incident-io-alert-routes-v3-api
name: Incident.io Alert Routes V3 API
description: 'Configure your alert routes in incident.io.
Alert routes define how alerts from different sources are processed, grouped, and routed to the right teams and people.'
humanURL: https://incident.io
tags:
- Alert Routes V3
properties:
- type: OpenAPI
url: openapi/incident-io-alert-routes-v3-api-openapi.yml
- aid: incident-io:incident-io-alert-sources-v2-api
name: Incident.io Alert Sources V2 API
description: 'Configure your alert sources in incident.io.
Alert sources are the systems that send alerts to incident.io, which can then be routed to the right people and teams.'
humanURL: https://incident.io
tags:
- Alert Sources V2
properties:
- type: OpenAPI
url: openapi/incident-io-alert-sources-v2-api-openapi.yml
- aid: incident-io:incident-io-alerts-v2-api
name: Incident.io Alerts V2 API
description: "Read your alerts in incident.io.\n\nAlerts are events ingested from third parties by alert sources. They can\
\ trigger incidents and escalations, as configured in alert routes.\nTo view your alerts, you can list all alerts, or\
\ show a single alert. \nIf you'd like to view only alerts that are currently firing, you can filter by status. \nTo view\
\ the alert that was created for an event in your external system, filter by deduplication key. \n\nIf you'd like to view\
\ alerts connected to a particular incident, you can list incident alerts. You can filter by incident_id to find all alerts\
\ attached to a particular incident, or by alert_id to find the incident that a particular alert triggered."
humanURL: https://incident.io
tags:
- Alerts V2
properties:
- type: OpenAPI
url: openapi/incident-io-alerts-v2-api-openapi.yml
- aid: incident-io:incident-io-announcement-rules-v2-api
name: Incident.io Announcement Rules V2 API
description: 'Create and manage announcement rules.
An announcement rule posts an announcement of each incident that matches its conditions
into the channels it lists, rendered with an announcement template.'
humanURL: https://incident.io
tags:
- Announcement Rules V2
properties:
- type: OpenAPI
url: openapi/incident-io-announcement-rules-v2-api-openapi.yml
- aid: incident-io:incident-io-announcement-templates-v2-api
name: Incident.io Announcement Templates V2 API
description: 'Create and manage announcement templates.
An announcement template controls which fields and actions appear on an announcement post.
Each announcement rule renders its posts with one template.'
humanURL: https://incident.io
tags:
- Announcement Templates V2
properties:
- type: OpenAPI
url: openapi/incident-io-announcement-templates-v2-api-openapi.yml
- aid: incident-io:incident-io-api-keys-v1-api
name: Incident.io API Keys V1 API
description: 'Manage API keys for your organization.
This API lets you view, create, update, delete, and rotate API keys programmatically, including configuring account-level
roles and roles scoped to specific teams.
Common use cases include:
- **API key rotation**: You can issue a new access token for any API key using the `Rotate` endpoint.
- **Managing keys at scale**: use the `Show`, `List`, `Create`, `Update`, and `Delete` endpoints to automate API key lifecycle
management.
## Permissions model
To use these endpoints, your API key must have the `api_keys_manage` role granted at either the account level or for specific
teams.
In addition, the following rules apply, when a "caller" API key is managing a "target" API key:
- A caller key can only assign roles whose scopes are a subset of its own scopes. For example, a key with `viewer` and
`incident_creator` can assign those roles to a target key, but cannot assign the `incident_editor` role, since it has
additional scopes.
- The same applies at the team level: A caller key with `schedules_editor` at the account level can create a target key
with that role for a specific team, but a key with `schedules_editor` only for one team (Team A, say) cannot assign it
at the account level or for another team, Team B.
- The `api_keys_manage` role cannot be assigned via the API. To create a key with that role, you must go to Settings →
API keys in the dashboard, and click "Add new", creating a key with the "View, create, edit, delete or rotate API keys"
role (`api_keys_manage`).
- The `Delete` endpoint does not check whether the calling API key holds the scopes of the key being deleted. However,
a team-scoped key can only delete keys belonging to its teams.
- To rotate the token of an API key, use the Rotate endpoint or by clicking "Rotate token" on any API key listed in the
dashboard. The same permissions limitations apply as when creating or updating an API key.
## Finding role names and team IDs
To find valid values for `role_names`, `team_ids`, and `team_role_names`, go to Settings → API keys in the dashboard.
Click to either edit an existing key or create a new one, select the desired roles and teams, and then use the copy button
to get hold of the role and team identifiers as JSON.'
humanURL: https://incident.io
tags:
- API Keys V1
properties:
- type: OpenAPI
url: openapi/incident-io-api-keys-v1-api-openapi.yml
- aid: incident-io:incident-io-audit-logs-api
name: Incident.io Audit logs API
description: "To give you visibility over the changes that are made within your incident.io account, we use an audit log.\
\ Our audit log is powered by <a href=\"https://workos.com\" target=\"_blank\">WorkOS</a>. The log is available for customers\
\ on our [Enterprise plan](https://incident.io/pricing).\n\nThe audit log contains information about any configuration\
\ changes, as well as changes to a user's permissions (e.g. being given a new role, or access to a private incident).\n\
\nEach entry will have an actor (the person or system that made the change) and one or more targets (a thing that was\
\ modified by this change). It will also include the Location and User Agent of the actor, where applicable.\n\nEach entry\
\ will conform to a schema, which is documented here. Each entry also has a version, so that if our schema changes over\
\ time you’ll still be able to parse old events.\n\nWe’ll retain these entries for one year.\n\nAudit log entries start\
\ from 18 April, 2023 (there are no entries available from before that date) and are retained in WorkOS for 365 days.\n\
\n## Viewing your audit log\n\nYou can view your audit log via our [security settings](https://app.incident.io/settings/security)\
\ page.\n\nFrom there, you'll be able to:\n\n- View the entries via a web interface (filterable by target, event type,\
\ actor and date)\n- Export the entries for a given time period to a CSV\n- Set up a log stream to a provider of your\
\ choice (e.g. Splunk or an Amazon S3 bucket)\n\n## Understanding actors\n\nEach entry will have an actor associated with\
\ it, which is one of 6 types:\n\n### Users\n\nThis is for changes triggered by the actions of a particular user in your\
\ account.\n\nAs an example:\n\n```\n\"actor\": {\n \"type\": \"user\",\n \"id\": \"01G0J1EXE7AXZ2C93K61WBPYEH\"\
,\n \"name\": \"Kelsey Mills\",\n \"metadata\": {\n \"user_base_role_slug\": \"admin\",\n \"user_custom_role_slugs\"\
: \"engineering,security\"\n }\n }\n```\n\n### API Keys\n\nThis is for changes triggered by an API key.\n\nAs an example:\n\
\n```\n\"actor\": {\n \"type\": \"api_key\",\n \"id\": \"01G0J1EXE7AXZ2C93K61WBPYEH\",\n \"name\": \"Lisa's development\
\ key\",\n \"metadata\": {\n \"api_key_roles\": \"incident_creator,global_access\"\n }\n }\n```\n\n### Integrations\n\
\nThis is for changes triggered by a system. Sometimes that will be a third party system (e.g. a user might be created\n\
via Slack) or sometimes it might be something triggered from inside incident.io (e.g. a severity created as part of setup).\n\
\nAs an example:\n\n```\n\"actor\": {\n \"type\": \"system\",\n \"id\": \"incident_setup\",\n \"name\": \"incident.io\
\ (setup)\",\n \"metadata\": {}\n }\n```\n\n### Workflows\n\nThis is for changes triggered by a workflow: for example,\
\ a workflow that invites users to a private incident.\n\nAs an example:\n\n```\n\"actor\": {\n \"type\": \"workflow\"\
,\n \"id\": \"01G0J1EXE7AXZ2C93K61WBPYEH\",\n \"name\": \"Auto-invite security team to private incidents\",\n \
\ \"metadata\": {}\n }\n```\n\n### External resources\n\nThis is for changes triggered by a specific [external resource](https://api-docs.incident.io/tag/Incident-Attachments-V1)\
\ (also known as an attachment).\n\nAs an example:\n\n```\n\"actor\": {\n \"type\": \"external_resource\",\n \"\
id\": \"01G0J1EXE7AXZ2C93K61WBPYEH\",\n \"name\": \"#1234 Increased API latency\",\n \"metadata\": {\n \"external_resource_type\"\
: \"pager_duty_incident\",\n \"external_resource_external_id\": \"q1234\"\n }\n }\n```\n\n### Alerts\n\nThis\
\ is for changes triggered by a specific alert (e.g. from Datadog or Grafana).\n\nAs an example:\n\n```\n\"actor\": {\n\
\ \"type\": \"alert\",\n \"id\": \"01G0J1EXE7AXZ2C93K61WBPYEH\",\n \"name\": \"Staging: pod CPU high\",\n \
\ \"metadata\": {\n \"alert_source_id\": \"01HB0ZG3B0HM04RCXNSPV1EDYG\"\n }\n }\n```"
humanURL: https://incident.io
tags:
- Audit Logs
tags_raw:
- Audit logs
properties:
- type: OpenAPI
url: openapi/incident-io-audit-logs-api-openapi.yml
- aid: incident-io:incident-io-call-routes-v2-api
name: Incident.io Call Routes V2 API
description: 'View and manage call routes: phone numbers your customers can call to
reach whoever is on call.
Use these endpoints to read how a route is configured, and to change who it
pages, the language it speaks to callers, and which number responders see when
it calls them.
List and edit call routes here. Create and delete them in the dashboard.'
humanURL: https://incident.io
tags:
- Call Routes V2
properties:
- type: OpenAPI
url: openapi/incident-io-call-routes-v2-api-openapi.yml
- aid: incident-io:incident-io-call-sessions-v2-api
name: Incident.io Call Sessions V2 API
description: 'List Scribe call sessions.
Call sessions are the individual meetings Scribe attended: several can accumulate
over time. Use this endpoint together with Call Transcript Entries to export what
Scribe transcribed during each session.'
humanURL: https://incident.io
tags:
- Call Sessions V2
properties:
- type: OpenAPI
url: openapi/incident-io-call-sessions-v2-api-openapi.yml
- aid: incident-io:incident-io-call-transcript-entries-v2-api
name: Incident.io Call Transcript Entries V2 API
description: 'List the transcript entries Scribe captured during a call session.
Entries are returned oldest first, ordered by when each participant started
speaking. To export a full transcript, page through with ''page_size'' and ''after''
until the response no longer includes a ''pagination_meta.after'' value.'
humanURL: https://incident.io
tags:
- Call Transcript Entries V2
properties:
- type: OpenAPI
url: openapi/incident-io-call-transcript-entries-v2-api-openapi.yml
- aid: incident-io:incident-io-catalog-v2-api
name: Incident.io Catalog V2 API
description: "Manage and browse catalog resources.\n\nThese endpoints have been deprecated in favour of CatalogV3. The only\
\ breaking change is\nthat the 'manual' attribute mode is now split into 'api' and 'dashboard'. We also removed\nthe usage\
\ of some types that were deprecated in the V2 API. \n\nUse the incident.io catalog to track services, teams, product\
\ features and anything\nelse that helps build a map of your organisation. These different categories of thing\nbecome\
\ catalog types, and each instance (like a particular service or team) is a\ncatalog entry.\n\nEach type is made up of\
\ a series of attributes, and each attribute has a type. Types\ncan even have attributes that refer to other catalog types.\n\
\nWe automatically create catalog types when you connect an integration, such as GitHub\nrepositories or PagerDuty services\
\ and teams. You can use this API to create custom\ntypes, that are specifically tailored to your organisation.\n\nExamples\
\ might be a 'Service' type with an 'Alert channel' which you can point at a\nSlack channel, or 'Team' which specifies\
\ its 'Manager' and 'Technical Lead' as Slack\nusers. You can then use these types to create powerful new workflows.\n\
\nConsider using our official [catalog importer](https://github.com/incident-io/catalog-importer).\nIt can be used to\
\ sync catalog data from sources like local files or GitHub and push\nthem into the incident.io catalog without having\
\ to directly interact with our public API."
humanURL: https://incident.io
tags:
- Catalog V2
properties:
- type: OpenAPI
url: openapi/incident-io-catalog-v2-api-openapi.yml
- aid: incident-io:incident-io-catalog-v3-api
name: Incident.io Catalog V3 API
description: 'Manage and browse catalog resources.
Use the incident.io catalog to track services, teams, product features and anything
else that helps build a map of your organisation. These different categories of thing
become catalog types, and each instance (like a particular service or team) is a
catalog entry.
Each type is made up of a series of attributes, and each attribute has a type. Types
can even have attributes that refer to other catalog types.
We automatically create catalog types when you connect an integration, such as GitHub
repositories or PagerDuty services and teams. You can use this API to create custom
types, that are specifically tailored to your organisation.
Examples might be a ''Service'' type with an ''Alert channel'' which you can point at a
Slack channel, or ''Team'' which specifies its ''Manager'' and ''Technical Lead'' as Slack
users. You can then use these types to create powerful new workflows.
Consider using our official [catalog importer](https://github.com/incident-io/catalog-importer).
It can be used to sync catalog data from sources like local files or GitHub and push
them into the incident.io catalog without having to directly interact with our public API.'
humanURL: https://incident.io
tags:
- Catalog V3
properties:
- type: OpenAPI
url: openapi/incident-io-catalog-v3-api-openapi.yml
- aid: incident-io:incident-io-custom-field-options-v1-api
name: Incident.io Custom Field Options V1 API
description: 'Manage custom field options.
Single- and multi-select custom fields have a list of all available options,
which have a value, and a sort key. The value must be unique to the custom
field. For example, you might have an Incident Type custom field, with options
"Data breach", "Performance degradation", "API downtime", etc.'
humanURL: https://incident.io
tags:
- Custom Field Options V1
properties:
- type: OpenAPI
url: openapi/incident-io-custom-field-options-v1-api-openapi.yml
- aid: incident-io:incident-io-custom-fields-v1-api
name: Incident.io Custom Fields V1 API
description: 'Manage custom fields.
Custom fields are used to attach metadata to incidents, which you can use when searching
for incidents in the dashboard, triggering workflows, building announcement rules or for
your own data needs.
Each field has a type:
- Single-select, single value selected from a predefined list of options (e.g. Detection Method)
- Multi-select, as above but you can pick more than one option (e.g. Affected Teams)
- Text, freeform text field (e.g. Customer ID)
- Link, link URL that is synced to Slack bookmarks on the incident channel (e.g. External Status Page)
- Number, integer or fractional numbers (e.g. # Customers Affected)
We may add more custom field types in the future - we''d love to hear any other types you''d like to use!'
humanURL: https://incident.io
tags:
- Custom Fields V1
properties:
- type: OpenAPI
url: openapi/incident-io-custom-fields-v1-api-openapi.yml
# --- truncated at 32 KB (61 KB total) ---
# Full source: https://artifacts.apis.io/incident-io/apis.yml
Incident.io API — frequently asked questions
Does Incident.io have an API?
Yes. APIs.io lists 92 APIs from Incident.io, including Incident.io Actions API, Incident.io Alert Attributes API and Incident.io Alert Routes API, and 89 more.
Is there an OpenAPI specification for the Incident.io API?
Yes. APIs.io indexes 92 OpenAPI specifications for Incident.io, each linked for download from this page.
How do I authenticate with the Incident.io API?
Incident.io uses bearer-token authentication (http · 1 scheme). The details are profiled on APIs.io as Incident Io Authentication.
How much does the Incident.io API cost?
APIs.io lists 5 pricing plans for Incident.io, with each plan's price, limits and inclusions under Pricing on this page.
Does Incident.io have an MCP server?
Yes. APIs.io lists 1 MCP server for Incident.io: Remote MCP server at mcp.incident.io over HTTP.
Is the Incident.io API ready for AI agents?
Incident.io has a Kin Score of 33.8 out of 100 (thin) and an Agent Readiness score of 50.9 (agent-native), scored by API Evangelist on 2026-11-06.
Calls without X-API-Key need no key. Calls with it need a paid plan — get a key.
Get an API key
Free tier, no form to fill in. Signing in shares your email address with us — we
store it to create your key and to recognise you if you sign in with another
provider. See our Privacy Policy and
Terms.
 Kin Score
How this is scored →
 It updates itself when the score changes. Paste this where you link to your API docs: