Jentic is an AI infrastructure company building the agentic knowledge layer for APIs. Founded in late 2024 and backed by $4.5M in pre-seed funding, Jentic enables enterprises to confidently manage, scale, and govern AI agent initiatives in a unified platform built on open standards. The platform provides secure execution, managed authentication, unified permissions, and observability for AI agents accessing 1,500+ public APIs and 2,000+ agent-ready workflows. Jentic's bet is that AI agents need a standards-based control plane built on OpenAPI plus Arazzo workflows plus MCP, rather than ad-hoc tool wiring inside every agent framework. The platform ships the Jentic Public APIs catalog, the Arazzo Engine (workflow runner), the Standard Agent (a composable ReWOO-style reasoning agent), the Jentic Mini self-hosted execution layer, a hosted Remote MCP server at api.jentic.com/mcp, and the Jentic API AI-Readiness Framework (JAIRF) for scoring API readiness for agents.
Jentic publishes 39 API contracts indexed on the APIs.io network, including Authentication API, Execution API, Search API, and 36 more. Tagged areas include AI Agents, Arazzo, OpenAPI, MCP, and Workflows.
The Jentic catalog on APIs.io includes 1 JSON-LD context and 2 Spectral governance rulesets.
Jentic’s developer surface includes authentication, engineering blog, documentation, pricing, signup flow, developer console, YouTube channel, and 28 more developer resources.
Regulatory Posture applies to this provider. Its tags matched the
Horizontal (data, software, accessibility, platform) regime, so
Regulatory Posture carries 15 points of the composite.
If this regime is wrong for your business, say so on your
provider repo — the
applicability map is public and we will correct it.
Create-or-Update Ergonomics applies to this provider. This API accepts writes, so it
carries 10 points of the composite. It is scored from the published contracts
themselves: whether a caller can create-or-update in one call, whether the write accepts a key the caller already
holds, and whether the response says which branch ran. Without that, every write needs a search-and-branch in
front of it, and the first time that check is skipped a duplicate record is created.
Scored against the observed mean rather than raw — a provider at the catalog average is unchanged by this facet,
not penalised by it.
The six quality facets above are damped to 75 points between them,
because the conditional facet above carries the other
25. That is why each facet's contribution is shown against a damped
maximum: raising a quality facet moves the composite by 75% of its nominal
weight, not 100%. The full arithmetic is at apis.io/rating/.
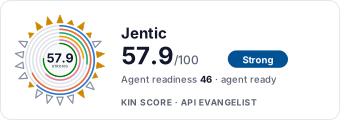
Show this score on your site.
It updates itself when the score changes. Paste this where you link to your API docs:
<a href="https://apis.io/providers/jentic/"><img src="https://apis.io/badge/jentic/card.svg" alt="Jentic on APIs.io — Kin Score by API Evangelist"></a>
Other styles, a README pill and a shields.io endpoint are on the badge page.
Raise your score.
Agent readiness — checks not met, largest first (exact, from this profile):
Idempotency+9 pts — OpenAPI mutating operations declare an idempotency key — a header, a request-body property, or a named de-duplication token whose own description says so (verified); else common[].type matches /idempoten/i (documented)
A2A Agent Card+8 pts — a2a/-a2a.yml manifest, graded on conformance.grade against A2A 1.0.0
Delegated User Identity+6 pts — a served discovery document listing authorization_code in grant_types_supported (served), else an oauth2 authorizationCode flow or openIdConnect declared in an OpenAPI (documented)
Typed Event Surface+6 pts — AsyncAPI document, OR webhooks/callbacks objects in the as-published OpenAPI, OR common[].type includes Webhooks
Protected Resource Metadata+5 pts — a served /.well-known/oauth-protected-resource carrying `resource` (documented), and naming its authorization_servers (verified)
4 more unmet checks in the Agent Readiness table above.
Kin Score — facets with the most composite points still available (weight × headroom):
The Kin Score Market layer reads a provider inside its market:
its position, and how deep its integrations go. Depth is only comparable within a position. Provisional and unweighted:
not part of the Kin Score or agent readiness.
Registered MCP server and declares compatibility are report only — not weighted.
Undeclared means we found nothing we can read, so there is no number: we never infer integrations.
Standards this provider implements or carries. De facto ones are profiled and measured by the API Commons; formal ones come from the standards directory and are linked by the provider's own tags. The evidence column says how each claim was established — not that it was made.
The Jentic Remote MCP Server is the hosted Model Context Protocol endpoint that exposes the Jentic catalog to MCP-capable clients (Claude Desktop, ChatGPT, Cursor, Windsurf, VS ...
Open-source Python engine that executes Arazzo workflow specifications alongside OpenAPI operation definitions. Powers the Jentic platform's workflow execution and is also insta...
Open-source composable reasoning agent framework that plans, acts, and recovers from failures, preconfigured with Jentic tools and a ReWOO reasoning loop. Primary entry point is...
Free, open-source, self-hosted API execution layer that sits between an agent and the outside world. The agent says what it wants to do and Jentic Mini handles the how: finding ...
Technical specification for evaluating how interpretable, operable, and trustworthy an API is for AI systems and autonomous agents. Defines the signals, dimensions, scoring mode...
Actor-agnostic, multi-item access-request surface (Core / Access bounded context). When an agent's brokered call is rejected by a permission rule — or the agent needs access it ...
Unified actor directory — a lightweight read-only view across all actor types (users, agents, service accounts). Returns ID-to-name mappings for UI cache hydration so dashboards...
Agent actors — autonomous principals that call the Broker. Covers the agent lifecycle (list, read, approve / deny, enable / disable, archive) and the toolkits bound to each agent.
Sub-resource of **APIs** (Registry bounded context). Enumerate the operations exposed by a registered API — either the live (`current_revision_id`) view or a specific revision. ...
Sub-resource of **APIs** (Registry bounded context). Download the underlying OpenAPI document for a registered API — either the live (`current_revision_id`) view or a specific r...
The `Api` aggregate root — what APIs are registered for this deployment, addressable by the loose `(vendor, name, version)` tuple. Every successful import lands a new immutable ...
Append-only administrative audit trail — who did what, when. Distinct from `Executions` (brokered upstream calls); this records control-plane mutations.
The public API **catalog** — a registry-side browse/preview/import surface over the Jentic public-APIs GitHub manifest. Powers the Discover experience: list importable APIs (`GE...
Runtime, DB-backed platform configuration. Lets an operator set, read, and list configuration that previously required hand-editing backend YAML and restarting the server — star...
Part of the **Core / Access** bounded context — the authoritative record of "who can call what, with which secret". A `Credential` is the auth secret + header configuration the ...
Curated, severity-tagged event stream surfaced to dashboards and operators. Each event is either **informational** (no action required, e.g. `import.completed`) or **actionable*...
Append-only audit log of every Broker call (sync or async) — timing, status, trace IDs, and the upstream API reference (`vendor:name:version`). Bodies are not stored. Records ar...
Identity introspection for the calling principal (human, agent, or service account) — `GET /me` returns the resolved subject, scopes, and permissions behind the presented token.
Resolve a single registered operation to its full structural detail — parameters, response schema, security scheme, server URL. Heavier than `Lookup` (which is the Broker hot pa...
In-flight async-job tracker for both Registry import jobs and Broker async-execution jobs — one uniform `Job` shape keyed by `kind`. Lifecycle only — type-specific result payloa...
MCP (Model Context Protocol) transport reporting. The `jentic mcp` stdio server terminates all MCP protocol traffic locally; the control plane only sees plain HTTP. This tag cov...
Dashboard-oriented aggregation endpoints — execution volume, success/failure ratios, and top operations over a bounded time window. Results are cached in-process (TTL ~120 s) so...
Free-form annotations attached to registry resources — an `Api`, an `ApiRevision`, a registered `operation_id`, an `ExecutionRecord`, or a `Credential`. Used to capture human or...
OAuth 2.0 / OIDC endpoints exposed by the platform authorization server — the authorize, token, introspection, revocation, and assertion-mint endpoints plus the redirect callback.
Admin-managed registry of third-party OAuth clients (confidential, secret-bearing). Registered clients integrate with Jentic One via the standard Authorization Code + PKCE flow....
OpenAPI Overlay 1.0 (`https://spec.openapis.org/overlay/v1.0.0`) documents that correct an imported spec without rewriting it. Overlays capture wrong required fields, missing se...
Part of the **Admin / Audit** bounded context — the catalogue of grantable permission strings. Permissions are namespaced `resource:action` strings (`users:write`, `capabilities...
Operational endpoints for service health and platform tooling. Not part of any bounded context — surfaced here so orchestrators and load balancers have a stable probe target.
Sub-resource of **Toolkits** (Core / Access bounded context). A toolkit doesn't own credentials directly — it **binds** to credentials that already exist in `/credentials`. The ...
Sub-resource of **Toolkits** (Core / Access bounded context). A toolkit can hold many API keys at once — different agents, machines, or environments typically each get their own...
Part of the **Core / Access** bounded context — a `Toolkit` is a scoped bundle of credentials and permissions issued to an agent or service. This tag covers **toolkit lifecycle*...
Part of the **Admin / Audit** bounded context — the human roster of the organisation. One organisation, many users; admin surfaces here cover create / list / read / update / del...
aid: jentic
url: https://raw.githubusercontent.com/api-evangelist/jentic/refs/heads/main/apis.yml
name: Jentic
description: Jentic is an AI infrastructure company building the agentic knowledge layer for APIs. Founded in late 2024 and
  backed by $4.5M in pre-seed funding, Jentic enables enterprises to confidently manage, scale, and govern AI agent initiatives
  in a unified platform built on open standards. The platform provides secure execution, managed authentication, unified permissions,
  and observability for AI agents accessing 1,500+ public APIs and 2,000+ agent-ready workflows. Jentic's bet is that AI agents
  need a standards-based control plane built on OpenAPI plus Arazzo workflows plus MCP, rather than ad-hoc tool wiring inside
  every agent framework. The platform ships the Jentic Public APIs catalog, the Arazzo Engine (workflow runner), the Standard
  Agent (a composable ReWOO-style reasoning agent), the Jentic Mini self-hosted execution layer, a hosted Remote MCP server
  at api.jentic.com/mcp, and the Jentic API AI-Readiness Framework (JAIRF) for scoring API readiness for agents.
deliveryModel:
  model: saas
  license_evidence:
    not_product:
    - jentic/api-ai-readiness-framework
    - jentic/arazzo-engine
    - jentic/jentic-mini
    - jentic/standard-agent
  open_source: unknown
  commercial: true
  callable_host: true
  label: Hosted service · you call their endpoint
  confidence: low
  source:
  - openapi
  - pricing
  - repository-not-product
  generated: '2026-09-25'
  method: derived
accessModel:
  pricing: enterprise
  onboarding: unknown
  trial: false
  try_now: false
  public: false
  label: Enterprise
  confidence: medium
  source:
  - plans
  - authentication
  - security
  generated: '2026-11-06'
  method: derived
image: https://kinlane-images.s3.amazonaws.com/shared/apis-json/icons/jentic.png
type: Index
access: 3rd-Party
position: Consuming
created: '2026-01-02'
modified: '2026-05-19'
x-docs-platform: mkdocs
x-docs-platform-confidence: medium
x-docs-platform-checked: 2026-10-03
tags:
- AI Agents
- Arazzo
- OpenAPI
- MCP
- Workflows
- Integration
- Agent Runtime
- Standard Agent
- Just In Time Tooling
- Credential Vault
- Agent Governance
- Observability
- API AI Readiness
tags_raw:
- AI Agents
- Arazzo
- OpenAPI
- MCP
- Workflows
- Integrations
- Agent Runtime
- Standard Agent
- Just In Time Tooling
- Credential Vault
- Agent Governance
- Observability
- API AI Readiness
segments:
- AI Agents
- Workflows
- Integrations
- MCP
- Agent Infrastructure
specificationVersion: '0.23'
apis:
- aid: jentic:jentic-mcp
  name: Jentic Remote MCP Server
  humanURL: https://docs.jentic.com/guides/mcp/remote-mcp/
  baseURL: https://api.jentic.com/mcp
  description: The Jentic Remote MCP Server is the hosted Model Context Protocol endpoint that exposes the Jentic catalog
    to MCP-capable clients (Claude Desktop, ChatGPT, Cursor, Windsurf, VS Code). It speaks the same search / load / execute
    pattern as the Jentic API, but packaged as MCP tools. Supports OAuth 2.0 with PKCE and dynamic client registration, with
    an API key fallback for Cursor and Windsurf.
  tags:
  - MCP
  - AI Agents
  - OAuth
  - Remote MCP
  - Authentication
  tags_raw:
  - MCP
  - AI Agents
  - OAuth
  - Remote MCP
  - Authentication
  properties:
  - url: https://docs.jentic.com/guides/mcp/
    type: Documentation
  - url: https://docs.jentic.com/guides/mcp/remote-mcp/
    type: GettingStarted
  - url: https://api.jentic.com/mcp
    type: BaseURL
  properties_authentication:
  - name: OAuth 2.0
    scheme: oauth2
    notes: Recommended. PKCE supported. Automatic token refresh. Dynamic client registration. Used by Claude Desktop, ChatGPT,
      Cursor, Windsurf.
  - name: API Key
    scheme: apiKey
    notes: Fallback for Cursor and Windsurf. Uses an agent-scoped Jentic API key (JENTIC_AGENT_API_KEY).
  properties_features:
  - name: search_apis Tool
    description: Lists matching APIs and workflows for a natural language query.
  - name: load_execution_info Tool
    description: Returns the schema and auth requirements for a chosen operation.
  - name: execute Tool
    description: Executes an operation or workflow with managed credentials.
  - name: list_credentials Resource
    description: Lists the agent's available upstream credentials.
- aid: jentic:arazzo-engine
  name: Arazzo Engine
  humanURL: https://github.com/jentic/arazzo-engine
  description: Open-source Python engine that executes Arazzo workflow specifications alongside OpenAPI operation definitions.
    Powers the Jentic platform's workflow execution and is also installable standalone as arazzo-runner for direct use in
    agents and automation. Handles authentication resolution (API key, OAuth 2.0, basic, bearer), dynamic server URL resolution,
    parameter chaining between steps, and blob storage for large binary payloads.
  tags:
  - Arazzo
  - OpenAPI
  - Workflows
  - Open Source
  tags_raw:
  - Arazzo
  - OpenAPI
  - Workflows
  - Open Source
  - Open-Source
  properties:
  - url: https://github.com/jentic/arazzo-engine
    type: SourceCode
  - url: https://docs.jentic.com/getting-started/arazzo-runner/
    type: Documentation
  - url: https://pypi.org/project/arazzo-runner/
    type: PythonPackage
- aid: jentic:standard-agent
  name: Jentic Standard Agent
  humanURL: https://github.com/jentic/standard-agent
  description: Open-source composable reasoning agent framework that plans, acts, and recovers from failures, preconfigured
    with Jentic tools and a ReWOO reasoning loop. Primary entry point is the ReWOOAgent Python class. Bring-your-own LLM (Anthropic,
    OpenAI, Google). Demonstrates how to build an agent that uses Jentic's just-in-time tooling without committing to a specific
    agent framework.
  tags:
  - Agent Framework
  - ReWOO
  - Open Source
  - Python
  tags_raw:
  - Agent Framework
  - ReWOO
  - Open Source
  - Python
  - Open-Source
  properties:
  - url: https://github.com/jentic/standard-agent
    type: SourceCode
  - url: https://docs.jentic.com/getting-started/standard-agent/
    type: Documentation
- aid: jentic:jentic-mini
  name: Jentic Mini
  humanURL: https://github.com/jentic/jentic-mini
  description: 'Free, open-source, self-hosted API execution layer that sits between an agent and the outside world. The agent
    says what it wants to do and Jentic Mini handles the how: finding the right API, injecting credentials at runtime, and
    brokering the request. Intended for teams that want Jentic''s execution model without sending traffic through the hosted
    Jentic API.'
  tags:
  - Self-Hosted
  - Open Source
  - Agent Runtime
  tags_raw:
  - Self Hosted
  - Open Source
  - Agent Runtime
  - Open-Source
  properties:
  - url: https://github.com/jentic/jentic-mini
    type: SourceCode
- aid: jentic:jairf
  name: Jentic API AI-Readiness Framework (JAIRF)
  humanURL: https://github.com/jentic/api-ai-readiness-framework
  description: Technical specification for evaluating how interpretable, operable, and trustworthy an API is for AI systems
    and autonomous agents. Defines the signals, dimensions, scoring model, and normalization rules used by the Jentic API
    Scorecard product. Apache 2.0.
  tags:
  - Specification
  - API AI Readiness
  - Open Source
  tags_raw:
  - Specification
  - API AI Readiness
  - Open Source
  - Open-Source
  properties:
  - url: https://github.com/jentic/api-ai-readiness-framework
    type: SourceCode
- aid: jentic:jentic-authentication-api
  name: Jentic Authentication API
  description: Registration and API key management for accessing the Jentic platform.
  humanURL: https://docs.jentic.com/reference/public-apis/
  baseURL: https://api.jentic.com/api/v1
  tags:
  - Authentication
  properties:
  - type: OpenAPI
    url: openapi/jentic-authentication-api-openapi.yml
  - type: Website
    url: https://jentic.com/
  - type: Documentation
    url: https://docs.jentic.com/
  - type: GettingStarted
    url: https://docs.jentic.com/getting-started/quickstart/
  - type: APIReference
    url: https://docs.jentic.com/reference/public-apis/
  - type: Signup
    url: https://app.jentic.com/sign-up
  - type: Console
    url: https://app.jentic.com/
  - type: BaseURL
    url: https://api.jentic.com/api/v1
  - type: SpectralRules
    url: rules/jentic-rules.yml
  - type: JSONSchema
    url: json-schema/jentic-operation-schema.json
  - type: JSONSchema
    url: json-schema/jentic-agent-schema.json
  - type: JSONSchema
    url: json-schema/jentic-workflow-schema.json
  - type: JSONStructure
    url: json-structure/jentic-operation-structure.json
  - type: Examples
    url: examples/jentic-search-example.json
  - type: Examples
    url: examples/jentic-load-example.json
  - type: Examples
    url: examples/jentic-execute-example.json
  - type: Examples
    url: examples/jentic-register-example.json
- aid: jentic:jentic-execution-api
  name: Jentic Execution API
  description: Load execution details and execute API operations or Arazzo workflows with managed authentication and credential
    injection.
  humanURL: https://docs.jentic.com/reference/public-apis/
  baseURL: https://api.jentic.com/api/v1
  tags:
  - Execution
  properties:
  - type: OpenAPI
    url: openapi/jentic-execution-api-openapi.yml
  - type: Website
    url: https://jentic.com/
  - type: Documentation
    url: https://docs.jentic.com/
  - type: GettingStarted
    url: https://docs.jentic.com/getting-started/quickstart/
  - type: APIReference
    url: https://docs.jentic.com/reference/public-apis/
  - type: Signup
    url: https://app.jentic.com/sign-up
  - type: Console
    url: https://app.jentic.com/
  - type: BaseURL
    url: https://api.jentic.com/api/v1
  - type: SpectralRules
    url: rules/jentic-rules.yml
  - type: JSONSchema
    url: json-schema/jentic-operation-schema.json
  - type: JSONSchema
    url: json-schema/jentic-agent-schema.json
  - type: JSONSchema
    url: json-schema/jentic-workflow-schema.json
  - type: JSONStructure
    url: json-structure/jentic-operation-structure.json
  - type: Examples
    url: examples/jentic-search-example.json
  - type: Examples
    url: examples/jentic-load-example.json
  - type: Examples
    url: examples/jentic-execute-example.json
  - type: Examples
    url: examples/jentic-register-example.json
- aid: jentic:jentic-search-api
  name: Jentic Search API
  description: Semantic search over the Jentic API and workflow catalog using natural language queries.
  humanURL: https://docs.jentic.com/reference/public-apis/
  baseURL: https://api.jentic.com/api/v1
  tags:
  - Search
  properties:
  - type: OpenAPI
    url: openapi/jentic-search-api-openapi.yml
  - type: Website
    url: https://jentic.com/
  - type: Documentation
    url: https://docs.jentic.com/
  - type: GettingStarted
    url: https://docs.jentic.com/getting-started/quickstart/
  - type: APIReference
    url: https://docs.jentic.com/reference/public-apis/
  - type: Signup
    url: https://app.jentic.com/sign-up
  - type: Console
    url: https://app.jentic.com/
  - type: BaseURL
    url: https://api.jentic.com/api/v1
  - type: SpectralRules
    url: rules/jentic-rules.yml
  - type: JSONSchema
    url: json-schema/jentic-operation-schema.json
  - type: JSONSchema
    url: json-schema/jentic-agent-schema.json
  - type: JSONSchema
    url: json-schema/jentic-workflow-schema.json
  - type: JSONStructure
    url: json-structure/jentic-operation-structure.json
  - type: Examples
    url: examples/jentic-search-example.json
  - type: Examples
    url: examples/jentic-load-example.json
  - type: Examples
    url: examples/jentic-execute-example.json
  - type: Examples
    url: examples/jentic-register-example.json
- aid: jentic:jentic-access-requests-api
  name: Jentic Access Requests API
  description: 'Actor-agnostic, multi-item access-request surface (Core / Access bounded context). When an agent''s brokered
    call is rejected by a permission rule — or the agent needs access it doesn''t yet have — the agent files an `AccessRequest`
    containing one or more line items (`AccessRequestItem`). The request enters `pending` state and surfaces an `approve_url`
    that the agent presents to a human reviewer.


    Reviewers `:decide` individual items (approve or deny each); filers can `:amend` pending items (adjust rules or target)
    or `:withdraw` the entire request. Each item transitions independently; the envelope status reflects the aggregate (`pending`
    while any item is pending, `partially_approved` when some items are decided but others remain, terminal once all items
    resolve).


    Pending requests carry a TTL (default 7 days, configurable). Envelope lifecycle: `pending → partially_approved → approved
    | denied | withdrawn | expired`.


    **Identity scoping.** List and get operations are identity-scoped: filers see their own requests, reviewers see their
    inbox, `org:admin` sees all. Non-owners receive `404` (not `403`) to avoid leaking existence.


    **Security.** Mutating operations (`POST`, `:decide`, `:amend`, `:withdraw`) require `agents:write`; read operations require
    `agents:read`.'
  humanURL: https://docs.jentic.com/guides/mcp/remote-mcp/
  baseURL: https://api.jentic.com/mcp
  tags:
  - Access Requests
  properties:
  - type: OpenAPI
    url: openapi/jentic-access-requests-api-openapi.yml
- aid: jentic:jentic-actors-api
  name: Jentic Actors API
  description: Unified actor directory — a lightweight read-only view across all actor types (users, agents, service accounts).
    Returns ID-to-name mappings for UI cache hydration so dashboards can display friendly names wherever an `actor_id` appears.
  humanURL: https://docs.jentic.com/guides/mcp/remote-mcp/
  baseURL: https://api.jentic.com/mcp
  tags:
  - Actors
  properties:
  - type: OpenAPI
    url: openapi/jentic-actors-api-openapi.yml
- aid: jentic:jentic-agent-registration-api
  name: Jentic Agent Registration API
  description: Dynamic agent registration (RFC 7591-style) — register a new agent client, poll registration status, update,
    or delete a registration.
  humanURL: https://docs.jentic.com/guides/mcp/remote-mcp/
  baseURL: https://api.jentic.com/mcp
  tags:
  - Agent Registration
  properties:
  - type: OpenAPI
    url: openapi/jentic-agent-registration-api-openapi.yml
- aid: jentic:jentic-agents-api
  name: Jentic Agents API
  description: Agent actors — autonomous principals that call the Broker. Covers the agent lifecycle (list, read, approve
    / deny, enable / disable, archive) and the toolkits bound to each agent.
  humanURL: https://docs.jentic.com/guides/mcp/remote-mcp/
  baseURL: https://api.jentic.com/mcp
  tags:
  - Agents
  properties:
  - type: OpenAPI
    url: openapi/jentic-agents-api-openapi.yml
- aid: jentic:jentic-api-operations-api
  name: Jentic API Operations API
  description: 'Sub-resource of **APIs** (Registry bounded context). Enumerate the operations exposed by a registered API
    — either the live (`current_revision_id`) view or a specific revision. Complements `Search` (ranked discovery) and `Inspect`
    (single-operation detail) by giving callers the deterministic list of every registered operation under one API without
    ranking, paging through `Search`, or parsing the spec.


    Each row is slim — the structural detail (parameters, response schema, security scheme) lives behind `_links.inspect`
    for callers that need it.'
  humanURL: https://docs.jentic.com/guides/mcp/remote-mcp/
  baseURL: https://api.jentic.com/mcp
  tags:
  - API Operations
  properties:
  - type: OpenAPI
    url: openapi/jentic-api-operations-api-openapi.yml
- aid: jentic:jentic-api-spec-api
  name: Jentic API Spec API
  description: 'Sub-resource of **APIs** (Registry bounded context). Download the underlying OpenAPI document for a registered
    API — either the live (`current_revision_id`) view or a specific revision. Supports `application/json`, `application/openapi+yaml`,
    and `application/yaml` via `Accept`-header content negotiation, with `Content-Disposition: attachment; filename="..."`
    so browser downloads work cleanly.


    By default the response includes any deployment-local overlays merged on top of the imported base. Pass `?overlays=false`
    to download the raw imported spec instead.'
  humanURL: https://docs.jentic.com/guides/mcp/remote-mcp/
  baseURL: https://api.jentic.com/mcp
  tags:
  - API Spec
  properties:
  - type: OpenAPI
    url: openapi/jentic-api-spec-api-openapi.yml
- aid: jentic:jentic-apis-api
  name: Jentic APIs API
  description: 'The `Api` aggregate root — what APIs are registered for this deployment, addressable by the loose `(vendor,
    name, version)` tuple. Every successful import lands a new immutable `ApiRevision`; the `Api` carries the live `current_revision_id`
    plus presentation metadata (`display_name`, `description`, `icon_url`).


    Mutation surfaces:


    - `POST /apis` — async import (url / inline). Returns 202 + `Job (kind=import)`.

    - `PATCH /apis/{vendor}/{name}/{version}` — metadata-only updates (display name, description, icon). Cannot mutate revisions
    or spec content.

    - `POST /apis/{vendor}/{name}/{version}/revisions/{revision_id}:promote` — make a draft revision live.

    - `POST /apis/{vendor}/{name}/{version}/revisions/{revision_id}:archive` — retire a draft revision.

    - `DELETE /apis/{vendor}/{name}/{version}` — deregister the API and all its revisions.


    Newly imported revisions are **never auto-promoted** — callers must explicitly `:promote` to flip the live pointer. Hot-path
    Broker calls can pin to a specific revision via the `Jentic-Revision` request header for testing without flipping the
    pointer.


    Sub-resources of an `Api` live under sibling tags: `API Operations` enumerates the operations exposed by a registered
    revision; `API Spec` returns the underlying OpenAPI document for tooling.'
  humanURL: https://docs.jentic.com/guides/mcp/remote-mcp/
  baseURL: https://api.jentic.com/mcp
  tags:
  - APIs
  properties:
  - type: OpenAPI
    url: openapi/jentic-apis-api-openapi.yml
- aid: jentic:jentic-audit-api
  name: Jentic Audit API
  description: Append-only administrative audit trail — who did what, when. Distinct from `Executions` (brokered upstream
    calls); this records control-plane mutations.
  humanURL: https://docs.jentic.com/guides/mcp/remote-mcp/
  baseURL: https://api.jentic.com/mcp
  tags:
  - Audit
  properties:
  - type: OpenAPI
    url: openapi/jentic-audit-api-openapi.yml
- aid: jentic:jentic-catalog-api
  name: Jentic Catalog API
  description: 'The public API **catalog** — a registry-side browse/preview/import surface over the Jentic public-APIs GitHub
    manifest. Powers the Discover experience: list importable APIs (`GET /catalog`, keyset cursor-paginated), preview an entry''s
    operations (`GET /catalog/{api_id}/operations`), refresh the cached manifest (`POST /catalog:refresh`, `org:admin`), and
    import an entry into the local registry (`POST /catalog/{api_id}:import`).


    The catalog is a cache of an upstream document, distinct from the local registry (`GET /apis`): `/apis` is what this deployment
    has imported, `/catalog` is what it *could* import. Each entry''s `registered` flag reflects whether its `spec_url` already
    backs a local API revision. Import resolves to a plain fetchable spec URL and reuses the standard async import job — no
    catalog identity ever crosses into the importer.'
  humanURL: https://docs.jentic.com/guides/mcp/remote-mcp/
  baseURL: https://api.jentic.com/mcp
  tags:
  - Catalog
  properties:
  - type: OpenAPI
    url: openapi/jentic-catalog-api-openapi.yml
- aid: jentic:jentic-configuration-api
  name: Jentic Configuration API
  description: Runtime, DB-backed platform configuration. Lets an operator set, read, and list configuration that previously
    required hand-editing backend YAML and restarting the server — starting with credential provider configs (e.g. Pipedream).
    A successful write rebuilds the in-process provider registry so the change takes effect without a restart. Secret fields
    (e.g. `client_secret`) are encrypted at rest and redacted on read. **Topology note:** in the combined (single-process)
    deployment a write takes effect immediately for all surfaces. In a multi-process deployment the control/broker processes
    pick up the new config at their next boot, not the instant the admin write lands; cross-process propagation is a tracked
    follow-up.
  humanURL: https://docs.jentic.com/guides/mcp/remote-mcp/
  baseURL: https://api.jentic.com/mcp
  tags:
  - Configuration
  properties:
  - type: OpenAPI
    url: openapi/jentic-configuration-api-openapi.yml
- aid: jentic:jentic-credentials-api
  name: Jentic Credentials API
  description: Part of the **Core / Access** bounded context — the authoritative record of "who can call what, with which
    secret". A `Credential` is the auth secret + header configuration the Broker injects on the way out to an upstream API.
    Credentials reference registry content via the loose `(vendor, name, version)` identity tuple (see `APIReference`) — there
    is no foreign key between Core and Registry, by design. Cleartext secret material is returned **exactly once** at creation
    (and on rotation via `PATCH`). Read paths return a redacted projection — last-N characters, hints, never the secret itself.
  humanURL: https://docs.jentic.com/guides/mcp/remote-mcp/
  baseURL: https://api.jentic.com/mcp
  tags:
  - Credentials
  properties:
  - type: OpenAPI
    url: openapi/jentic-credentials-api-openapi.yml
- aid: jentic:jentic-discovery-api
  name: Jentic Discovery API
  description: Unauthenticated metadata discovery — the JWKS document and OAuth authorization server metadata under `/.well-known/*`.
  humanURL: https://docs.jentic.com/guides/mcp/remote-mcp/
  baseURL: https://api.jentic.com/mcp
  tags:
  - Discovery
  properties:
  - type: OpenAPI
    url: openapi/jentic-discovery-api-openapi.yml
- aid: jentic:jentic-events-api
  name: Jentic Events API
  description: Curated, severity-tagged event stream surfaced to dashboards and operators. Each event is either **informational**
    (no action required, e.g. `import.completed`) or **actionable** (requires operator follow-up, e.g. `credential.expiring_soon`,
    `execution.repeated_failure`). Events reference the underlying `ExecutionRecord` or `Job` via `_links` and share `trace_id`
    for correlation. Subscribe live via `GET /events/stream` (Server-Sent Events) or poll `GET /events` with a `since=` filter.
  humanURL: https://docs.jentic.com/guides/mcp/remote-mcp/
  baseURL: https://api.jentic.com/mcp
  tags:
  - Events
  properties:
  - type: OpenAPI
    url: openapi/jentic-events-api-openapi.yml
- aid: jentic:jentic-executions-api
  name: Jentic Executions API
  description: Append-only audit log of every Broker call (sync or async) — timing, status, trace IDs, and the upstream API
    reference (`vendor:name:version`). Bodies are not stored. Records are written by the Broker; this surface is read-only.
    To walk the history of a single logical request that fanned out into multiple upstream calls, list with `?trace_id={trace_id}`.
  humanURL: https://docs.jentic.com/guides/mcp/remote-mcp/
  baseURL: https://api.jentic.com/mcp
  tags:
  - Executions
  properties:
  - type: OpenAPI
    url: openapi/jentic-executions-api-openapi.yml
- aid: jentic:jentic-identity-api
  name: Jentic Identity API
  description: Identity introspection for the calling principal (human, agent, or service account) — `GET /me` returns the
    resolved subject, scopes, and permissions behind the presented token.
  humanURL: https://docs.jentic.com/guides/mcp/remote-mcp/
  baseURL: https://api.jentic.com/mcp
  tags:
  - Identity
  properties:
  - type: OpenAPI
    url: openapi/jentic-identity-api-openapi.yml
- aid: jentic:jentic-inspect-api
  name: Jentic Inspect API
  description: Resolve a single registered operation to its full structural detail — parameters, response schema, security
    scheme, server URL. Heavier than `Lookup` (which is the Broker hot path) and separate from `Search` (which only returns
    ranked summaries). Supports JSON, Markdown, and OpenAPI YAML response formats via `Accept`-header content negotiation.
  humanURL: https://docs.jentic.com/guides/mcp/remote-mcp/
  baseURL: https://api.jentic.com/mcp
  tags:
  - Inspect
  properties:
  - type: OpenAPI
    url: openapi/jentic-inspect-api-openapi.yml
- aid: jentic:jentic-jobs-api
  name: Jentic Jobs API
  description: In-flight async-job tracker for both Registry import jobs and Broker async-execution jobs — one uniform `Job`
    shape keyed by `kind`. Lifecycle only — type-specific result payloads (the imported revisions for `import`, upstream response
    body for `execution`) live under `/jobs/{job_id}/result`. Result availability follows the organisation-level retention
    policy (one-shot or TTL); once that expires, both `/jobs/{job_id}` and `/jobs/{job_id}/result` `404`.
  humanURL: https://docs.jentic.com/guides/mcp/remote-mcp/
  baseURL: https://api.jentic.com/mcp
  tags:
  - Jobs
  properties:
  - type: OpenAPI
    url: openapi/jentic-jobs-api-openapi.yml
- aid: jentic:jentic-mcp-api
  name: Jentic MCP API
  description: MCP (Model Context Protocol) transport reporting. The `jentic mcp` stdio server terminates all MCP protocol
    traffic locally; the control plane only sees plain HTTP. This tag covers the small reporting surface behind it — today,
    the config-registration report `jentic setup`/`jentic skill init` send after writing an MCP server entry for a detected
    agent runtime, which feeds the config-written → first-session → first-execute adoption funnel.
  humanURL: https://docs.jentic.com/guides/mcp/remote-mcp/
  baseURL: https://api.jentic.com/mcp
  tags:
  - MCP
  properties:
  - type: OpenAPI
    url: openapi/jentic-mcp-api-openapi.yml
- aid: jentic:jentic-monitoring-api
  name: Jentic Monitoring API
  description: Dashboard-oriented aggregation endpoints — execution volume, success/failure ratios, and top operations over
    a bounded time window. Results are cached in-process (TTL ~120 s) so concurrent dashboard viewers never stampede the database.
  humanURL: https://docs.jentic.com/guides/mcp/remote-mcp/
  baseURL: https://api.jentic.com/mcp
  tags:
  - Monitoring
  properties:
  - type: OpenAPI
    url: openapi/jentic-monitoring-api-openapi.yml
- aid: jentic:jentic-notes-api
  name: Jentic Notes API
  description: 'Free-form annotations attached to registry resources — an `Api`, an `ApiRevision`, a registered `operation_id`,
    an `ExecutionRecord`, or a `Credential`. Used to capture human or agent observations about quirks: *"this endpoint silently
    truncates email addresses to 64 chars"*, *"this credential rejects calls outside US business hours"*, *"this operation
    needs `Accept: application/json` even though the spec doesn''t say so"*.


    Notes are an information surface for agents — they accumulate over time as the platform learns from real executions and
    surface back through `_links.notes` on the resources they annotate (woven in by individual surfaces as they need it).


    **Edit model.** Notes are editable via `PATCH`; each successful edit bumps a monotonic `revision` counter on the `Note`.
    Use the `If-Match` header on `PATCH` and `DELETE` to guard against concurrent modification.


    **Confidence promotion.** Notes carry both a `confidence` value (`observed | suspected | verified`) and a `confidence_source`
    (`client | platform_promoted`). Today only `client` is written by callers; the `platform_promoted` value is reserved for
    a future surface that auto-promotes `observed` notes to `verified` once enough matching `execution_feedback` accumulates.


    **Authentication.** Any authenticated principal (agent or human) can post any note type. Per-type policy (e.g. only humans
    may file `correction`) is enforced platform-side and not modelled in the spec.'
  humanURL: https://docs.jentic.com/guides/mcp/remote-mcp/
  baseURL: https://api.jentic.com/mcp
  tags:
  - Notes
  properties:
  - type: OpenAPI
    url: openapi/jentic-notes-api-openapi.yml
- aid: jentic:jentic-oauth-api
  name: Jentic OAuth API
  description: OAuth 2.0 / OIDC endpoints exposed by the platform authorization server — the authorize, token, introspection,
    revocation, and assertion-mint endpoints plus the redirect callback.
  humanURL: https://docs.jentic.com/guides/mcp/remote-mcp/
  baseURL: https://api.jentic.com/mcp
  tags:
  - OAuth
  properties:
  - type: OpenAPI
    url: openapi/jentic-oauth-api-openapi.yml
- aid: jentic:jentic-oauth-clients-api
  name: Jentic OAuth Clients API
  description: Admin-managed registry of third-party OAuth clients (confidential, secret-bearing). Registered clients integrate
    with Jentic One via the standard Authorization Code + PKCE flow. Admins can create, list, update, rotate secrets, and
    deactivate clients. Deactivating a client immediately invalidates all tokens issued through it.
  humanURL: https://docs.jentic.com/guides/mcp/remote-mcp/
  baseURL: https://api.jentic.com/mcp
  tags:
  - OAuth Clients
  properties:
  - type: OpenAPI
    url: openapi/jentic-oauth-clients-api-openapi.yml
- aid: jentic:jentic-overlays-api
  name: Jentic Overlays API
  description: 'OpenAPI Overlay 1.0 (`https://spec.openapis.org/overlay/v1.0.0`) documents that correct an imported spec without
    rewriting it. Overlays capture wrong required fields, missing security schemes, undocumented headers, silent payload truncation,
    and other places where the upstream spec disagrees with the upstream API''s actual behaviour — without forking the spec
    or waiting for an upstream fix.


    Overlays attach to the `Api` aggregate (not to a specific `ApiRevision`) and continue to apply across revision bumps until
    materially superseded. The optional `target_revision_id` records the revision the overlay was authored against, for auditing.


    **Lifecycle.** New overlays start in `pending`. The Broker calls `POST /apis/{vendor}/{name}/{version}/overlays/{overlay_id}:confirm`
    after the first successful upstream execution that exercised an overlay-patched operation, transitioning the overlay to
    `confirmed`. This is the platform''s only documented data-plane → control-plane writeback. Once `confirmed`, an overlay
    stays `confirmed` — repeated `:confirm` calls return `200` with the existing record unchanged.


    **Edit model.** Overlay documents are editable via `PATCH` only while `pending`. Once `confirmed` (or `deprecated`), the
    document is immutable — to change a confirmed overlay, submit a new one and let the old one age out via `DELETE` (which
    soft-deprecates).


    **Deletion.** `DELETE` is a **soft-deprecation** — the row is preserved with `status: deprecated` for audit. Deprecated
    overlays no longer apply to spec-download merges (`?overlays=false` becomes the default for that overlay) but stay queryable
    via `GET`. There is no hard-delete in this surface.


    **Authentication.** Any authenticated principal (agent or human) can submit, edit, confirm, or deprecate overlays. Platform-side
    rate limits gate abuse.'
  humanURL: https://docs.jentic.com/guides/mcp/remote-mcp/
  baseURL: https://api.jentic.com/mcp
  tags:
  - Overlays
  properties:
  - type: OpenAPI
    url: openapi/jentic-overlays-api-openapi.yml


# --- truncated at 32 KB (43 KB total) ---
# Full source: https://artifacts.apis.io/jentic/apis.yml
Jentic API — frequently asked questions
Does Jentic have an API?
Yes. APIs.io lists 39 APIs from Jentic, including Jentic Remote MCP Server, Arazzo Engine and Jentic Standard Agent, and 36 more.
Is there an OpenAPI specification for the Jentic API?
Yes. APIs.io indexes 34 OpenAPI specifications for Jentic, each linked for download from this page.
How do I authenticate with the Jentic API?
Jentic uses bearer-token authentication (apiKey · 1 scheme). The details are profiled on APIs.io as Jentic Authentication.
How much does the Jentic API cost?
Jentic publishes its prices; its Jentic One Enterprise plan is Usage-based as of 2026-10-28. APIs.io lists 3 pricing plans for Jentic, with each plan's price, limits and inclusions under Pricing on this page.
Does Jentic have an MCP server?
Yes. APIs.io lists 1 MCP server for Jentic: Remote MCP server at api.jentic.com over HTTP; 4 tools listed.
Is the Jentic API ready for AI agents?
Jentic has a Kin Score of 57.9 out of 100 (strong) and an Agent Readiness score of 45.9 (agent-ready), scored by API Evangelist on 2026-11-06.
Calls without X-API-Key need no key. Calls with it need a paid plan — get a key.
Get an API key
Free tier, no form to fill in. Signing in shares your email address with us — we
store it to create your key and to recognise you if you sign in with another
provider. See our Privacy Policy and
Terms.
 Kin Score
How this is scored →
 It updates itself when the score changes. Paste this where you link to your API docs: