Defakto Security
Defakto (formerly SPIRL) is a non-human identity (NHI) security company that issues short-lived, cryptographically attested identities to workloads, services, CI/CD pipelines and AI agents in place of static secrets, API keys and long-lived service accounts. The platform is built on SPIFFE and ships two products: Mint, which runs Trust Domain Servers and Agents that mint X.509-SVIDs, JWT-SVIDs and proof-of-possession WIT-SVIDs for Kubernetes, Linux, Docker and serverless workloads under a dozen attestation methods; and Ledger, which discovers, risk-scores and eradicates static secrets across AWS, Azure, GCP, Kubernetes, Anthropic, OpenAI, Bedrock AgentCore and Gemini. The control plane is driven by a gRPC management API and the spirlctl CLI, with a Go SDK, an OpenTofu/Terraform provider, workload identity federation into AWS/Azure/GCP, and OCSF 1.8.0 audit logging.
Defakto Security is listed with 2 APIs on the APIs.io network. Tagged areas include Security, Identity, Non-Human Identity, Workload Identity, and SPIFFE.
The Defakto Security catalog on APIs.io includes 1 event-driven AsyncAPI specification.
Defakto Security’s developer surface includes documentation, API reference, getting-started guide, engineering blog, support, signup flow, CLI, and 24 more developer resources.
Kin Score
 Kin Score
How this is scored →
scored 2026-11-06 · rubric v0.27.0
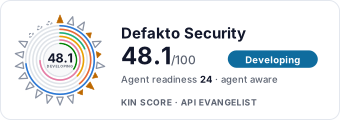 It updates itself when the score changes. Paste this where you link to your API docs:
<a href="https://apis.io/providers/defakto-security/"><img src="https://apis.io/badge/defakto-security/card.svg" alt="Defakto Security on APIs.io — Kin Score by API Evangelist"></a>Other styles, a README pill and a shields.io endpoint are on the badge page.
- MCP Server +12 pts — deployment.mode + probe verdict on the mcp/ manifest, not the pointer; an unprobed slug falls back to authorship
- Agentic Access Contract +10 pts — agentic_access artifact present (x-agentic-access), graded by author
- Idempotency +9 pts — OpenAPI mutating operations declare an idempotency key — a header, a request-body property, or a named de-duplication token whose own description says so (verified); else common[].type matches /idempoten/i (documented)
- A2A Agent Card +8 pts — a2a/
-a2a.yml manifest, graded on conformance.grade against A2A 1.0.0 - Request/Response Examples +7 pts — share of operations carrying request/response examples; else an Examples / Code Samples link
- Registration Without a Human +6 pts — a `registration_endpoint` in the served RFC 8414 / OIDC discovery document
- Contract Quality scores 39.0 — up to +15.3 composite points
- Access Clarity scores 34.2 — up to +13.2 composite points
- Contract Governance scores 18.2 — up to +9.8 composite points
Markets this provider is in provisional
The Kin Score Market layer reads a provider inside its market: its position, and how deep its integrations go. Depth is only comparable within a position. Provisional and unweighted: not part of the Kin Score or agent readiness.
| Market | Position | Depth | Registered MCP server | Declares compatibility |
|---|---|---|---|---|
| PKI and Encryption (certificate authorities, key management) | standard | 26.8 (thin) | - | - |
| OpenID Certified Implementations (OIDC, FAPI, OpenID4VC) | standard | 26.8 (thin) | - | - |
| Buf Schema Registry (public Protocol Buffers modules, gRPC / ConnectRPC schema publishers) | standard | 26.8 (thin) | - | - |
Registered MCP server and declares compatibility are report only — not weighted. Undeclared means we found nothing we can read, so there is no number: we never infer integrations.
Standards implemented 1
Standards this provider implements or carries. De facto ones are profiled and measured by the API Commons; formal ones come from the standards directory and are linked by the provider's own tags. The evidence column says how each claim was established — not that it was made.
APIs 2
Individual APIs this provider publishes, each with its own machine-readable definition.
Defakto Management API
The Defakto control-plane API. A gRPC service surface of sixteen versioned services covering trust domains, clusters, realms, workloads, access policy, service accounts and sess...
SPIRL Management API (legacy)
The pre-rebrand SPIRL control-plane endpoint, still documented and still serving the legacy app.spirl.com console and the spirlctl CLI alongside the current api.defakto.security...
Agent Skills 4
Packaged agent skills for driving this provider's APIs from an AI assistant.
defakto-audit-credential-issuance
AGENT SKILLdefakto-onboard-trust-domain
AGENT SKILLdefakto-rotate-signing-keys
AGENT SKILLdefakto-secretless-cicd
AGENT SKILLDefakto Security API pricing
Pricing Plans 1
Published pricing tiers and plan structures.
Rate Limits 1
Documented rate limits and quota policies.
Defakto Security Rate Limits
RATE LIMITSFinOps 1
Cost, billing, and metering signals for API financial operations.
Defakto Security Finops
FINOPSEvent Specifications 1
AsyncAPI definitions for this provider's event-driven and streaming APIs.
Defakto Security Audit Events
ASYNCAPISecurity Posture 3
Authentication, domain security, vulnerability disclosure, and trust-center signals.
Resources
Get Started 4
Portal, sign-up, and the first successful call
Documentation 2
Reference material describing how the API behaves
Agent Surfaces 2
MCP servers, agent skills, and machine-readable catalogs
Design & Contract 5
Pagination, idempotency, versioning, errors, and events
Build 4
SDKs, sample code, and the tooling you integrate with
Access & Security 4
Authentication, authorization, and security posture
Operate 4
Status, limits, changes, and where to get help
Commercial 3
Pricing, plans, and the legal terms of use
Company 3
The organization behind the API
Source (apis.yml)
Defakto Security API — frequently asked questions
Does Defakto Security have an API?
Yes. APIs.io lists 2 APIs from Defakto Security, including Defakto Management API and SPIRL Management API (legacy).
How do I authenticate with the Defakto Security API?
Defakto Security uses bearer-token authentication (5 schemes). The details are profiled on APIs.io as Defakto Security Authentication.
Is the Defakto Security API ready for AI agents?
Defakto Security has a Kin Score of 48.1 out of 100 (developing) and an Agent Readiness score of 23.9 (agent-aware), scored by API Evangelist on 2026-11-06.
Work with this as data
Every provider here is available over the APIs.io API and to AI agents over MCP.