Adaptive Security is the human security platform for the AI era, defending organizations against AI-powered social engineering — deepfakes, voice cloning, phishing, smishing and vishing — through interactive security awareness training, hyperrealistic multi-channel attack simulations, cloud email security, and AI governance. Founded by Brian Long and Andrew Jones and backed by Andreessen Horowitz (a16z) and the OpenAI Startup Fund, Adaptive protects 1,000+ enterprise customers including PayPal, Figma, Ramp, Plaid and the NHL. The Adaptive API is a read-only REST reporting interface (v2) that gives programmatic access to users, groups, training campaigns, phishing campaigns and simulations, and audit logs for compliance reporting, progress monitoring, and BI/HRIS/SIEM data integration.
Adaptive Security publishes 7 API contracts indexed on the APIs.io network, including Audit Logs API, Groups API, Phishing API, and 4 more. Tagged areas include Company, Security, Cybersecurity, Security Awareness Training, and Phishing Simulation.
The Adaptive Security catalog on APIs.io includes 1 event-driven AsyncAPI specification and 1 Spectral governance ruleset.
Adaptive Security’s developer surface includes changelog, documentation, API reference, getting-started guide, engineering blog, support, pricing, and 33 more developer resources.
47.9/100developing▬ flatAgent37/100agent readyFront door AI6/6
dominant
Heartbeat100/100
alive
saas
Full breakdown ↓
scored 2026-11-13 · rubric v0.28.0 · Show this score on your site →
Regulatory Posture applies to this provider. Its tags matched the
Horizontal (data, software, accessibility, platform) regime, so
Regulatory Posture carries 15 points of the composite.
If this regime is wrong for your business, say so on your
provider repo — the
applicability map is public and we will correct it.
Create-or-Update Ergonomics applies to this provider. This API accepts writes, so it
carries 10 points of the composite. It is scored from the published contracts
themselves: whether a caller can create-or-update in one call, whether the write accepts a key the caller already
holds, and whether the response says which branch ran. Without that, every write needs a search-and-branch in
front of it, and the first time that check is skipped a duplicate record is created.
Scored against the observed mean rather than raw — a provider at the catalog average is unchanged by this facet,
not penalised by it.
The six quality facets above are damped to 75 points between them,
because the conditional facet above carries the other
25. That is why each facet's contribution is shown against a damped
maximum: raising a quality facet moves the composite by 75% of its nominal
weight, not 100%. The full arithmetic is at apis.io/rating/.
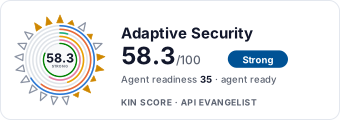
Show this score on your site.
It updates itself when the score changes. Paste this where you link to your API docs:
<a href="https://apis.io/providers/adaptive-security/"><img src="https://apis.io/badge/adaptive-security/card.svg" alt="Adaptive Security on APIs.io — Kin Score by API Evangelist"></a>
Other styles, a README pill and a shields.io endpoint are on the badge page.
Raise your score.
Agent readiness — checks not met, largest first (exact, from this profile):
MCP Server+12 pts — deployment.mode + probe verdict on the mcp/ manifest, not the pointer; an unprobed slug falls back to authorship Ask about this →
Idempotency+9 pts — OpenAPI mutating operations declare an idempotency key — a header, a request-body property, or a named de-duplication token whose own description says so (verified); else common[].type matches /idempoten/i (documented) Ask about this →
Delegated User Identity+6 pts — a served discovery document listing authorization_code in grant_types_supported (served), else an oauth2 authorizationCode flow or openIdConnect declared in an OpenAPI (documented) Ask about this →
Protected Resource Metadata+5 pts — a served /.well-known/oauth-protected-resource carrying `resource` (documented), and naming its authorization_servers (verified) Ask about this →
4 more unmet checks in the Agent Readiness table above.
Kin Score — facets with the most composite points still available (weight × headroom):
Each check links to what satisfies it. Publish the artifact, or tell us where it already lives, and the score moves on the next scoring run.
Not sure how this applies to your stack? Ask about any one item. Kin Lane reads every question, looks at your profile and your situation, and replies with what a fix would take — scoped to that one area, priced up front, yours whether you ship it or not. Ask a question →
The Kin Score Market layer reads a provider inside its market:
its position, and how deep its integrations go. Depth is only comparable within a position. Provisional and unweighted:
not part of the Kin Score or agent readiness.
Registered MCP server and declares compatibility are report only — not weighted.
Undeclared means we found nothing we can read, so there is no number: we never infer integrations.
Standards this provider implements or carries. De facto ones are profiled and measured by the API Commons; formal ones come from the standards directory and are linked by the provider's own tags. The evidence column says how each claim was established — not that it was made.
Adaptive can push events to your systems as they happen — a user fails a phishing simulation, completes a training, falls overdue — so you can drive SIEM detections, SOAR playbo...
Overlays applied on top of this provider's contracts. Each card says who wrote it: a document the provider publishes, or one API Evangelist derived or generated.
aid: adaptive-security
name: Adaptive Security
description: Adaptive Security is the human security platform for the AI era, defending organizations against AI-powered social
  engineering — deepfakes, voice cloning, phishing, smishing and vishing — through interactive security awareness training,
  hyperrealistic multi-channel attack simulations, cloud email security, and AI governance. Founded by Brian Long and Andrew
  Jones and backed by Andreessen Horowitz (a16z) and the OpenAI Startup Fund, Adaptive protects 1,000+ enterprise customers
  including PayPal, Figma, Ramp, Plaid and the NHL. The Adaptive API is a read-only REST reporting interface (v2) that gives
  programmatic access to users, groups, training campaigns, phishing campaigns and simulations, and audit logs for compliance
  reporting, progress monitoring, and BI/HRIS/SIEM data integration.
deliveryModel:
  model: saas
  open_source: false
  commercial: true
  callable_host: true
  label: Hosted service · you call their endpoint
  confidence: high
  source:
  - openapi
  - pricing
  generated: '2026-08-28'
  method: derived
accessModel:
  pricing: enterprise
  onboarding: unknown
  trial: false
  try_now: false
  public: false
  label: Enterprise
  confidence: medium
  source:
  - plans
  - authentication
  - security
  generated: '2026-11-13'
  method: derived
image: https://www.adaptivesecurity.com/og-image.jpg
url: https://raw.githubusercontent.com/api-evangelist/adaptive-security/refs/heads/main/apis.yml
x-type: company
x-source: a16z-portfolio
x-tier: profiled
x-tier-reason: enrichment-pipeline
specificationVersion: '0.23'
created: '2026-07-17'
modified: '2026-07-17'
x-docs-platform: redocly
x-docs-platform-confidence: medium
x-docs-platform-checked: 2026-09-17
tags:
- Company
- Security
- Cybersecurity
- Security Awareness Training
- Phishing Simulation
- Deepfake Defense
- AI Governance
- Social-Engineering
- Reporting
- Compliance
tags_raw:
- Company
- Security
- Cybersecurity
- Security Awareness Training
- Phishing Simulation
- Deepfake Defense
- AI Governance
- Social Engineering
- Reporting
- Compliance
apis:
- aid: adaptive-security:adaptive-security-audit-logs-api
  name: Adaptive Security Audit Logs API
  description: '<span style="background-color: #ff9500; color: white; padding: 2px 6px; border-radius: 3px; font-size: 10px;
    font-weight: bold; text-transform: uppercase; margin-right: 8px;">BETA</span>Admin audit log endpoints'
  humanURL: https://developer.adaptivesecurity.com/
  baseURL: https://api.adaptivesecurity.com
  tags:
  - Audit Logs
  properties:
  - type: OpenAPI
    url: openapi/adaptive-security-audit-logs-api-openapi.yml
  - type: APIReference
    url: https://developer.adaptivesecurity.com/
  - type: Documentation
    url: https://developer.adaptivesecurity.com/
  - type: Authentication
    url: authentication/adaptive-security-authentication.yml
  - type: Conventions
    url: conventions/adaptive-security-conventions.yml
  - type: ErrorCatalog
    url: errors/adaptive-security-problem-types.yml
  - type: Lifecycle
    url: lifecycle/adaptive-security-lifecycle.yml
  - type: Conformance
    url: conformance/adaptive-security-conformance.yml
  - type: DataModel
    url: data-model/adaptive-security-data-model.yml
  - type: LLMsTxt
    url: llms/adaptive-security-llms.txt
- aid: adaptive-security:adaptive-security-groups-api
  name: Adaptive Security Groups API
  description: '<span style="background-color: #ff9500; color: white; padding: 2px 6px; border-radius: 3px; font-size: 10px;
    font-weight: bold; text-transform: uppercase; margin-right: 8px;">BETA</span>User group management endpoints'
  humanURL: https://developer.adaptivesecurity.com/
  baseURL: https://api.adaptivesecurity.com
  tags:
  - Group
  tags_raw:
  - Groups
  properties:
  - type: OpenAPI
    url: openapi/adaptive-security-groups-api-openapi.yml
  - type: APIReference
    url: https://developer.adaptivesecurity.com/
  - type: Documentation
    url: https://developer.adaptivesecurity.com/
  - type: Authentication
    url: authentication/adaptive-security-authentication.yml
  - type: Conventions
    url: conventions/adaptive-security-conventions.yml
  - type: ErrorCatalog
    url: errors/adaptive-security-problem-types.yml
  - type: Lifecycle
    url: lifecycle/adaptive-security-lifecycle.yml
  - type: Conformance
    url: conformance/adaptive-security-conformance.yml
  - type: DataModel
    url: data-model/adaptive-security-data-model.yml
  - type: LLMsTxt
    url: llms/adaptive-security-llms.txt
- aid: adaptive-security:adaptive-security-phishing-api
  name: Adaptive Security Phishing API
  description: '<span style="background-color: #ff9500; color: white; padding: 2px 6px; border-radius: 3px; font-size: 10px;
    font-weight: bold; text-transform: uppercase; margin-right: 8px;">BETA</span>Phishing campaign and simulation management
    endpoints'
  humanURL: https://developer.adaptivesecurity.com/
  baseURL: https://api.adaptivesecurity.com
  tags:
  - Phishing
  properties:
  - type: OpenAPI
    url: openapi/adaptive-security-phishing-api-openapi.yml
  - type: APIReference
    url: https://developer.adaptivesecurity.com/
  - type: Documentation
    url: https://developer.adaptivesecurity.com/
  - type: Authentication
    url: authentication/adaptive-security-authentication.yml
  - type: Conventions
    url: conventions/adaptive-security-conventions.yml
  - type: ErrorCatalog
    url: errors/adaptive-security-problem-types.yml
  - type: Lifecycle
    url: lifecycle/adaptive-security-lifecycle.yml
  - type: Conformance
    url: conformance/adaptive-security-conformance.yml
  - type: DataModel
    url: data-model/adaptive-security-data-model.yml
  - type: LLMsTxt
    url: llms/adaptive-security-llms.txt
- aid: adaptive-security:adaptive-security-training-api
  name: Adaptive Security Training API
  description: '<span style="background-color: #ff9500; color: white; padding: 2px 6px; border-radius: 3px; font-size: 10px;
    font-weight: bold; text-transform: uppercase; margin-right: 8px;">BETA</span>Training campaign and activity endpoints'
  humanURL: https://developer.adaptivesecurity.com/
  baseURL: https://api.adaptivesecurity.com
  tags:
  - Training
  properties:
  - type: OpenAPI
    url: openapi/adaptive-security-training-api-openapi.yml
  - type: APIReference
    url: https://developer.adaptivesecurity.com/
  - type: Documentation
    url: https://developer.adaptivesecurity.com/
  - type: Authentication
    url: authentication/adaptive-security-authentication.yml
  - type: Conventions
    url: conventions/adaptive-security-conventions.yml
  - type: ErrorCatalog
    url: errors/adaptive-security-problem-types.yml
  - type: Lifecycle
    url: lifecycle/adaptive-security-lifecycle.yml
  - type: Conformance
    url: conformance/adaptive-security-conformance.yml
  - type: DataModel
    url: data-model/adaptive-security-data-model.yml
  - type: LLMsTxt
    url: llms/adaptive-security-llms.txt
- aid: adaptive-security:adaptive-security-users-api
  name: Adaptive Security Users API
  description: '<span style="background-color: #ff9500; color: white; padding: 2px 6px; border-radius: 3px; font-size: 10px;
    font-weight: bold; text-transform: uppercase; margin-right: 8px;">BETA</span>User management endpoints'
  humanURL: https://developer.adaptivesecurity.com/
  baseURL: https://api.adaptivesecurity.com
  tags:
  - User
  tags_raw:
  - Users
  properties:
  - type: OpenAPI
    url: openapi/adaptive-security-users-api-openapi.yml
  - type: APIReference
    url: https://developer.adaptivesecurity.com/
  - type: Documentation
    url: https://developer.adaptivesecurity.com/
  - type: Authentication
    url: authentication/adaptive-security-authentication.yml
  - type: Conventions
    url: conventions/adaptive-security-conventions.yml
  - type: ErrorCatalog
    url: errors/adaptive-security-problem-types.yml
  - type: Lifecycle
    url: lifecycle/adaptive-security-lifecycle.yml
  - type: Conformance
    url: conformance/adaptive-security-conformance.yml
  - type: DataModel
    url: data-model/adaptive-security-data-model.yml
  - type: LLMsTxt
    url: llms/adaptive-security-llms.txt
- aid: adaptive-security:adaptive-security-email-security-api
  name: Adaptive Security Email Security API
  description: Email Security detections and company-configured email security rules
  humanURL: https://developer.adaptivesecurity.com/
  baseURL: https://api.adaptivesecurity.com
  tags:
  - Email Security
  properties:
  - type: OpenAPI
    url: openapi/adaptive-security-email-security-api-openapi.yml
- aid: adaptive-security:adaptive-security-webhooks-api
  name: Adaptive Security Webhooks API
  description: "Adaptive can push events to your systems as they happen — a user fails a phishing simulation, completes a\
    \ training, falls overdue — so you can drive SIEM detections, SOAR playbooks, and downstream workflows without polling.\n\
    \n## Delivery\n\nEndpoints must use HTTPS. Adaptive rejects `http://` URLs when you create or update an endpoint. Webhook\
    \ deliveries are encrypted in transit using TLS.\n\nEvery delivery is a `POST` request to your endpoint over HTTPS with\
    \ `Content-Type: application/json`. The body is a [CloudEvents 1.0](https://cloudevents.io/) envelope; the event-specific\
    \ payload is at `data.payload`, and any custom metadata configured on your subscription is echoed back at `data.customdata`.\n\
    \nDelivery is **at least once**: retries and rare internal races can deliver the same event more than once, so dedupe\
    \ on the envelope `id`. Failed deliveries — timeouts, connection errors, `408`, `429`, and `5xx` responses other than\
    \ `501` — are attempted up to five times. The four retry delays have base values of 1 minute, 15 minutes, 1 hour, and\
    \ 6 hours, each with up to 50% jitter. All other non-`2xx` responses, including `1xx`, `3xx`, other `4xx` responses, and\
    \ `501`, are permanent failures and are not retried.\n\nA `429` response always pauses all deliveries to your endpoint.\
    \ A `503` does the same when it includes a valid `Retry-After` value (either delay seconds or an HTTP date). The cooldown\
    \ is at least one minute and never shorter than either the current retry delay or a valid `Retry-After` value. Respond\
    \ with any `2xx` status within 10 seconds to acknowledge a delivery.\n\nEvents are not guaranteed to arrive in order.\
    \ Use the envelope `time` field (when the event occurred) rather than arrival time when ordering matters.\n\n## Verifying\
    \ signatures\n\nEvery delivery carries an `X-Adaptive-Signature` header so you can verify it originated from Adaptive\
    \ and was not tampered with:\n\n```\nX-Adaptive-Signature: t=1752692712,v1=5f7c9a2b...\n```\n\n`t` is the Unix timestamp\
    \ (seconds) of the delivery attempt and `v1` is a hex-encoded HMAC-SHA256 signature. To verify, recompute the signature\
    \ over the string `{id}.{t}.{body}` — the envelope `id`, the header timestamp, and the exact raw request body, joined\
    \ with periods — using your endpoint's signing secret as the HMAC key (the secret's literal characters, not hex-decoded):\n\
    \n```python\nimport hashlib, hmac, time\n\ndef verify(\n    secret: str,\n    event_id: str,\n    header: str,\n    body:\
    \ bytes,\n    tolerance_seconds: int = 300,\n) -> bool:\n    try:\n        parts = [part.split(\"=\", 1) for part in header.split(\"\
    ,\")]\n        timestamps = [\n            value for key, value in parts if key == \"t\"\n        ]\n        signatures\
    \ = [\n            value for key, value in parts if key == \"v1\"\n        ]\n        if len(timestamps) != 1 or not signatures:\n\
    \            return False\n        timestamp = int(timestamps[0])\n    except (TypeError, ValueError):\n        return\
    \ False\n\n    if abs(int(time.time()) - timestamp) > tolerance_seconds:\n        return False\n\n    signed = f\"{event_id}.{timestamp}.\"\
    .encode() + body\n    expected = hmac.new(secret.encode(), signed, hashlib.sha256).hexdigest()\n    return any(\n    \
    \    hmac.compare_digest(expected, signature)\n        for signature in signatures\n    )\n```\n\nRead `event_id` from\
    \ the parsed body, but verify against the exact raw body bytes. The example rejects timestamps more than five minutes\
    \ in the past or future to guard against replay and clock-skew abuse. During secret rotation a delivery may carry multiple\
    \ `v1` signatures; accept if any matches.\n\n## Subscription filters\n\nSubscriptions can narrow an event type to specific\
    \ resources — for example, only `phishing.simulation.failed` events for one campaign. The filterable fields for each event\
    \ are listed in its description below. Filtering on a recurring phishing campaign matches every simulation run in the\
    \ series."
  humanURL: https://developer.adaptivesecurity.com/
  baseURL: https://api.adaptivesecurity.com
  tags:
  - Webhook
  tags_raw:
  - Webhooks
  properties:
  - type: OpenAPI
    url: openapi/adaptive-security-webhooks-api-openapi.yml
maintainers:
- FN: Kin Lane
  email: kin@apievangelist.com
- FN: APIs.json
  email: info@apis.io
common:
- type: RateLimits
  url: rate-limits/adaptive-security-rate-limits.yml
- type: CapabilityMap
  url: capabilities/adaptive-security-capability-edges.yml
  name: Adaptive Security Business Capability Map
- type: Login
  url: https://admin.adaptivesecurity.com/
- type: ChangeLog
  url: https://www.adaptivesecurity.com/resources/product-updates
- type: Plans
  url: plans/adaptive-security-plans-pricing.yml
- type: Webhooks
  url: asyncapi/adaptive-security-webhooks.yml
- type: UsageTerms
  url: terms/adaptive-security-terms-of-service.yml
- type: DataProcessing
  url: privacy/adaptive-security-privacy-policy.yml
- type: Eligibility
  url: eligibility/adaptive-security-eligibility.yml
- type: AIPreferences
  url: ai-preferences/adaptive-security-ai-preferences.yml
- type: Website
  url: https://www.adaptivesecurity.com/
- type: DeveloperPortal
  url: https://developer.adaptivesecurity.com/
- type: Documentation
  url: https://developer.adaptivesecurity.com/
- type: APIReference
  url: https://developer.adaptivesecurity.com/
- type: GettingStarted
  url: https://developer.adaptivesecurity.com/
- type: Blog
  url: https://www.adaptivesecurity.com/blog
- type: Support
  url: https://www.adaptivesecurity.com/support
- type: HelpCenter
  url: https://help.adaptivesecurity.com/en/
- type: Pricing
  url: https://www.adaptivesecurity.com/pricing
- type: SignUp
  url: https://admin.adaptivesecurity.com/login
- type: TermsOfService
  url: https://www.adaptivesecurity.com/legal/terms-of-service
- type: PrivacyPolicy
  url: https://www.adaptivesecurity.com/legal/privacy-policy
- type: StatusPage
  url: https://status.adaptivesecurity.com/
- type: GitHubOrganization
  url: https://github.com/adaptivesecurity
- type: Integrations
  url: https://www.adaptivesecurity.com/integrations
- type: LinkedIn
  url: https://www.linkedin.com/company/adaptivesecurity
- type: TrustCenter
  url: security/adaptive-security-trust-center.yml
- type: Compliance
  url: security/adaptive-security-trust-center.yml
- type: DomainSecurity
  url: security/adaptive-security-domain-security.yml
- type: Authentication
  url: authentication/adaptive-security-authentication.yml
- type: ErrorCatalog
  url: errors/adaptive-security-problem-types.yml
- type: RateLimits
  url: rate-limits/adaptive-security-rate-limits.yml
- type: X-MCPServerCandidate
  url: mcp/adaptive-security-mcp.yml
  note: 'Renamed from MCPServer 2026-09-03 (roadmap#247): the manifest self-describes as status: candidate — a tool list derived
    from the published API contracts, not an existing server. The scorer already read the manifest and reported mcp_server
    correctly; the MCPServer type was crediting the artifact-type surfaces with a server that does not exist.'
- type: AgentSkill
  url: skills/_index.yml
- type: AgenticAccess
  url: agentic-access/adaptive-security-agentic-access.yml
- type: Conventions
  url: conventions/adaptive-security-conventions.yml
- type: DataModel
  url: data-model/adaptive-security-data-model.yml
- type: Lifecycle
  url: lifecycle/adaptive-security-lifecycle.yml
- type: Conformance
  url: conformance/adaptive-security-conformance.yml
- type: Overlay
  url: overlays/adaptive-security-openapi-overlay.yaml
- type: LLMsTxt
  url: llms/adaptive-security-llms.txt
Adaptive Security API — frequently asked questions
Does Adaptive Security have an API?
Yes. APIs.io lists 7 APIs from Adaptive Security, including Adaptive Security Audit Logs API, Adaptive Security Groups API and Adaptive Security Phishing API, and 4 more.
Is there an OpenAPI specification for the Adaptive Security API?
Yes. APIs.io indexes 7 OpenAPI specifications for Adaptive Security, each linked for download from this page.
How do I authenticate with the Adaptive Security API?
Adaptive Security uses bearer-token authentication (http · 1 scheme). The details are profiled on APIs.io as Adaptive Security Authentication.
How much does the Adaptive Security API cost?
Adaptive Security publishes its prices; its SMBs plan is Get pricing per seat as of 2026-10-28. APIs.io lists 2 pricing plans for Adaptive Security, with each plan's price, limits and inclusions under Pricing on this page.
Is the Adaptive Security API ready for AI agents?
Adaptive Security has a Kin Score of 47.9 out of 100 (developing) and an Agent Readiness score of 37.0 (agent-ready), scored by API Evangelist on 2026-11-13.
Calls without X-API-Key need no key. Calls with it need a paid plan — get a key.
Get an API key
Free tier, no form to fill in. Signing in shares your email address with us — we
store it to create your key and to recognise you if you sign in with another
provider. See our Privacy Policy and
Terms.
 Kin Score
How this is scored →
 It updates itself when the score changes. Paste this where you link to your API docs: