P0 Security website screenshot

P0 Security

P0 Security is a cloud-native Privileged Access Management (PAM) platform that governs runtime authorization for human users, machine/service accounts, and AI agents across hybrid and multi-cloud environments. Its AuthZ Control Plane enforces just-in-time (JIT), least-privilege access to AWS, Google Cloud, Azure, Oracle Cloud, Kubernetes, databases, SSH hosts, Okta, and Google Workspace — provisioning short-lived credentials on request, routing approvals through Slack, Microsoft Teams, the web app, or the CLI, and automatically revoking access when it expires. P0 also provides an access inventory and identity graph, posture scanning for over-privileged and stale access, service-account key rotation, and an agentic authorization control plane with a self-hosted MCP Gateway that enforces least-privilege policy on every MCP tool call. Developers integrate P0 through the official p0 CLI, a Terraform provider, and a bearer-authenticated Just-in-Time Access API (Command, Permission Request, and Access Policies).

P0 Security publishes 2 API contracts indexed on the APIs.io network: Command API and Permission Requests API. Tagged areas include Company, Security, Privileged Access Management, Identity and Access Management, and Just-In-Time Access.

The P0 Security catalog on APIs.io includes 1 Spectral governance ruleset.

P0 Security’s developer surface includes documentation, API reference, getting-started guide, support, engineering blog, signup flow, CLI, and 23 more developer resources.

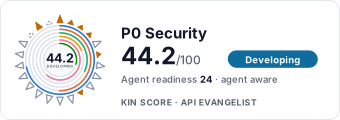
44.2/100 developing ▬ flat Agent 24/100 agent aware Front door AI 6/6 dominant Heartbeat 98/100 alive saas Full breakdown ↓
scored 2026-11-06 · rubric v0.27.0 · Show this score on your site →
1 published contract 1 MCP Servers 1 Agent Skills
CompanySecurityPrivileged Access ManagementIdentity and Access ManagementJust-In-Time AccessCloud SecurityAuthorizationZero TrustAgentic AccessMCP

What this lets a business do 1

Business capabilities this provider's published APIs can perform, derived from its own contracts. Browse all capabilities →

Cybersecurity Management
BC-620
CommandPermission Requests
POST /o/{orgId}/permission-requests/{requestId}/approve

Kin Score

Kin Score Kin Score How this is scored →
scored 2026-11-06 · rubric v0.27.0
Regulatory Posture applies to this provider. Its tags matched the Horizontal (data, software, accessibility, platform) regime, so Regulatory Posture carries 15 points of the composite. If this regime is wrong for your business, say so on your provider repo — the applicability map is public and we will correct it.
Create-or-Update Ergonomics applies to this provider. This API accepts writes, so it carries 10 points of the composite. It is scored from the published contracts themselves: whether a caller can create-or-update in one call, whether the write accepts a key the caller already holds, and whether the response says which branch ran. Without that, every write needs a search-and-branch in front of it, and the first time that check is skipped a duplicate record is created. Scored against the observed mean rather than raw — a provider at the catalog average is unchanged by this facet, not penalised by it.
The six quality facets above are damped to 75 points between them, because the conditional facet above carries the other 25. That is why each facet's contribution is shown against a damped maximum: raising a quality facet moves the composite by 75% of its nominal weight, not 100%. The full arithmetic is at apis.io/rating/.
Show this score on your site. Kin Score badge preview for P0 Security It updates itself when the score changes. Paste this where you link to your API docs:
<a href="https://apis.io/providers/p0-security/"><img src="https://apis.io/badge/p0-security/card.svg" alt="P0 Security on APIs.io — Kin Score by API Evangelist"></a>
Other styles, a README pill and a shields.io endpoint are on the badge page.
Raise your score.
Agent readiness — checks not met, largest first (exact, from this profile):
  • Idempotency +9 pts — OpenAPI mutating operations declare an idempotency key — a header, a request-body property, or a named de-duplication token whose own description says so (verified); else common[].type matches /idempoten/i (documented)
  • A2A Agent Card +8 pts — a2a/-a2a.yml manifest, graded on conformance.grade against A2A 1.0.0
  • Rate-Limit Signaling +7 pts — OpenAPI responses document X-RateLimit-* / RateLimit headers (verified), else a rate_limits artifact or RateLimits link (documented)
  • Request/Response Examples +7 pts — share of operations carrying request/response examples; else an Examples / Code Samples link
  • Registration Without a Human +6 pts — a `registration_endpoint` in the served RFC 8414 / OIDC discovery document
  • Delegated User Identity +6 pts — a served discovery document listing authorization_code in grant_types_supported (served), else an oauth2 authorizationCode flow or openIdConnect declared in an OpenAPI (documented)
7 more unmet checks in the Agent Readiness table above.
Kin Score — facets with the most composite points still available (weight × headroom):
Each check links to what satisfies it. Publish the artifact, or tell us where it already lives, and the score moves on the next scoring run.
Improve this rating by publishing the missing artifacts — every area above can be raised, and the full rubric is at apis.io/rating/. Every facet and dimension name above is a link: it opens that measurement's own page — what it means, the exact checks that feed it, how the whole catalog distributes on it, and the providers at the top of it. This rating is computed from the provider profile at artifacts.apis.io/p0-security/apis.yml: open an issue on github.com/api-evangelist/p0-security to ask a question or point us at an artifact you publish. Submit an artifact on GitHub — free → Manage your own listing — the Influence plan, $499/mo →

Standards implemented 3

Standards this provider implements or carries. De facto ones are profiled and measured by the API Commons; formal ones come from the standards directory and are linked by the provider's own tags. The evidence column says how each claim was established — not that it was made.

IAM
tagged — the provider's own APIs.json carries the standard as a tag; implementation not verified
measured — observed by APIs.io (documented)
measured — observed by APIs.io (published)

APIs 2

Individual APIs this provider publishes, each with its own machine-readable definition.

P0 Security Command API

Submit commands that trigger access workflows.

P0 Security Permission Requests API

Approve, deny, or revoke just-in-time access requests.

Open Collections 2

Open, tool-agnostic API collections (OpenAPI-derived and Bruno).

MCP Servers 1

Model Context Protocol servers that expose these APIs to AI agents.

P0 MCP Gateway

The P0 MCP Gateway is a self-hosted runtime enforcement layer for agentic authorization. It sits in the data path between AI agents (MCP clients) and upstream MCP servers: it pr...

MCP SERVER

Agent Skills 1

Packaged agent skills for driving this provider's APIs from an AI assistant.

Spectral Rules 1

Spectral governance rulesets for linting and validating these APIs.

P0 Security API Rules

56 rules · 54 errors 1 warnings 1 info

SPECTRAL

OpenAPI Overlays 1

Overlays applied on top of this provider's contracts. Each card says who wrote it: a document the provider publishes, or one API Evangelist derived or generated.

P0 Security Jit Overlay

4 actions · update · p0-security-jit-openapi.yml

DERIVED

Security Posture 3

Authentication, domain security, vulnerability disclosure, and trust-center signals.

P0 Security Authentication

http · 1 scheme

SECURITY

P0 Security Domain Security

TLSv1.3 · HSTS · DNSSEC · DMARC

SECURITY

P0 Security Trust Center

SOC 2 Type II

SECURITY

Agentic Access 1

Recommended x-agentic-access execution contracts for AI agents.

P0 Security Agentic Access

4 operations · 4 acting · 1 human-in-the-loop

4 operations · 4 acting

AGENTIC

Resources

Get Started 4

Portal, sign-up, and the first successful call

Documentation 2

Reference material describing how the API behaves

Agent Surfaces 4

MCP servers, agent skills, and machine-readable catalogs

Design & Contract 5

Pagination, idempotency, versioning, errors, and events

Build 3

SDKs, sample code, and the tooling you integrate with

Access & Security 3

Authentication, authorization, and security posture

Operate 2

Status, limits, changes, and where to get help

Commercial 2

Pricing, plans, and the legal terms of use

Company 3

The organization behind the API

Other 2

Properties that don't map to a standard resource type

Source (apis.yml)

apis.yml Raw ↑
aid: p0-security
name: P0 Security
description: P0 Security is a cloud-native Privileged Access Management (PAM) platform that governs runtime authorization
  for human users, machine/service accounts, and AI agents across hybrid and multi-cloud environments. Its AuthZ Control Plane
  enforces just-in-time (JIT), least-privilege access to AWS, Google Cloud, Azure, Oracle Cloud, Kubernetes, databases, SSH
  hosts, Okta, and Google Workspace — provisioning short-lived credentials on request, routing approvals through Slack, Microsoft
  Teams, the web app, or the CLI, and automatically revoking access when it expires. P0 also provides an access inventory
  and identity graph, posture scanning for over-privileged and stale access, service-account key rotation, and an agentic
  authorization control plane with a self-hosted MCP Gateway that enforces least-privilege policy on every MCP tool call.
  Developers integrate P0 through the official p0 CLI, a Terraform provider, and a bearer-authenticated Just-in-Time Access
  API (Command, Permission Request, and Access Policies).
url: https://raw.githubusercontent.com/api-evangelist/p0-security/refs/heads/main/apis.yml
x-type: company
x-source: vc-portfolio
x-backed-by:
- lightspeed-venture-partners
x-tier: stub
x-tier-reason: portfolio-lead
deliveryModel:
  model: saas
  open_source: false
  commercial: true
  callable_host: true
  label: Hosted service · you call their endpoint
  confidence: high
  source:
  - openapi
  - pricing
  generated: '2026-08-28'
  method: derived
accessModel:
  pricing: unknown
  onboarding: unknown
  trial: false
  try_now: false
  public: false
  label: Unknown
  confidence: low
  source:
  - authentication
  - security
  generated: '2026-11-06'
  method: derived
specificationVersion: '0.23'
created: '2026-07-17'
modified: '2026-10-06'
image: https://p0.dev/p0.jpg
x-docs-platform: gitbook
x-docs-platform-confidence: high
x-docs-platform-checked: 2026-10-04
tags:
- Company
- Security
- Privileged Access Management
- Identity and Access Management
- Just-In-Time Access
- Cloud Security
- Authorization
- Zero Trust
- Agentic Access
- MCP
tags_raw:
- Company
- Security
- Privileged Access Management
- Identity and Access Management
- Just-in-Time Access
- Cloud Security
- Authorization
- Zero Trust
- Agentic Access
- MCP
apis:
- aid: p0-security:p0-security-command-api
  name: P0 Security Command API
  description: Submit commands that trigger access workflows.
  humanURL: https://docs.p0.dev/access-management/just-in-time-access/just-in-time-api
  baseURL: https://api.p0.app
  tags:
  - Command
  properties:
  - type: OpenAPI
    url: openapi/p0-security-command-api-openapi.yml
  - type: Documentation
    url: https://docs.p0.dev/access-management/just-in-time-access/just-in-time-api
  - type: Authentication
    url: authentication/p0-security-authentication.yml
- aid: p0-security:p0-security-permission-requests-api
  name: P0 Security Permission Requests API
  description: Approve, deny, or revoke just-in-time access requests.
  humanURL: https://docs.p0.dev/access-management/just-in-time-access/just-in-time-api
  baseURL: https://api.p0.app
  tags:
  - Permission Requests
  properties:
  - type: OpenAPI
    url: openapi/p0-security-permission-requests-api-openapi.yml
  - type: Documentation
    url: https://docs.p0.dev/access-management/just-in-time-access/just-in-time-api
  - type: Authentication
    url: authentication/p0-security-authentication.yml
maintainers:
- FN: Kin Lane
  email: kin@apievangelist.com
- FN: APIs.json
  email: info@apis.io
common:
- url: https://p0.dev/feed/
  type: BlogRSS
- type: CapabilityMap
  url: capabilities/p0-security-capability-edges.yml
  name: P0 Security Business Capability Map
- type: Website
  url: https://p0.dev
- type: DomainSecurity
  url: security/p0-security-domain-security.yml
- type: AgenticAccess
  url: agentic-access/p0-security-agentic-access.yml
- type: DeveloperPortal
  url: https://docs.p0.dev/
- type: Documentation
  url: https://docs.p0.dev/
- type: APIReference
  url: https://docs.p0.dev/access-management/just-in-time-access/just-in-time-api
- type: GettingStarted
  url: https://docs.p0.dev/getting-started/p0-security-onboarding
- type: Support
  url: https://support.p0.dev/
- type: Blog
  url: https://p0.dev/blog/
- type: GitHubOrganization
  url: https://github.com/p0-security
- type: SignUp
  url: https://p0.app/
- type: Login
  url: https://p0.app/
- type: TermsOfService
  url: https://p0.app/tos
- type: PrivacyPolicy
  url: https://p0.app/privacy
- type: TrustCenter
  url: https://p0.dev/trust-center/
- type: Compliance
  url: security/p0-security-trust-center.yml
- type: Conformance
  url: conformance/p0-security-conformance.yml
- type: Packages
  url: packages/p0-security-packages.yml
- type: CLI
  url: cli/p0-security-cli.yml
- type: MCPServer
  url: mcp/p0-security-mcp.yml
- type: LLMsTxt
  url: llms/p0-security-llms.txt
- type: ChangeLog
  url: changelog/p0-security-changelog.yml
- type: Lifecycle
  url: lifecycle/p0-security-lifecycle.yml
- type: Conventions
  url: conventions/p0-security-conventions.yml
- type: ErrorCatalog
  url: errors/p0-security-problem-types.yml
- type: DataModel
  url: data-model/p0-security-data-model.yml
- type: Overlay
  url: overlays/p0-security-jit-overlay.yaml
- type: AgentSkill
  url: skills/_index.yml
x-enrichment:
  date: '2026-07-20'
  status: enriched
  artifacts_added: 18
  pass: local-v1

P0 Security API — frequently asked questions

Does P0 Security have an API?

Yes. APIs.io lists 2 APIs from P0 Security, including P0 Security Command API and P0 Security Permission Requests API.

Is there an OpenAPI specification for the P0 Security API?

Yes. APIs.io indexes 2 OpenAPI specifications for P0 Security, each linked for download from this page.

How do I authenticate with the P0 Security API?

P0 Security uses bearer-token authentication (http · 1 scheme). The details are profiled on APIs.io as P0 Security Authentication.

Does P0 Security have an MCP server?

Yes. APIs.io lists 1 MCP server for P0 Security: The P0 MCP Gateway is a self-hosted runtime enforcement layer for agentic authorization. It sits in the data path between AI agents (MCP clients) and upstream MCP servers: it proxies MCP tool calls, v

Is the P0 Security API ready for AI agents?

P0 Security has a Kin Score of 44.2 out of 100 (developing) and an Agent Readiness score of 24.0 (agent-aware), scored by API Evangelist on 2026-11-06.

Work with this as data

Every provider here is available over the APIs.io API and to AI agents over MCP.

MCP server

One button, every client — Claude, Cursor, VS Code and the rest.

https://apis.io/mcp

Tools for providers

9 MCP tools reach this
  • find_providersBrowse and filter every provider in the catalog.
  • get_provider_artifactsEvery artifact this provider publishes, grouped by type.
  • get_provider_operationsEvery operation across all of their OpenAPIs — one call instead of parsing every spec.
  • get_provider_toolsEvery MCP tool they ship, with the operation each wraps.
  • get_provider_evidenceHow each part of their score was established. Free — the basis for a claim should not sit behind it.
  • get_provider_ratingPRO — composite, band, trend and facet scores.
  • apis_io_searchSTART HERE — APIs, providers and tags for one query, each with its total.
  • resolveTurn a domain, URL or GitHub org into the provider it belongs to.
  • find_cohortsEvery scored population of providers in the catalog.
All 92 tools →

Call it yourself

curl for this page
This provider
curl "https://apis.io/api/v1/providers/p0-security"
All providers
curl "https://apis.io/api/v1/providers?limit=25"
Every operation they expose
curl "https://apis.io/api/v1/providers/p0-security/operations?limit=25"
How their score was established
curl "https://apis.io/api/v1/providers/p0-security/evidence"

Calls without X-API-Key need no key. Calls with it need a paid plan — get a key.

Get an API key

Free tier, no form to fill in. Signing in shares your email address with us — we store it to create your key and to recognise you if you sign in with another provider. See our Privacy Policy and Terms.

A second provider on the same verified email joins the account you already have.
