Malwarebytes is an American anti-malware and endpoint security company founded in 2008 and headquartered in Santa Clara, California. It sells consumer protection under the Malwarebytes brand (Premium Security, Mobile Security, Browser Guard, Privacy VPN, Identity Theft Protection, Personal Data Remover, AdwCleaner) and business endpoint security under the ThreatDown brand, powered by Malwarebytes. The programmable surface is ThreatDown: two large OAuth2-protected REST APIs — the Nebula API for direct-tenant endpoint security management and the OneView API for multi-tenant MSP management of sites and subscriptions — both served from api.threatdown.com and documented with public OpenAPI 3.0 definitions covering endpoints, detections, jobs, policies, quarantine, vulnerability and patch management, EDR/XDR, DNS filtering, device control, email protection and webhooks.
Malwarebytes publishes 52 API contracts indexed on the APIs.io network, including Account API, AI Detection & Response API, App Block API, and 49 more. Tagged areas include Company, Security, Cybersecurity, Endpoint Security, and Anti Malware.
The Malwarebytes catalog on APIs.io includes 1 event-driven AsyncAPI specification and 1 Spectral governance ruleset.
Malwarebytes’ developer surface includes documentation, API reference, getting-started guide, support, engineering blog, pricing, signup flow, and 40 more developer resources.
Regulatory Posture applies to this provider. Its tags matched the
Horizontal (data, software, accessibility, platform) regime, so
Regulatory Posture carries 15 points of the composite.
If this regime is wrong for your business, say so on your
provider repo — the
applicability map is public and we will correct it.
Create-or-Update Ergonomics applies to this provider. This API accepts writes, so it
carries 10 points of the composite. It is scored from the published contracts
themselves: whether a caller can create-or-update in one call, whether the write accepts a key the caller already
holds, and whether the response says which branch ran. Without that, every write needs a search-and-branch in
front of it, and the first time that check is skipped a duplicate record is created.
Scored against the observed mean rather than raw — a provider at the catalog average is unchanged by this facet,
not penalised by it.
The six quality facets above are damped to 75 points between them,
because the conditional facet above carries the other
25. That is why each facet's contribution is shown against a damped
maximum: raising a quality facet moves the composite by 75% of its nominal
weight, not 100%. The full arithmetic is at apis.io/rating/.
Show this score on your site.
It updates itself when the score changes. Paste this where you link to your API docs:
<a href="https://apis.io/providers/malwarebytes/"><img src="https://apis.io/badge/malwarebytes/card.svg" alt="Malwarebytes on APIs.io — Kin Score by API Evangelist"></a>
Other styles, a README pill and a shields.io endpoint are on the badge page.
Raise your score.
Agent readiness — checks not met, largest first (exact, from this profile):
MCP Server+12 pts — deployment.mode + probe verdict on the mcp/ manifest, not the pointer; an unprobed slug falls back to authorship
Idempotency+9 pts — OpenAPI mutating operations declare an idempotency key — a header, a request-body property, or a named de-duplication token whose own description says so (verified); else common[].type matches /idempoten/i (documented)
Stable Error Semantics+8 pts — OpenAPI $refs a shared error schema across 4xx/5xx responses (verified), else common[].type includes ErrorCatalog / ErrorCodes / DeclineCodes
A2A Agent Card+8 pts — a2a/-a2a.yml manifest, graded on conformance.grade against A2A 1.0.0
Delegated User Identity+6 pts — a served discovery document listing authorization_code in grant_types_supported (served), else an oauth2 authorizationCode flow or openIdConnect declared in an OpenAPI (documented)
7 more unmet checks in the Agent Readiness table above.
Kin Score — facets with the most composite points still available (weight × headroom):
The Kin Score Market layer reads a provider inside its market:
its position, and how deep its integrations go. Depth is only comparable within a position. Provisional and unweighted:
not part of the Kin Score or agent readiness.
Registered MCP server and declares compatibility are report only — not weighted.
Undeclared means we found nothing we can read, so there is no number: we never infer integrations.
Standards this provider implements or carries. De facto ones are profiled and measured by the API Commons; formal ones come from the standards directory and are linked by the provider's own tags. The evidence column says how each claim was established — not that it was made.
Manage governance rules and settings for AI Detection & Response (AIDR). Use these APIs to create per-tool authorization rules that determine whether specific AI tools are autho...
The Content Filtering APIs are for managing content filtering rules used by the DNS module. These rules control what domains or categories of domains your endpoints have access to.
Detections contain information on threats such as malware, ransomware, and malicious URLs found across your account. Use the detection APIs to export detection data and retrieve...
The Device Control feature manages access to USB storage drives. Activity is logged every time a USB device is blocked or restricted to read-only. Use the Device Control APIs to...
The DNS Filtering module limits the number of domain-based threats in your environment by allowing and blocking access across the network. Each time this occurs, a record is gen...
## Endpoints Introduction An Endpoint is a device which has the ThreatDown Endpoint Agent installed. Currently, there are available Endpoint Agents for Windows, macOS, and Linux...
Exclusions allow you to prevent trusted applications, websites, and services from being detected by our security engine. This means they won't be scanned or blocked. Use these A...
EDR customers can use Flight Recorder to search event data captured on endpoints that have suspicious activity monitoring enabled. Use these APIs to search through files, regist...
# Grid Introduction Using the following API, you can search endpoints, detections, software inventory, vulnerabilities, rid rules, os-patches, device control events and dns logs...
Groups are used to contain and organize endpoints. Policies, which determine the software settings, and endpoints, are assigned to groups. Endpoints use the policies in the grou...
This API offers a powerful tool to create notification subscriptions. There are different categories of notifications, for each category different constraints and output fields ...
A policy is a set of configurations that determine how the endpoint agent monitors your endpoints, such as protection and scan settings. Once a policy has been created, it needs...
The Preferences APIs allow you to enable or disable all notifications of a specific type (email, webhook, slack, teams, admin app), without needing to modify or delete multiple ...
When a harmful file is found on a device, it can be neutralized and placed in quarantine, preventing it from posing a threat. You can utilize the Quarantine APIs to export or ch...
A remote intrusion detection (RID) occurs when a brute force protection rule is triggered according to policy settings. Use these APIs to export and search for RID rules by spec...
Scheduled scans allow you to automate scans to run based on a certain schedule, rather than manually triggering a scan. Use these APIs to create and manage your scan schedules.
Create and manage sites through APIs. Using sites APIs you can easily segment the usage and the subscriptions for your customers. In order to obtain an `account_id` for one of y...
Suspicious Activities are found using Endpoint Detection and Response (EDR). When Suspicious Activity Monitoring is enabled via the policy, EDR watches for potentially malicious...
## Using Webhooks ThreatDown can send webhook events that notify your application any time an event happens on your account. This is useful for transactions which are not report...
Overlays applied on top of this provider's contracts. Each card says who wrote it: a document the provider publishes, or one API Evangelist derived or generated.
aid: malwarebytes
name: Malwarebytes
description: 'Malwarebytes is an American anti-malware and endpoint security company founded in 2008 and headquartered in
  Santa Clara, California. It sells consumer protection under the Malwarebytes brand (Premium Security, Mobile Security, Browser
  Guard, Privacy VPN, Identity Theft Protection, Personal Data Remover, AdwCleaner) and business endpoint security under the
  ThreatDown brand, powered by Malwarebytes. The programmable surface is ThreatDown: two large OAuth2-protected REST APIs
  — the Nebula API for direct-tenant endpoint security management and the OneView API for multi-tenant MSP management of sites
  and subscriptions — both served from api.threatdown.com and documented with public OpenAPI 3.0 definitions covering endpoints,
  detections, jobs, policies, quarantine, vulnerability and patch management, EDR/XDR, DNS filtering, device control, email
  protection and webhooks.'
url: https://raw.githubusercontent.com/api-evangelist/malwarebytes/refs/heads/main/apis.yml
deliveryModel:
  model: saas
  open_source: false
  commercial: true
  callable_host: true
  label: Hosted service · you call their endpoint
  confidence: high
  source:
  - openapi
  - pricing
  generated: '2026-08-28'
  method: derived
accessModel:
  pricing: paid
  onboarding: unknown
  trial: false
  try_now: false
  public: false
  label: Paid
  confidence: high
  source:
  - plans
  - authentication
  - scopes
  - rate-limits
  - security
  generated: '2026-11-06'
  method: derived
image: https://www.malwarebytes.com/wp-content/uploads/sites/2/2026/01/Malwarebytes-wordmark-horiz-Brand-Blue.png?w=810
x-type: company
x-source: harvest:secondary-market
specificationVersion: '0.23'
created: '2026-08-04'
modified: '2026-10-06'
tags:
- Company
- Security
- Cybersecurity
- Endpoint Security
- Anti Malware
- Endpoint Detection and Response
- Threat Detection
- Vulnerability Management
- Patch Management
- Managed Service Providers
- DNS Filtering
- Webhook
tags_raw:
- Company
- Security
- Cybersecurity
- Endpoint Security
- Anti-Malware
- Endpoint Detection and Response
- Threat Detection
- Vulnerability Management
- Patch Management
- Managed Service Providers
- DNS Filtering
- Webhooks
maintainers:
- FN: Kin Lane
  email: kin@apievangelist.com
- FN: APIs.json
  email: info@apis.io
common:
- type: Plans
  url: plans/malwarebytes-plans-pricing.yml
- type: AgenticAccess
  url: agentic-access/malwarebytes-agentic-access.yml
- type: Spectral
  url: rules/malwarebytes-rules.yml
- type: Vocabulary
  url: vocabulary/malwarebytes-vocabulary.yml
- type: Hosts
  url: hosts/malwarebytes-hosts.yml
- type: Vendors
  url: vendors/malwarebytes-vendors.yml
- type: SDKs
  url: packages/malwarebytes-packages.yml
- type: Newsroom
  url: https://www.malwarebytes.com/press/
- url: https://www.malwarebytes.com/blog/feed/index.xml
  type: BlogRSS
- type: CapabilityMap
  url: capabilities/malwarebytes-capability-edges.yml
  name: Malwarebytes Business Capability Map
- type: X-MCPServerCandidate
  url: mcp/malwarebytes-mcp.yml
  note: 'Renamed from MCPServer 2026-09-03 (roadmap#247): the manifest self-describes as status: candidate — a tool list derived
    from the published API contracts, not an existing server. The scorer already read the manifest and reported mcp_server
    correctly; the MCPServer type was crediting the artifact-type surfaces with a server that does not exist.'
- type: Overlay
  url: overlays/malwarebytes-threatdown-nebula-overlay.yaml
- type: Website
  url: https://www.malwarebytes.com/
- type: DeveloperPortal
  url: https://api.threatdown.com/nebula/v1/docs
- type: Documentation
  url: https://api.threatdown.com/nebula/v1/docs
- type: APIReference
  url: https://api.threatdown.com/nebula/v1/docs
- type: GettingStarted
  url: https://support.threatdown.com/hc/en-us/articles/5808694795539-Nebula-API-example-using-Ruby
- type: Support
  url: https://support.threatdown.com/hc/en-us/
- type: HelpCenter
  url: https://help.malwarebytes.com/hc/en-us
- type: Community
  url: https://forums.malwarebytes.com/
- type: Blog
  url: https://www.malwarebytes.com/blog
- type: GitHubOrganization
  url: https://github.com/malwarebytes
- type: Pricing
  url: https://www.threatdown.com/pricing/
- type: SignUp
  url: https://cloud.threatdown.com/auth/login
- type: TermsOfService
  url: https://www.threatdown.com/legal/terms-of-service/
- type: PrivacyPolicy
  url: https://www.threatdown.com/legal/privacy-policy/
- type: StatusPage
  url: https://status.threatdown.com/
- type: Lifecycle
  url: lifecycle/malwarebytes-lifecycle.yml
- type: Deprecation
  url: lifecycle/malwarebytes-lifecycle.yml
- type: ChangeLog
  url: changelog/malwarebytes-changelog.yml
- type: Security
  url: security/malwarebytes-vulnerability-disclosure.yml
- type: VulnerabilityDisclosure
  url: security/malwarebytes-vulnerability-disclosure.yml
- type: TrustCenter
  url: security/malwarebytes-trust-center.yml
- type: Compliance
  url: https://www.threatdown.com/legal/trust-and-compliance/
- type: DomainSecurity
  url: security/malwarebytes-domain-security.yml
- type: Conformance
  url: conformance/malwarebytes-conformance.yml
- type: Authentication
  url: authentication/malwarebytes-authentication.yml
- type: OAuthScopes
  url: scopes/malwarebytes-scopes.yml
- type: Conventions
  url: conventions/malwarebytes-conventions.yml
- type: RateLimits
  url: rate-limits/malwarebytes-rate-limits.yml
- type: DataModel
  url: data-model/malwarebytes-data-model.yml
- type: Webhooks
  url: asyncapi/malwarebytes-threatdown-webhooks.yml
- type: Packages
  url: packages/malwarebytes-packages.yml
- type: WellKnown
  url: well-known/malwarebytes-well-known.yml
- type: SecurityTxt
  url: well-known/malwarebytes-security.txt
- type: LLMsTxt
  url: llms/malwarebytes-llms.txt
- type: AgentSkill
  url: skills/_index.yml
apis:
- aid: malwarebytes:malwarebytes-account-api
  name: Malwarebytes Account API
  description: The Account API from Malwarebytes — 2 operation(s) for account.
  humanURL: https://api.threatdown.com/nebula/v1/docs
  baseURL: https://api.threatdown.com
  tags:
  - Account
  properties:
  - type: OpenAPI
    url: openapi/malwarebytes-account-api-openapi.yml
  - type: Documentation
    url: https://api.threatdown.com/nebula/v1/docs
  - type: APIReference
    url: https://api.threatdown.com/nebula/v1/docs
  - type: Documentation
    url: https://cloud.malwarebytes.com/api/v2/oneview/docs
- aid: malwarebytes:malwarebytes-ai-detection-response-api
  name: Malwarebytes AI Detection & Response API
  description: 'Manage governance rules and settings for AI Detection & Response (AIDR).


    Use these APIs to create per-tool authorization rules that determine whether specific AI tools are authorized, unauthorized,
    or pending review. Configure account-level defaults as a fallback when no matching rule exists.'
  humanURL: https://api.threatdown.com/nebula/v1/docs
  baseURL: https://api.threatdown.com
  tags:
  - AI Detection & Response
  properties:
  - type: OpenAPI
    url: openapi/malwarebytes-ai-detection-response-api-openapi.yml
  - type: Documentation
    url: https://api.threatdown.com/nebula/v1/docs
  - type: APIReference
    url: https://api.threatdown.com/nebula/v1/docs
  - type: Documentation
    url: https://cloud.malwarebytes.com/api/v2/oneview/docs
- aid: malwarebytes:malwarebytes-app-block-api
  name: Malwarebytes App Block API
  description: The App Block API from Malwarebytes — 20 operation(s) for app block.
  humanURL: https://api.threatdown.com/nebula/v1/docs
  baseURL: https://api.threatdown.com
  tags:
  - App Block
  properties:
  - type: OpenAPI
    url: openapi/malwarebytes-app-block-api-openapi.yml
  - type: Documentation
    url: https://api.threatdown.com/nebula/v1/docs
  - type: APIReference
    url: https://api.threatdown.com/nebula/v1/docs
  - type: Documentation
    url: https://cloud.malwarebytes.com/api/v2/oneview/docs
- aid: malwarebytes:malwarebytes-assets-api
  name: Malwarebytes Assets API
  description: The Assets API from Malwarebytes — 8 operation(s) for assets.
  humanURL: https://api.threatdown.com/nebula/v1/docs
  baseURL: https://api.threatdown.com
  tags:
  - Assets
  properties:
  - type: OpenAPI
    url: openapi/malwarebytes-assets-api-openapi.yml
  - type: Documentation
    url: https://api.threatdown.com/nebula/v1/docs
  - type: APIReference
    url: https://api.threatdown.com/nebula/v1/docs
  - type: Documentation
    url: https://cloud.malwarebytes.com/api/v2/oneview/docs
- aid: malwarebytes:malwarebytes-authentication-api
  name: Malwarebytes Authentication API
  description: The Authentication API from Malwarebytes — 2 operation(s) for authentication.
  humanURL: https://api.threatdown.com/nebula/v1/docs
  baseURL: https://api.threatdown.com
  tags:
  - Authentication
  properties:
  - type: OpenAPI
    url: openapi/malwarebytes-authentication-api-openapi.yml
  - type: Documentation
    url: https://api.threatdown.com/nebula/v1/docs
  - type: APIReference
    url: https://api.threatdown.com/nebula/v1/docs
  - type: Documentation
    url: https://cloud.malwarebytes.com/api/v2/oneview/docs
- aid: malwarebytes:malwarebytes-case-management-api
  name: Malwarebytes Case Management API
  description: The Case Management APIs are for managing Managed Detection and Response (MDR) and Managed Threat Hunting (MTH)
    cases.
  humanURL: https://api.threatdown.com/nebula/v1/docs
  baseURL: https://api.threatdown.com
  tags:
  - Case Management
  properties:
  - type: OpenAPI
    url: openapi/malwarebytes-case-management-api-openapi.yml
  - type: Documentation
    url: https://api.threatdown.com/nebula/v1/docs
  - type: APIReference
    url: https://api.threatdown.com/nebula/v1/docs
  - type: Documentation
    url: https://cloud.malwarebytes.com/api/v2/oneview/docs
- aid: malwarebytes:malwarebytes-content-filtering-api
  name: Malwarebytes Content Filtering API
  description: The Content Filtering APIs are for managing content filtering rules used by the DNS module. These rules control
    what domains or categories of domains your endpoints have access to.
  humanURL: https://api.threatdown.com/nebula/v1/docs
  baseURL: https://api.threatdown.com
  tags:
  - Content Filtering
  properties:
  - type: OpenAPI
    url: openapi/malwarebytes-content-filtering-api-openapi.yml
  - type: Documentation
    url: https://api.threatdown.com/nebula/v1/docs
  - type: APIReference
    url: https://api.threatdown.com/nebula/v1/docs
  - type: Documentation
    url: https://cloud.malwarebytes.com/api/v2/oneview/docs
- aid: malwarebytes:malwarebytes-copilot-api
  name: Malwarebytes Copilot API
  description: The Copilot API from Malwarebytes — 10 operation(s) for copilot.
  humanURL: https://api.threatdown.com/nebula/v1/docs
  baseURL: https://api.threatdown.com
  tags:
  - Copilot
  properties:
  - type: OpenAPI
    url: openapi/malwarebytes-copilot-api-openapi.yml
  - type: Documentation
    url: https://api.threatdown.com/nebula/v1/docs
  - type: APIReference
    url: https://api.threatdown.com/nebula/v1/docs
  - type: Documentation
    url: https://cloud.malwarebytes.com/api/v2/oneview/docs
- aid: malwarebytes:malwarebytes-detections-api
  name: Malwarebytes Detections API
  description: "Detections contain information on threats such as malware, ransomware, and malicious URLs found across your\
    \ account. \n\nUse the detection APIs to export detection data and retrieve details about a specific detection."
  humanURL: https://api.threatdown.com/nebula/v1/docs
  baseURL: https://api.threatdown.com
  tags:
  - Detections
  properties:
  - type: OpenAPI
    url: openapi/malwarebytes-detections-api-openapi.yml
  - type: Documentation
    url: https://api.threatdown.com/nebula/v1/docs
  - type: APIReference
    url: https://api.threatdown.com/nebula/v1/docs
  - type: Documentation
    url: https://cloud.malwarebytes.com/api/v2/oneview/docs
- aid: malwarebytes:malwarebytes-device-control-api
  name: Malwarebytes Device Control API
  description: 'The Device Control feature manages access to USB storage drives. Activity is logged every time a USB device
    is blocked or restricted to read-only.


    Use the Device Control APIs to export device control activity, obtain information about a specific device control event,
    search for device control events, and view device control activity grouped by a selected parameter.


    If your endpoints are running Endpoint Agent version 2.0.0.81 or newer, you can utilize the APIs that manage the Allowlist,
    or exclusions, for Device Control. The Allowlist provides the ability to override policy controls and prevent certain
    USB devices from being blocked by Device Control.'
  humanURL: https://api.threatdown.com/nebula/v1/docs
  baseURL: https://api.threatdown.com
  tags:
  - Device Control
  properties:
  - type: OpenAPI
    url: openapi/malwarebytes-device-control-api-openapi.yml
  - type: Documentation
    url: https://api.threatdown.com/nebula/v1/docs
  - type: APIReference
    url: https://api.threatdown.com/nebula/v1/docs
  - type: Documentation
    url: https://cloud.malwarebytes.com/api/v2/oneview/docs
- aid: malwarebytes:malwarebytes-dns-api
  name: Malwarebytes DNS API
  description: The DNS API from Malwarebytes — 4 operation(s) for dns.
  humanURL: https://api.threatdown.com/nebula/v1/docs
  baseURL: https://api.threatdown.com
  tags:
  - DNS
  properties:
  - type: OpenAPI
    url: openapi/malwarebytes-dns-api-openapi.yml
  - type: Documentation
    url: https://api.threatdown.com/nebula/v1/docs
  - type: APIReference
    url: https://api.threatdown.com/nebula/v1/docs
  - type: Documentation
    url: https://cloud.malwarebytes.com/api/v2/oneview/docs
- aid: malwarebytes:malwarebytes-dns-logs-api
  name: Malwarebytes DNS Logs API
  description: 'The DNS Filtering module limits the number of domain-based threats in your environment by allowing and blocking
    access across the network. Each time this occurs, a record is generated.


    Use these APIs to export the DNS activity and search through the logs.'
  humanURL: https://api.threatdown.com/nebula/v1/docs
  baseURL: https://api.threatdown.com
  tags:
  - DNS Logs
  properties:
  - type: OpenAPI
    url: openapi/malwarebytes-dns-logs-api-openapi.yml
  - type: Documentation
    url: https://api.threatdown.com/nebula/v1/docs
  - type: APIReference
    url: https://api.threatdown.com/nebula/v1/docs
  - type: Documentation
    url: https://cloud.malwarebytes.com/api/v2/oneview/docs
- aid: malwarebytes:malwarebytes-drive-encryption-api
  name: Malwarebytes Drive Encryption API
  description: The Drive Encryption API from Malwarebytes — 5 operation(s) for drive encryption.
  humanURL: https://api.threatdown.com/nebula/v1/docs
  baseURL: https://api.threatdown.com
  tags:
  - Drive Encryption
  properties:
  - type: OpenAPI
    url: openapi/malwarebytes-drive-encryption-api-openapi.yml
  - type: Documentation
    url: https://api.threatdown.com/nebula/v1/docs
  - type: APIReference
    url: https://api.threatdown.com/nebula/v1/docs
  - type: Documentation
    url: https://cloud.malwarebytes.com/api/v2/oneview/docs
- aid: malwarebytes:malwarebytes-email-protection-api
  name: Malwarebytes Email Protection API
  description: The Email Protection API from Malwarebytes — 79 operation(s) for email protection.
  humanURL: https://api.threatdown.com/nebula/v1/docs
  baseURL: https://api.threatdown.com
  tags:
  - Email Protection
  properties:
  - type: OpenAPI
    url: openapi/malwarebytes-email-protection-api-openapi.yml
  - type: Documentation
    url: https://api.threatdown.com/nebula/v1/docs
  - type: APIReference
    url: https://api.threatdown.com/nebula/v1/docs
  - type: Documentation
    url: https://cloud.malwarebytes.com/api/v2/oneview/docs
- aid: malwarebytes:malwarebytes-endpoints-api
  name: Malwarebytes Endpoints API
  description: '## Endpoints Introduction


    An Endpoint is a device which has the ThreatDown Endpoint Agent installed. Currently, there are available Endpoint Agents
    for Windows, macOS, and Linux. Refer to the installation guide for more information on registering a new Endpoint.


    Using the Endpoint API, you can search your registered endpoints and retrieve their last known status. The API allows
    you to perform advanced queries and offers grouping capabilities so that you can perform deep analysis of your company''s
    devices and the found threats, such as Detections or Suspicious Activities.


    You can scan, isolate, remediate, and reboot your endpoints remotely through the Job APIs.


    ## How to deploy an endpoint agent


    **Endpoint software can be installed in the following ways**:


    - Active Directory (AD) Group Policy

    - System Center Configuration Manager (SCCM)

    - Third-party deployment tools

    - Manually on the endpoints

    - Discovery & Deployment Tool


    Once the installation is complete, the endpoints will be displayed in the console.


    You can retrieve installers for your account through the `Installers` APIs.'
  humanURL: https://api.threatdown.com/nebula/v1/docs
  baseURL: https://api.threatdown.com
  tags: []
  tags_raw:
  - Endpoints
  properties:
  - type: OpenAPI
    url: openapi/malwarebytes-endpoints-api-openapi.yml
  - type: Documentation
    url: https://api.threatdown.com/nebula/v1/docs
  - type: APIReference
    url: https://api.threatdown.com/nebula/v1/docs
  - type: Documentation
    url: https://cloud.malwarebytes.com/api/v2/oneview/docs
- aid: malwarebytes:malwarebytes-events-api
  name: Malwarebytes Events API
  description: An event is a general term for a threat that has occurred, remediation or other action taken on a threat, and
    other endpoint-related activity.
  humanURL: https://api.threatdown.com/nebula/v1/docs
  baseURL: https://api.threatdown.com
  tags:
  - Event
  tags_raw:
  - Events
  properties:
  - type: OpenAPI
    url: openapi/malwarebytes-events-api-openapi.yml
  - type: Documentation
    url: https://api.threatdown.com/nebula/v1/docs
  - type: APIReference
    url: https://api.threatdown.com/nebula/v1/docs
  - type: Documentation
    url: https://cloud.malwarebytes.com/api/v2/oneview/docs
- aid: malwarebytes:malwarebytes-exclusions-api
  name: Malwarebytes Exclusions API
  description: 'Exclusions allow you to prevent trusted applications, websites, and services from being detected by our security
    engine. This means they won''t be scanned or blocked.


    Use these APIs to manage the exclusions across your account.'
  humanURL: https://api.threatdown.com/nebula/v1/docs
  baseURL: https://api.threatdown.com
  tags:
  - Exclusions
  properties:
  - type: OpenAPI
    url: openapi/malwarebytes-exclusions-api-openapi.yml
  - type: Documentation
    url: https://api.threatdown.com/nebula/v1/docs
  - type: APIReference
    url: https://api.threatdown.com/nebula/v1/docs
  - type: Documentation
    url: https://cloud.malwarebytes.com/api/v2/oneview/docs
- aid: malwarebytes:malwarebytes-firewall-management-api
  name: Malwarebytes Firewall Management API
  description: The Firewall Management API from Malwarebytes — 20 operation(s) for firewall management.
  humanURL: https://api.threatdown.com/nebula/v1/docs
  baseURL: https://api.threatdown.com
  tags:
  - Firewall Management
  properties:
  - type: OpenAPI
    url: openapi/malwarebytes-firewall-management-api-openapi.yml
  - type: Documentation
    url: https://api.threatdown.com/nebula/v1/docs
  - type: APIReference
    url: https://api.threatdown.com/nebula/v1/docs
  - type: Documentation
    url: https://cloud.malwarebytes.com/api/v2/oneview/docs
- aid: malwarebytes:malwarebytes-flight-recorder-api
  name: Malwarebytes Flight Recorder API
  description: "EDR customers can use Flight Recorder to search event data captured on endpoints that have suspicious activity\
    \ monitoring enabled. \n\nUse these APIs to search through files, registry, processes, networking activity, and suspicious\
    \ activities. This information can be used to investigate or identify indicators of compromise."
  humanURL: https://api.threatdown.com/nebula/v1/docs
  baseURL: https://api.threatdown.com
  tags:
  - Flight-recorder
  properties:
  - type: OpenAPI
    url: openapi/malwarebytes-flight-recorder-api-openapi.yml
  - type: Documentation
    url: https://api.threatdown.com/nebula/v1/docs
  - type: APIReference
    url: https://api.threatdown.com/nebula/v1/docs
  - type: Documentation
    url: https://cloud.malwarebytes.com/api/v2/oneview/docs
- aid: malwarebytes:malwarebytes-grid-api
  name: Malwarebytes Grid API
  description: "# Grid Introduction\n\nUsing the following API, you can search endpoints, detections, software inventory,\
    \ vulnerabilities, rid rules, os-patches, device control events and dns logs. This API allows to perform filtering, sorting,\
    \ grouping and aggregating of data by specifying constraints based on the field type.\n\nAvailable constraints for searching\
    \ based on value type\n\n| Value Type | Constraints |\n| --- |----|\n| Simple String | equals, not_equals, contains, not_contains\
    \ |\n| String (with enum) | equals, not_equals |\n| String/UUID (entity reference) | equals, not_equals |\n| Version |\
    \ equals, not_equals |\n| Number | gt, lt, gte, lte |\n| Timestamp | start, end |\n| IP | ip |\n| Boolean | equals, not_equals\
    \ |\n\nGrid API also supports compound constraints that can be constructed with the keywords **allOf**, **anyOf**, **noneOf**\n\
    \nExample of compound constraint:\n\n```json\n{\n\"constraints\": [\n  {\n    \"allOf\": [\n      {\n        \"field\"\
    : \"agent.host_name\",\n        \"operator\": \"contains\",\n        \"value\": \"a\"\n      },\n      {\n          \"\
    field\": \"machine.is_deleted\",\n          \"operator\": \"equals\",\n          \"value\": false\n      },\n      {\n\
    \        \"anyOf\": [\n          {\n            \"field\": \"agent.os_info.os_platform\",\n            \"operator\": \"\
    equals\",\n            \"value\": \"Linux\"\n          },\n          {\n            \"field\": \"agent.os_info.os_platform\"\
    ,\n            \"operator\": \"equals\",\n            \"value\": \"MacOS\"\n          }\n        ]\n      }\n    ]\n \
    \ }\n]\n}\n```\nIn this example all the records that contain **a** in the ***agent.host_name***, have ***machine.is_deleted***\
    \ set to false and whose ***os_platform*** is equal to **either** ***Linux*** or ***MacOS*** will be returned."
  humanURL: https://api.threatdown.com/nebula/v1/docs
  baseURL: https://api.threatdown.com
  tags:
  - Grid
  properties:
  - type: OpenAPI
    url: openapi/malwarebytes-grid-api-openapi.yml
  - type: Documentation
    url: https://api.threatdown.com/nebula/v1/docs
  - type: APIReference
    url: https://api.threatdown.com/nebula/v1/docs
  - type: Documentation
    url: https://cloud.malwarebytes.com/api/v2/oneview/docs
- aid: malwarebytes:malwarebytes-groups-api
  name: Malwarebytes Groups API
  description: 'Groups are used to contain and organize endpoints. Policies, which determine the software settings, and endpoints,
    are assigned to groups. Endpoints use the policies in the groups they are assigned to determine which software settings
    are enabled.


    Use these APIs to create, manage, and move endpoints into groups.'
  humanURL: https://api.threatdown.com/nebula/v1/docs
  baseURL: https://api.threatdown.com
  tags:
  - Group
  tags_raw:
  - Groups
  properties:
  - type: OpenAPI
    url: openapi/malwarebytes-groups-api-openapi.yml
  - type: Documentation
    url: https://api.threatdown.com/nebula/v1/docs
  - type: APIReference
    url: https://api.threatdown.com/nebula/v1/docs
  - type: Documentation
    url: https://cloud.malwarebytes.com/api/v2/oneview/docs
- aid: malwarebytes:malwarebytes-ignore-rules-api
  name: Malwarebytes Ignore Rules API
  description: The Ignore Rules API from Malwarebytes — 4 operation(s) for ignore rules.
  humanURL: https://api.threatdown.com/nebula/v1/docs
  baseURL: https://api.threatdown.com
  tags:
  - Ignore Rules
  properties:
  - type: OpenAPI
    url: openapi/malwarebytes-ignore-rules-api-openapi.yml
  - type: Documentation
    url: https://api.threatdown.com/nebula/v1/docs
  - type: APIReference
    url: https://api.threatdown.com/nebula/v1/docs
  - type: Documentation
    url: https://cloud.malwarebytes.com/api/v2/oneview/docs
- aid: malwarebytes:malwarebytes-info-api
  name: Malwarebytes Info API
  description: The Info API from Malwarebytes — 1 operation(s) for info.
  humanURL: https://api.threatdown.com/nebula/v1/docs
  baseURL: https://api.threatdown.com
  tags:
  - Info
  properties:
  - type: OpenAPI
    url: openapi/malwarebytes-info-api-openapi.yml
  - type: Documentation
    url: https://api.threatdown.com/nebula/v1/docs
  - type: APIReference
    url: https://api.threatdown.com/nebula/v1/docs
  - type: Documentation
    url: https://cloud.malwarebytes.com/api/v2/oneview/docs
- aid: malwarebytes:malwarebytes-installation-tokens-api
  name: Malwarebytes Installation Tokens API
  description: Use these APIs to generate, send, and revoke installation tokens used to activate Mobile Security for Business.
  humanURL: https://api.threatdown.com/nebula/v1/docs
  baseURL: https://api.threatdown.com
  tags:
  - Installation Tokens
  properties:
  - type: OpenAPI
    url: openapi/malwarebytes-installation-tokens-api-openapi.yml
  - type: Documentation
    url: https://api.threatdown.com/nebula/v1/docs
  - type: APIReference
    url: https://api.threatdown.com/nebula/v1/docs
  - type: Documentation
    url: https://cloud.malwarebytes.com/api/v2/oneview/docs
- aid: malwarebytes:malwarebytes-installers-api
  name: Malwarebytes Installers API
  description: The Installers APIs allow you to deploy the endpoint agent to Windows and macOS devices.
  humanURL: https://api.threatdown.com/nebula/v1/docs
  baseURL: https://api.threatdown.com
  tags:
  - Installers
  properties:
  - type: OpenAPI
    url: openapi/malwarebytes-installers-api-openapi.yml
  - type: Documentation
    url: https://api.threatdown.com/nebula/v1/docs
  - type: APIReference
    url: https://api.threatdown.com/nebula/v1/docs
  - type: Documentation
    url: https://cloud.malwarebytes.com/api/v2/oneview/docs
- aid: malwarebytes:malwarebytes-itdr-api
  name: Malwarebytes ITDR API
  description: The ITDR API from Malwarebytes — 29 operation(s) for itdr.
  humanURL: https://api.threatdown.com/nebula/v1/docs
  baseURL: https://api.threatdown.com
  tags:
  - ITDR
  properties:
  - type: OpenAPI
    url: openapi/malwarebytes-itdr-api-openapi.yml
  - type: Documentation
    url: https://api.threatdown.com/nebula/v1/docs
  - type: APIReference
    url: https://api.threatdown.com/nebula/v1/docs
  - type: Documentation
    url: https://cloud.malwarebytes.com/api/v2/oneview/docs
- aid: malwarebytes:malwarebytes-jobs-api
  name: Malwarebytes Jobs API
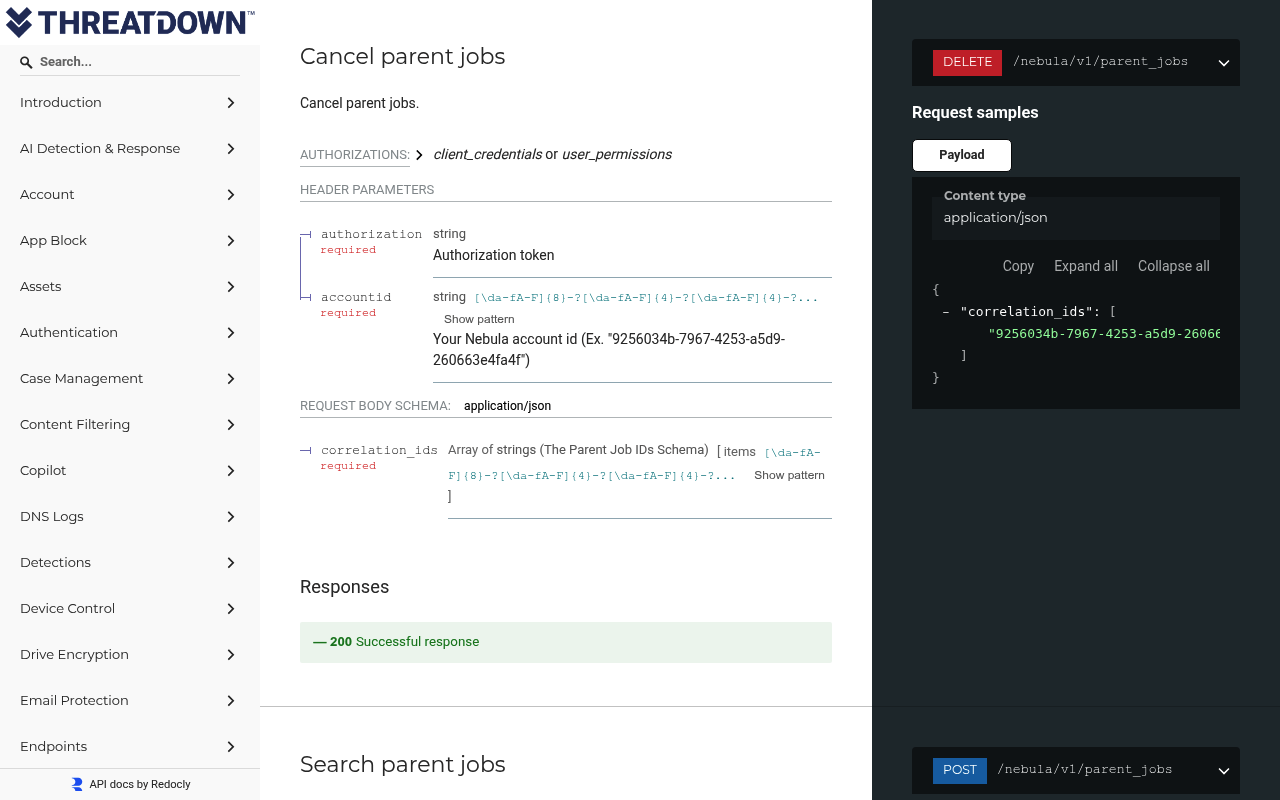
  description: Jobs are tasks that are issued to endpoints. Use these APIs to manage, search, and export jobs.
  humanURL: https://api.threatdown.com/nebula/v1/docs
  baseURL: https://api.threatdown.com
  tags:
  - Job
  tags_raw:
  - Jobs
  properties:
  - type: OpenAPI
    url: openapi/malwarebytes-jobs-api-openapi.yml
  - type: Documentation
    url: https://api.threatdown.com/nebula/v1/docs
  - type: APIReference
    url: https://api.threatdown.com/nebula/v1/docs
  - type: Documentation
    url: https://cloud.malwarebytes.com/api/v2/oneview/docs
- aid: malwarebytes:malwarebytes-licensing-api
  name: Malwarebytes Licensing API
  description: The Licensing API from Malwarebytes — 1 operation(s) for licensing.
  humanURL: https://api.threatdown.com/nebula/v1/docs
  baseURL: https://api.threatdown.com
  tags:
  - Licensing
  properties:
  - type: OpenAPI
    url: openapi/malwarebytes-licensing-api-openapi.yml
  - type: Documentation
    url: https://api.threatdown.com/nebula/v1/docs
  - type: APIReference
    url: https://api.threatdown.com/nebula/v1/docs
  - type: Documentation
    url: https://cloud.malwarebytes.com/api/v2/oneview/docs
- aid: malwarebytes:malwarebytes-mdr-api
  name: Malwarebytes MDR API
  description: The MDR API from Malwarebytes — 2 operation(s) for mdr.
  humanURL: https://api.threatdown.com/nebula/v1/docs
  baseURL: https://api.threatdown.com
  tags:
  - MDR
  properties:
  - type: OpenAPI
    url: openapi/malwarebytes-mdr-api-openapi.yml
  - type: Documentation
    url: https://api.threatdown.com/nebula/v1/docs
  - type: APIReference
    url: https://api.threatdown.com/nebula/v1/docs
  - type: Documentation
    url: https://cloud.malwarebytes.com/api/v2/oneview/docs
- aid: malwarebytes:malwarebytes-mxdr-api
  name: Malwarebytes MXDR API
  description: The MXDR API from Malwarebytes — 4 operation(s) for mxdr.
  humanURL: https://api.threatdown.com/nebula/v1/docs
  baseURL: https://api.threatdown.com
  tags:
  - MXDR
  properties:
  - type: OpenAPI
    url: openapi/malwarebytes-mxdr-api-openapi.yml
  - type: Documentation
    url: https://api.threatdown.com/nebula/v1/docs
  - type: APIReference
    url: https://api.threatdown.com/nebula/v1/docs
  - type: Documentation
    url: https://cloud.malwarebytes.com/api/v2/oneview/docs


# --- truncated at 32 KB (134 KB total) ---
# Full source: https://artifacts.apis.io/malwarebytes/apis.yml
Malwarebytes API — frequently asked questions
Does Malwarebytes have an API?
Yes. APIs.io lists 52 APIs from Malwarebytes, including Malwarebytes Account API, Malwarebytes AI Detection & Response API and Malwarebytes App Block API, and 49 more.
Is there an OpenAPI specification for the Malwarebytes API?
Yes. APIs.io indexes 52 OpenAPI specifications for Malwarebytes, each linked for download from this page.
How do I authenticate with the Malwarebytes API?
Malwarebytes documents its authentication (2 schemes). The details are profiled on APIs.io as Malwarebytes Authentication.
How much does the Malwarebytes API cost?
Malwarebytes publishes its prices; its Standard plan is Billed $47.93 for the first year* as of 2026-10-20. APIs.io lists 4 pricing plans for Malwarebytes, with each plan's price, limits and inclusions under Pricing on this page.
Is the Malwarebytes API ready for AI agents?
Malwarebytes has a Kin Score of 70.9 out of 100 (exemplar) and an Agent Readiness score of 29.7 (agent-ready), scored by API Evangelist on 2026-11-06.
Calls without X-API-Key need no key. Calls with it need a paid plan — get a key.
Get an API key
Free tier, no form to fill in. Signing in shares your email address with us — we
store it to create your key and to recognise you if you sign in with another
provider. See our Privacy Policy and
Terms.
 Kin Score
How this is scored →
 It updates itself when the score changes. Paste this where you link to your API docs: