Cequence Security delivers the Unified API Protection (UAP) platform, combining external API attack-surface discovery, posture and compliance analysis, inline runtime protection, and testing into a single solution for defending web applications, APIs, and AI endpoints against business logic abuse, bot attacks, and fraud. The Cequence product family is organized into API Spyder (agentless external discovery), API Sentinel (API inventory, posture, and compliance), API Spartan (runtime bot and abuse defense), API Security Testing (shift-left OpenAPI conformance and vulnerability testing), and Cequence Defender (inline reverse-proxy enforcement of API policy).
Cequence Security is listed with 6 APIs on the APIs.io network. Tagged areas include AI Protection, API Discovery, API Security, Application Security, and Attack Surface.
Cequence Security’s developer surface includes engineering blog, documentation, API reference, and 25 more developer resources.
Regulatory Posture applies to this provider. Its tags matched the
Horizontal (data, software, accessibility, platform) regime, so
Regulatory Posture carries 15 points of the composite.
If this regime is wrong for your business, say so on your
provider repo — the
applicability map is public and we will correct it.
Create-or-Update Ergonomics could not be measured. We hold no machine-readable contract for
this provider to read, so there is nothing to measure a write surface against. Excluded rather than scored zero:
never-measured and measured-empty are different facts. Publishing an OpenAPI is what makes this facet — and
several others — scorable at all.
The six quality facets above are damped to 85 points between them,
because the conditional facet above carries the other
15. That is why each facet's contribution is shown against a damped
maximum: raising a quality facet moves the composite by 85% of its nominal
weight, not 100%. The full arithmetic is at apis.io/rating/.
Show this score on your site.
It updates itself when the score changes. Paste this where you link to your API docs:
<a href="https://apis.io/providers/cequence/"><img src="https://apis.io/badge/cequence/card.svg" alt="Cequence Security on APIs.io — Kin Score by API Evangelist"></a>
Other styles, a README pill and a shields.io endpoint are on the badge page.
Raise your score.
Agent readiness — checks not met, largest first (exact, from this profile):
Idempotency+9 pts — OpenAPI mutating operations declare an idempotency key — a header, a request-body property, or a named de-duplication token whose own description says so (verified); else common[].type matches /idempoten/i (documented)
A2A Agent Card+8 pts — a2a/-a2a.yml manifest, graded on conformance.grade against A2A 1.0.0
Request/Response Examples+7 pts — share of operations carrying request/response examples; else an Examples / Code Samples link
Typed Event Surface+6 pts — AsyncAPI document, OR webhooks/callbacks objects in the as-published OpenAPI, OR common[].type includes Webhooks
5 more unmet checks in the Agent Readiness table above.
Kin Score — facets with the most composite points still available (weight × headroom):
Standards this provider implements or carries. De facto ones are profiled and measured by the API Commons; formal ones come from the standards directory and are linked by the provider's own tags. The evidence column says how each claim was established — not that it was made.
API Spyder is a SaaS-based, agentless external discovery service that provides an attacker's view into an organization's public-facing API hosts, hosting providers, and API-spec...
API Sentinel is the Cequence API posture and compliance module that continuously inventories internal and external APIs, classifies sensitive data flows, scores API risk against...
API Spartan provides runtime protection against malicious and unwanted API traffic, including account takeover, credential stuffing, scraping, gift-card fraud, and other busines...
API Security Testing extends Cequence into shift-left, performing pre-production OpenAPI conformance and vulnerability testing against the OWASP API Security Top 10, feeding res...
Cequence Defender is a reverse-proxy deployed inline with API traffic, enforcing API policies, filtering malicious traffic, and providing real-time detection and mitigation thro...
Enterprise AI Gateway that makes applications agent-ready through governed Model Context Protocol integration. Register a REST API from its OpenAPI spec (or proxy a third-party ...
aid: cequence
url: https://raw.githubusercontent.com/api-evangelist/cequence/refs/heads/main/apis.yml
name: Cequence Security
x-docs-platform: docusaurus
x-docs-platform-confidence: medium
x-docs-platform-checked: 2026-09-21
x-docs-hosting: firebase
tags:
- AI Protection
- API Discovery
- API Security
- Application Security
- Attack Surface
- Bot Management
- Business Logic Abuse
- CNAPP
- Cybersecurity
- Fraud Prevention
- Unified API Protection
tags_raw:
- AI Protection
- API Discovery
- API Security
- Application Security
- Attack Surface
- Bot Management
- Business Logic Abuse
- CNAPP
- Cybersecurity
- Fraud
- Unified API Protection
type: Index
deliveryModel:
  model: unknown
  open_source: false
  commercial: false
  callable_host: false
  label: Delivery model not determined — needs a product licence on record
  confidence: low
  source:
  - none
  generated: '2026-08-28'
  method: derived
accessModel:
  pricing: unknown
  onboarding: unknown
  trial: false
  try_now: false
  public: false
  label: Unknown
  confidence: low
  source:
  - authentication
  - scopes
  - rate-limits
  - security
  generated: '2026-11-06'
  method: derived
image: https://kinlane-images.s3.amazonaws.com/shared/apis-json/icons/cequence.png
access: 3rd-Party
created: '2025-01-08'
modified: '2026-09-05'
position: Consuming
specificationVersion: '0.23'
description: Cequence Security delivers the Unified API Protection (UAP) platform, combining external API attack-surface discovery,
  posture and compliance analysis, inline runtime protection, and testing into a single solution for defending web applications,
  APIs, and AI endpoints against business logic abuse, bot attacks, and fraud. The Cequence product family is organized into
  API Spyder (agentless external discovery), API Sentinel (API inventory, posture, and compliance), API Spartan (runtime bot
  and abuse defense), API Security Testing (shift-left OpenAPI conformance and vulnerability testing), and Cequence Defender
  (inline reverse-proxy enforcement of API policy).
apis:
- aid: cequence:cequence-api-spyder
  name: Cequence API Spyder
  tags:
  - Attack Surface Management
  - Discovery
  - External Scanning
  - Shadow APIs
  humanURL: https://www.cequence.ai/products/api-spyder/
  properties:
  - url: https://www.cequence.ai/products/api-spyder/
    type: Website
  - url: https://www.cequence.ai/wp-content/uploads/2022/06/cequence-ds-apispyder.pdf
    type: Datasheet
  - url: https://www.cequence.ai/apispyder-demo/
    type: Demo
  description: API Spyder is a SaaS-based, agentless external discovery service that provides an attacker's view into an organization's
    public-facing API hosts, hosting providers, and API-specific exposures including weak TLS and shadow APIs. Crawls can
    be on-demand or scheduled for continuous external attack-surface monitoring.
- aid: cequence:cequence-api-sentinel
  name: Cequence API Sentinel
  tags:
  - API Inventory
  - Compliance
  - Posture
  - Risk Management
  - Sensitive Data
  tags_raw:
  - API Inventory
  - Compliance
  - Posture
  - Risk
  - Sensitive Data
  humanURL: https://www.cequence.ai/products/
  properties:
  - url: https://www.cequence.ai/products/
    type: Website
  - url: https://helpdesk.cequence.ai/
    type: HelpCenter
  description: API Sentinel is the Cequence API posture and compliance module that continuously inventories internal and external
    APIs, classifies sensitive data flows, scores API risk against governance policies, and generates remediation guidance
    for security and platform teams.
- aid: cequence:cequence-api-spartan
  name: Cequence API Spartan
  tags:
  - ATO
  - Bot Management
  - Business Logic Abuse
  - Credential Stuffing
  - Fraud Prevention
  - Runtime
  tags_raw:
  - ATO
  - Bot Management
  - Business Logic Abuse
  - Credential Stuffing
  - Fraud
  - Runtime
  humanURL: https://www.cequence.ai/products/
  properties:
  - url: https://www.cequence.ai/products/
    type: Website
  - url: https://helpdesk.cequence.ai/hc/en-us/articles/19223960381719-Cequence-Unified-API-Protection-overview
    type: Documentation
  description: API Spartan provides runtime protection against malicious and unwanted API traffic, including account takeover,
    credential stuffing, scraping, gift-card fraud, and other business logic abuse, with ML-driven detection and mitigation
    actions such as blocking, rate limiting, and deception.
- aid: cequence:cequence-api-security-testing
  name: Cequence API Security Testing
  tags:
  - Conformance
  - DAST
  - OWASP API Top 10
  - Pre-Production
  - Testing
  humanURL: https://www.cequence.ai/blog/cequence-product-news/announcing-unified-api-protection-v2-0/
  properties:
  - url: https://www.cequence.ai/blog/cequence-product-news/announcing-unified-api-protection-v2-0/
    type: Announcement
  - url: https://www.cequence.ai/products/
    type: Website
  description: API Security Testing extends Cequence into shift-left, performing pre-production OpenAPI conformance and vulnerability
    testing against the OWASP API Security Top 10, feeding results back into Sentinel and Spartan for continuous lifecycle
    protection.
- aid: cequence:cequence-defender
  name: Cequence Defender
  tags:
  - Enforcement
  - Inline
  - Policy
  - Reverse Proxy
  - Runtime
  humanURL: https://helpdesk.cequence.ai/hc/en-us/articles/19223960381719-Cequence-Unified-API-Protection-overview
  properties:
  - url: https://helpdesk.cequence.ai/hc/en-us/articles/19223960381719-Cequence-Unified-API-Protection-overview
    type: Documentation
  - url: https://www.cequence.ai/products/
    type: Website
  description: Cequence Defender is a reverse-proxy deployed inline with API traffic, enforcing API policies, filtering malicious
    traffic, and providing real-time detection and mitigation through active traffic inspection.
- name: Cequence AI Gateway
  description: Enterprise AI Gateway that makes applications agent-ready through governed Model Context Protocol integration.
    Register a REST API from its OpenAPI spec (or proxy a third-party remote MCP server) and the gateway publishes it as an
    MCP endpoint with inbound SSO/OAuth/API-key/JWT authentication, outbound credential injection (OAuth 2.1 authorization
    or client-credentials, API key, bearer, JWT bearer, basic, passthrough), per-tool rate limiting, DLP redaction, circuit
    breaking, agent personas that compose tools across servers, a SKILL.md skill registry, and audit export to Splunk HEC,
    Datadog, OTLP or syslog. Cequence also operates a first-party hosted MCP server, provisioned for every tenant, that manages
    the gateway itself from any agent.
  humanURL: https://docs.aigateway.cequence.ai/docs/introduction
  baseURL: https://aigateway.cequence.ai
  tags:
  - AI Gateway
  - MCP
  - AI Agents
  - API Security
  - API Governance
  - Agent-Native
  tags_raw:
  - ai-gateway
  - model-context-protocol
  - agentic-ai
  - api-security
  - api-governance
  - agent-native
  - Agentic AI
  properties:
  - type: Documentation
    url: https://docs.aigateway.cequence.ai/docs/introduction
  - type: APIReference
    url: https://docs.aigateway.cequence.ai/docs/remote-mcp-servers/cequence-ai-gateway
  - type: GettingStarted
    url: https://docs.aigateway.cequence.ai/docs/getstarted
  - type: MCPServer
    url: mcp/cequence-mcp.yml
  - type: Documentation
    url: https://docs.aigateway.cequence.ai/docs/remote-mcp-servers/cequence-ai-gateway
  - type: Authentication
    url: authentication/cequence-authentication.yml
  - type: Conventions
    url: conventions/cequence-conventions.yml
  - type: RateLimits
    url: rate-limits/cequence-rate-limits.yml
  - type: ErrorCatalog
    url: errors/cequence-problem-types.yml
  - type: CLI
    url: cli/cequence-cli.yml
  - type: LLMsTxt
    url: llms/cequence-ai-gateway-llms.txt
  - type: Website
    url: https://www.cequence.ai/products/ai-gateway/
  - type: OAuthScopes
    url: scopes/cequence-scopes.yml
  - type: AgentSkill
    url: skills/_index.yml
  - type: WellKnown
    url: well-known/cequence-well-known.yml
common:
- type: RateLimits
  url: rate-limits/cequence-rate-limits.yml
- type: FinOps
  url: finops/cequence-finops.yml
- type: TrustCenter
  url: security/cequence-trust-center.yml
- type: DomainSecurity
  url: security/cequence-domain-security.yml
- type: LinkedIn
  url: https://www.linkedin.com/company/cequence-security
- type: Website
  url: https://www.cequence.ai/
- type: Solutions
  url: https://www.cequence.ai/products/
- type: HelpCenter
  url: https://helpdesk.cequence.ai/
- type: Blog
  url: https://www.cequence.ai/blog/
- type: Newsroom
  url: https://www.cequence.ai/newsroom/
- type: PrivacyPolicy
  url: https://www.cequence.ai/privacy/
- type: LlmsText
  url: https://www.cequence.ai/llms.txt
- type: DeveloperPortal
  url: https://aigateway.cequence.ai
- type: Documentation
  url: https://docs.aigateway.cequence.ai/docs/introduction
- type: APIReference
  url: https://docs.aigateway.cequence.ai/docs/remote-mcp-servers/cequence-ai-gateway
- type: GitHubOrganization
  url: https://github.com/cequenceai
- type: WellKnown
  url: well-known/cequence-well-known.yml
- type: Packages
  url: packages/cequence-packages.yml
- type: SDKs
  url: packages/cequence-packages.yml
- type: OAuthScopes
  url: scopes/cequence-scopes.yml
- type: Conformance
  url: conformance/cequence-conformance.yml
- type: Compliance
  url: https://www.cequence.ai/compliance/
- type: Lifecycle
  url: lifecycle/cequence-lifecycle.yml
- type: VulnerabilityDisclosure
  url: security/cequence-vulnerability-disclosure.yml
- type: Security
  url: https://www.cequence.ai/responsible-disclosure-policy/
- type: AgentSkill
  url: skills/_index.yml
- type: Plans
  url: plans/cequence-plans-pricing.yml
- type: TermsOfService
  url: https://www.cequence.ai/legal/saas-ai-gateway-end-user-license-agreement/
- type: Login
  url: https://aigateway.cequence.ai/login
maintainers:
- FN: Kin Lane
  email: kin@apievangelist.com
x-enrichment:
  date: '2026-09-05'
  status: enriched
  artifacts_added: 19
  pass: local-v3
Cequence Security API — frequently asked questions
Does Cequence Security have an API?
Yes. APIs.io lists 6 APIs from Cequence Security, including Cequence API Spyder, Cequence API Sentinel and Cequence API Spartan, and 3 more.
How do I authenticate with the Cequence Security API?
Cequence Security documents its authentication (oauth2/openIdConnect/apiKey/http · 12 schemes). The details are profiled on APIs.io as Cequence Authentication.
Does Cequence Security have an MCP server?
Yes. APIs.io lists 1 MCP server for Cequence Security: Remote MCP server at mcp.aigateway.cequence.ai over HTTP requiring OAuth; 25 tools listed.
Is the Cequence Security API ready for AI agents?
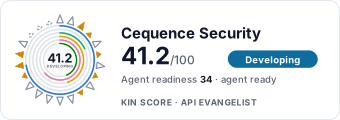
Cequence Security has a Kin Score of 41.2 out of 100 (developing) and an Agent Readiness score of 33.6 (agent-ready), scored by API Evangelist on 2026-11-06.
Calls without X-API-Key need no key. Calls with it need a paid plan — get a key.
Get an API key
Free tier, no form to fill in. Signing in shares your email address with us — we
store it to create your key and to recognise you if you sign in with another
provider. See our Privacy Policy and
Terms.
 Kin Score
How this is scored →
 It updates itself when the score changes. Paste this where you link to your API docs: