The Chief Information Officers Council (CIOC) is the principal interagency forum for improving agency practices related to the design, acquisition, development, modernization, use, sharing, and performance of federal information resources. Established by Executive Order 13011 in 1996 and codified in the E-Government Act of 2002 (44 U.S.C. 3603), the Council is comprised of the Chief Information Officers and Deputy CIOs of executive branch agencies, the Federal CIO at OMB (who serves as Chair), the Federal Chief Information Security Officer, and the Administrator for Electronic Government. The CIOC develops recommendations for OMB IT policy, identifies opportunities to improve federal IT performance, coordinates multi-agency IT initiatives such as cybersecurity and cloud adoption, supports federal IT workforce development, and disseminates effective IT management practices across the federal government. The Council publishes guidance, playbooks, committee output and its charter through councils.gov, the consolidated federal executive councils hub GSA launched in March 2026; its long-standing home at cio.gov now redirects there. The Council operates no developer program and publishes no API.
Chief Information Officers Council is listed with 1 API on the APIs.io network. Tagged areas include CIO, Cloud, Cybersecurity, E-Government, and Federal Government.
Regulatory Posture applies to this provider. Its tags matched the
Government & Public Sector regime, so
Regulatory Posture carries 15 points of the composite.
If this regime is wrong for your business, say so on your
provider repo — the
applicability map is public and we will correct it.
Create-or-Update Ergonomics could not be measured. We hold no machine-readable contract for
this provider to read, so there is nothing to measure a write surface against. Excluded rather than scored zero:
never-measured and measured-empty are different facts. Publishing an OpenAPI is what makes this facet — and
several others — scorable at all.
The six quality facets above are damped to 85 points between them,
because the conditional facet above carries the other
15. That is why each facet's contribution is shown against a damped
maximum: raising a quality facet moves the composite by 85% of its nominal
weight, not 100%. The full arithmetic is at apis.io/rating/.
Show this score on your site.
It updates itself when the score changes. Paste this where you link to your API docs:
<a href="https://apis.io/providers/chief-information-officers-council/"><img src="https://apis.io/badge/chief-information-officers-council/card.svg" alt="Chief Information Officers Council on APIs.io — Kin Score by API Evangelist"></a>
Other styles, a README pill and a shields.io endpoint are on the badge page.
Raise your score.
Agent readiness — checks not met, largest first (exact, from this profile):
Machine-Readable Auth+10 pts — a served openid-configuration/oauth-authorization-server carrying `issuer` (served), else the securitySchemes class in the provider OpenAPIs — bound (mutualTLS, DPoP, Signature) > negotiable (oauth2 authorizationCode/clientCredentials, openIdConnect) > bearer (http bearer, apiKey)
Idempotency+9 pts — OpenAPI mutating operations declare an idempotency key — a header, a request-body property, or a named de-duplication token whose own description says so (verified); else common[].type matches /idempoten/i (documented)
Stable Error Semantics+8 pts — OpenAPI $refs a shared error schema across 4xx/5xx responses (verified), else common[].type includes ErrorCatalog / ErrorCodes / DeclineCodes
12 more unmet checks in the Agent Readiness table above.
Kin Score — facets with the most composite points still available (weight × headroom):
The Kin Score Market layer reads a provider inside its market:
its position, and how deep its integrations go. Depth is only comparable within a position. Provisional and unweighted:
not part of the Kin Score or agent readiness.
Registered MCP server and declares compatibility are report only — not weighted.
Undeclared means we found nothing we can read, so there is no number: we never infer integrations.
The CIOC publishes its charter, leadership roster, committee output, playbooks (e.g., Cloud Smart, Modular Contracting, IT Modernization), and federal IT guidance through cio.go...
aid: chief-information-officers-council
name: Chief Information Officers Council
kind: government
description: The Chief Information Officers Council (CIOC) is the principal interagency forum for improving agency practices
  related to the design, acquisition, development, modernization, use, sharing, and performance of federal information resources.
  Established by Executive Order 13011 in 1996 and codified in the E-Government Act of 2002 (44 U.S.C. 3603), the Council
  is comprised of the Chief Information Officers and Deputy CIOs of executive branch agencies, the Federal CIO at OMB (who
  serves as Chair), the Federal Chief Information Security Officer, and the Administrator for Electronic Government. The CIOC
  develops recommendations for OMB IT policy, identifies opportunities to improve federal IT performance, coordinates multi-agency
  IT initiatives such as cybersecurity and cloud adoption, supports federal IT workforce development, and disseminates effective
  IT management practices across the federal government. The Council publishes guidance, playbooks, committee output and its
  charter through councils.gov, the consolidated federal executive councils hub GSA launched in March 2026; its long-standing
  home at cio.gov now redirects there. The Council operates no developer program and publishes no API.
type: Index
deliveryModel:
  model: saas
  license_evidence:
    not_product:
    - gsa/councils.gov
  open_source: unknown
  commercial: true
  callable_host: false
  label: Hosted service · you call their endpoint
  confidence: low
  source:
  - pricing
  - repository-not-product
  generated: '2026-09-25'
  method: derived
accessModel:
  pricing: unknown
  onboarding: unknown
  trial: false
  try_now: false
  public: false
  label: Unknown
  confidence: low
  probe_state: none
  source:
  - rate-limits
  - security
  generated: '2026-11-06'
  method: derived
position: Consuming
access: 3rd-Party
image: https://kinlane-images.s3.amazonaws.com/shared/apis-json/icons/chief-information-officers-council.png
url: https://raw.githubusercontent.com/api-evangelist/chief-information-officers-council/refs/heads/main/apis.yml
tags:
- CIO
- Cloud
- Cybersecurity
- E-Government
- Federal Government
- IT Modernization
- Information Technology
- Interagency Council
- OMB
- Public Sector
tags_raw:
- CIO
- Cloud
- Cybersecurity
- E-Government
- Federal Government
- IT Modernization
- Information Technology
- Interagency Council
- OMB
- Public Sector
- Federal-Government
created: '2024-12-03'
modified: '2026-09-05'
specificationVersion: '0.23'
apis:
- aid: chief-information-officers-council:cioc-resources
  name: Chief Information Officers Council Resources
  description: 'The CIOC publishes its charter, leadership roster, committee output, playbooks (e.g., Cloud Smart, Modular
    Contracting, IT Modernization), and federal IT guidance through cio.gov and councils.gov. The Council does not expose
    a dedicated developer API; resources are distributed as web pages, PDFs, and downloadable documents alongside OMB and
    GSA federal IT management resources. Probed 2026-09-05 across councils.gov, cio.gov and tmf.cio.gov: no OpenAPI, GraphQL,
    MCP, AsyncAPI, agent card or apis.json is served from any host in this record.'
  image: https://kinlane-images.s3.amazonaws.com/shared/apis-json/apis-json-logo.jpg
  humanURL: https://www.councils.gov/cioc
  tags:
  - Federal Government
  - Information Technology
  tags_raw:
  - Federal Government
  - Information Technology
  - Federal-Government
  properties:
  - type: Documentation
    url: https://www.councils.gov/cioc
  - type: LegacyWebsite
    url: https://cio.gov
  - type: Statute
    url: https://www.law.cornell.edu/uscode/text/44/3603
common:
- type: RateLimits
  url: rate-limits/chief-information-officers-council-rate-limits.yml
- type: DomainSecurity
  url: security/chief-information-officers-council-domain-security.yml
- type: LLMsTxt
  url: llms/chief-information-officers-council-llms.txt
- type: Lifecycle
  url: lifecycle/chief-information-officers-council-lifecycle.yml
- type: Plans
  url: plans/chief-information-officers-council-plans-pricing.yml
- type: FinOps
  url: finops/chief-information-officers-council-finops.yml
- type: LinkedIn
  url: https://www.linkedin.com/company/federal-cio-council
- type: Website
  url: https://www.councils.gov/cioc
- type: LegacyWebsite
  url: https://cio.gov
- type: ParentAgency
  name: Office of Management and Budget (OMB)
  url: https://www.whitehouse.gov/omb/
- type: Statute
  name: E-Government Act of 2002 (44 USC 3603)
  url: https://www.law.cornell.edu/uscode/text/44/3603
- type: ExecutiveOrder
  name: Executive Order 13011 (1996)
  url: https://www.federalregister.gov/documents/1996/07/19/96-18555/federal-information-technology
- type: GSAOfficeOfGovernmentwidePolicy
  url: https://www.gsa.gov/policy-regulations/policy/information-technology-policy
- type: FedRAMP
  url: https://www.fedramp.gov
- type: TechnologyModernizationFund
  url: https://tmf.cio.gov
- type: USAGov
  url: https://www.usa.gov/agencies/chief-information-officers-council
- type: PrivacyPolicy
  url: https://www.gsa.gov/website-information/website-policies
- type: KnowledgeBase
  name: CIOC Resources Library
  url: https://www.councils.gov/resources/?council=CIOC
- type: Newsroom
  name: CIOC News & Events
  url: https://www.councils.gov/news-events/?council=CIOC
- type: x-CouncilMembers
  name: CIOC Leadership & Members
  url: https://www.councils.gov/cioc/members-leaders/
- type: x-Charter
  name: CIO Council Charter (December 2020)
  url: https://www.councils.gov/docs/CIOC-Charter-Dec-2020.pdf
- type: SourceCode
  name: GSA/councils.gov (Astro site source)
  url: https://github.com/GSA/councils.gov
- name: Committees
  type: Committees
  data:
  - name: Innovation Committee
  - name: Workforce Committee
  - name: Information Security and Identity Management Committee (ISIMC)
  - name: Privacy Committee
  - name: Accessibility Committee
  - name: Shared Services Committee
  - name: Modernization and Migration Committee
- name: Programs
  type: Programs
  data:
  - name: Federal CIO Office (OMB)
  - name: Federal Chief Information Security Officer Council
  - name: Federal Risk and Authorization Management Program (FedRAMP)
  - name: Technology Modernization Fund (TMF)
  - name: U.S. Digital Service
  - name: 18F (GSA)
  - name: National Initiative for Cybersecurity Education (NICE)
- name: Features
  type: Features
  data:
  - name: Senior-Level Interagency Forum
  - name: Federal IT Policy Coordination
  - name: Cybersecurity Standards and Guidance
  - name: IT Modernization Playbooks
  - name: Cloud Adoption (Cloud Smart)
  - name: Federal IT Workforce Development
  - name: Federal Identity, Credential, and Access Management (FICAM)
  - name: Open Government and Data Sharing
- name: UseCases
  type: UseCases
  data:
  - name: Federal IT Modernization
  - name: Cloud Migration and Adoption
  - name: Cybersecurity Posture Improvement
  - name: Federal IT Workforce Development
  - name: Cross-Agency IT Best Practice Sharing
  - name: FedRAMP Authorization Coordination
  - name: Identity, Credential, and Access Management
  - name: Federal Data Strategy Implementation
- name: Standards
  type: Standards
  data:
  - name: E-Government Act of 2002 (44 USC 3603)
  - name: Federal Information Security Modernization Act (FISMA)
  - name: NIST Cybersecurity Framework
  - name: NIST SP 800-53 (Security and Privacy Controls)
  - name: Federal Information Processing Standards (FIPS)
  - name: OMB Circular A-130 (Managing Information as a Strategic Resource)
  - name: Cloud Smart Strategy
  - name: Federal Data Strategy
maintainers:
- FN: Kin Lane
  email: kin@apievangelist.com
x-enrichment:
  date: '2026-09-05'
  status: minimal
  artifacts_added: 4
  pass: local-v3
x-coverage:
  state: none
  reason: not-a-software-company
  detail: The CIO Council is a federal interagency policy forum, not a software publisher — its output is guidance, playbooks
    and a charter served as static Astro pages and PDFs on councils.gov, and a named-path probe of www.councils.gov, councils.gov
    and cio.gov on 2026-09-05 returned 404 (or a 301 to www) for every OpenAPI, GraphQL, MCP, agent-card, llms.txt and apis.json
    location, with a negative-control path confirming none of those hosts echoes paths.
  evidence:
  - url: https://www.councils.gov/cioc/
    status: 200
  - url: https://www.councils.gov/openapi.json
    status: 404
  - url: https://www.councils.gov/.well-known/agent-card.json
    status: 404
  - url: https://www.councils.gov/.well-known/apis.json
    status: 404
  - url: https://cio.gov/
    status: 301
  - url: https://cio.gov/openapi.json
    status: 404
  - url: https://www.councils.gov/.well-known/cioc-negative-control-7f3ab91c.json
    status: 404
  checked: '2026-09-05'
Chief Information Officers Council API — frequently asked questions
Does Chief Information Officers Council have an API?
Yes. APIs.io lists 1 API from Chief Information Officers Council, including Chief Information Officers Council Resources.
Is the Chief Information Officers Council API ready for AI agents?
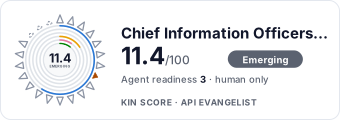
Chief Information Officers Council has a Kin Score of 11.4 out of 100 (emerging) and an Agent Readiness score of 2.5 (human-only), scored by API Evangelist on 2026-11-06.
Calls without X-API-Key need no key. Calls with it need a paid plan — get a key.
Get an API key
Free tier, no form to fill in. Signing in shares your email address with us — we
store it to create your key and to recognise you if you sign in with another
provider. See our Privacy Policy and
Terms.
 Kin Score
How this is scored →
 It updates itself when the score changes. Paste this where you link to your API docs: