Tidelift
Tidelift provides open-source software supply-chain management for enterprises. Its platform combines package intelligence (maintenance, quality, end-of-life, and vulnerability signals) with catalogs of approved dependencies, policy and license standards enforcement, SBOM import/export, and "alignment" of projects against an organization's standards. Tidelift is distinctive for paying the open-source maintainers ("lifters") behind the packages enterprises rely on. The Tidelift External API (OpenAPI 3.0, Bearer API-key auth) exposes catalogs, violations, projects, groups, packages, releases, vulnerabilities, licenses, and reporting. Tidelift was acquired by Sonar in 2025; the API and developer surface remain active.
Tidelift publishes 15 API contracts indexed on the APIs.io network, including Alignments API, Attestations API, Authentication API, and 12 more. Tagged areas include Company, Open Source, Software Supply Chain, Dependency Management, and Application Security.
The Tidelift catalog on APIs.io includes 1 event-driven AsyncAPI specification and 1 Spectral governance ruleset.
Tidelift’s developer surface includes documentation, API reference, getting-started guide, support, pricing, authentication, CLI, and 26 more developer resources.
What this lets a business do 1
Business capabilities this provider's published APIs can perform, derived from its own contracts. Browse all capabilities →
Kin Score
 Kin Score
How this is scored →
scored 2026-11-06 · rubric v0.27.0
 It updates itself when the score changes. Paste this where you link to your API docs:
<a href="https://apis.io/providers/tidelift/"><img src="https://apis.io/badge/tidelift/card.svg" alt="Tidelift on APIs.io — Kin Score by API Evangelist"></a>Other styles, a README pill and a shields.io endpoint are on the badge page.
- MCP Server +12 pts — deployment.mode + probe verdict on the mcp/ manifest, not the pointer; an unprobed slug falls back to authorship
- Idempotency +9 pts — OpenAPI mutating operations declare an idempotency key — a header, a request-body property, or a named de-duplication token whose own description says so (verified); else common[].type matches /idempoten/i (documented)
- A2A Agent Card +8 pts — a2a/
-a2a.yml manifest, graded on conformance.grade against A2A 1.0.0 - Rate-Limit Signaling +7 pts — OpenAPI responses document X-RateLimit-* / RateLimit headers (verified), else a rate_limits artifact or RateLimits link (documented)
- Registration Without a Human +6 pts — a `registration_endpoint` in the served RFC 8414 / OIDC discovery document
- Delegated User Identity +6 pts — a served discovery document listing authorization_code in grant_types_supported (served), else an oauth2 authorizationCode flow or openIdConnect declared in an OpenAPI (documented)
- Access Clarity scores 0.0 — up to +20.0 composite points
- Contract Quality scores 58.0 — up to +10.5 composite points
- Contract Governance scores 18.2 — up to +9.8 composite points
Markets this provider is in provisional
The Kin Score Market layer reads a provider inside its market: its position, and how deep its integrations go. Depth is only comparable within a position. Provisional and unweighted: not part of the Kin Score or agent readiness.
| Market | Position | Depth | Registered MCP server | Declares compatibility |
|---|---|---|---|---|
| Software Supply Chain (SBOM, Signing, Open Source Security) | standard | 44.1 | - | - |
| Cloud Security Attestation and Secure-by-Design | standard | 44.1 | - | - |
Registered MCP server and declares compatibility are report only — not weighted. Undeclared means we found nothing we can read, so there is no number: we never infer integrations.
Standards implemented 1
Standards this provider implements or carries. De facto ones are profiled and measured by the API Commons; formal ones come from the standards directory and are linked by the provider's own tags. The evidence column says how each claim was established — not that it was made.
APIs 15
Individual APIs this provider publishes, each with its own machine-readable definition.
Tidelift Alignments API
The Alignments API from Tidelift — 4 operation(s) for alignments.
Tidelift Attestations API
The Attestations API from Tidelift — 2 operation(s) for attestations.
Tidelift Authentication API
A [Tidelift API key](https://docs.tidelift.com/article/79-api-authentication) is required for all endpoints. If a particular type of API key is required it will be noted on the ...
Tidelift Basic Examples API
* curl ``` curl -H "Accept: application/json" \ -H "Authorization: bearer " \ https://api.tidelift.com/external-api/v1/packages/pypi/urllib3 ``` More detailed examples can be fo
Tidelift Catalog Releases API
The Catalog Releases API from Tidelift — 7 operation(s) for catalog releases.
Tidelift Catalogs API
The Catalogs API from Tidelift — 9 operation(s) for catalogs.
Tidelift CatalogStandards API
The CatalogStandards API from Tidelift — 3 operation(s) for catalogstandards.
Tidelift Groups API
The Groups API from Tidelift — 5 operation(s) for groups.
Tidelift Licenses API
The Licenses API from Tidelift — 5 operation(s) for licenses.
Tidelift Packages API
The Packages API from Tidelift — 6 operation(s) for packages.
Tidelift Projects API
The Projects API from Tidelift — 6 operation(s) for projects.
Tidelift Releases API
The Releases API from Tidelift — 5 operation(s) for releases.
Tidelift Reports API
The Reports API from Tidelift — 3 operation(s) for reports.
Tidelift Users API
The Users API from Tidelift — 1 operation(s) for users.
Tidelift Vulnerabilities API
The Vulnerabilities API from Tidelift — 2 operation(s) for vulnerabilities.
Scroll for all 15
Open Collections 15
Open, tool-agnostic API collections (OpenAPI-derived and Bruno).
Tidelift External Alignments API
OPEN COLLECTIONTidelift External Alignments Attestations API
OPEN COLLECTIONTidelift External Alignments Authentication API
OPEN COLLECTIONTidelift External Alignments Basic Examples API
OPEN COLLECTIONTidelift External Alignments Catalog Releases API
OPEN COLLECTIONTidelift External Alignments Catalogs API
OPEN COLLECTIONTidelift External Alignments CatalogStandards API
OPEN COLLECTIONTidelift External Alignments Groups API
OPEN COLLECTIONTidelift External Alignments Licenses API
OPEN COLLECTIONTidelift External Alignments Packages API
OPEN COLLECTIONTidelift External Alignments Projects API
OPEN COLLECTIONTidelift External Alignments Releases API
OPEN COLLECTIONTidelift External Alignments Reports API
OPEN COLLECTIONTidelift External Alignments Users API
OPEN COLLECTIONTidelift External Alignments Vulnerabilities API
OPEN COLLECTIONScroll for all 15
Arazzo Workflows 1
Multi-step API workflows described with the Arazzo specification.
Tidelift — package vulnerability check
Validate the API key, look up a package and a release, and pull the release's vulnerabilities.
ARAZZOAgent Skills 3
Packaged agent skills for driving this provider's APIs from an AI assistant.
Align a project against a catalog
AGENT SKILLCheck catalog policy violations
AGENT SKILLLook up package and release intelligence
AGENT SKILLEvent Specifications 1
AsyncAPI definitions for this provider's event-driven and streaming APIs.
Tidelift Webhooks
ASYNCAPISpectral Rules 1
Spectral governance rulesets for linting and validating these APIs.
Tidelift API Rules
SPECTRALOpenAPI Overlays 1
Overlays applied on top of this provider's contracts. Each card says who wrote it: a document the provider publishes, or one API Evangelist derived or generated.
Tidelift Subscriber Api Overlay
DERIVEDSecurity Posture 3
Authentication, domain security, vulnerability disclosure, and trust-center signals.
Agentic Access 1
Recommended x-agentic-access execution contracts for AI agents.
Resources
Get Started 2
Portal, sign-up, and the first successful call
Documentation 2
Reference material describing how the API behaves
Agent Surfaces 5
MCP servers, agent skills, and machine-readable catalogs
Design & Contract 7
Pagination, idempotency, versioning, errors, and events
Scroll for all 7
Build 5
SDKs, sample code, and the tooling you integrate with
Access & Security 5
Authentication, authorization, and security posture
Operate 2
Status, limits, changes, and where to get help
Commercial 1
Pricing, plans, and the legal terms of use
Company 1
The organization behind the API
Other 3
Properties that don't map to a standard resource type
Source (apis.yml)
Tidelift API — frequently asked questions
Does Tidelift have an API?
Yes. APIs.io lists 15 APIs from Tidelift, including Tidelift Alignments API, Tidelift Attestations API and Tidelift Authentication API, and 12 more.
Is there an OpenAPI specification for the Tidelift API?
Yes. APIs.io indexes 15 OpenAPI specifications for Tidelift, each linked for download from this page.
How do I authenticate with the Tidelift API?
Tidelift uses bearer-token authentication (http · 1 scheme). The details are profiled on APIs.io as Tidelift Authentication.
Is the Tidelift API ready for AI agents?
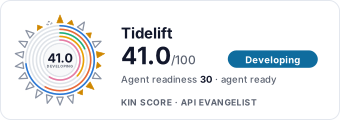
Tidelift has a Kin Score of 41.0 out of 100 (developing) and an Agent Readiness score of 30.1 (agent-ready), scored by API Evangelist on 2026-11-06.
Work with this as data
Every provider here is available over the APIs.io API and to AI agents over MCP.