Zero Trust Network Access
Zero Trust Network Access (ZTNA) is a security framework and product category that grants access to private applications and resources based on identity, device posture, and context, rather than network location. ZTNA replaces the implicit trust of legacy VPNs with explicit per-request verification, creating one-to-one encrypted tunnels between authenticated users and the specific applications they are authorized to use. This topic collects the leading ZTNA vendors, the standards bodies that govern the underlying primitives, and the data schemas used to describe access policies, identities, devices, and resources.
Zero Trust Network Access publishes 12 API contracts indexed on the APIs.io network, including Deployment Groups API, Devices API, DEX Tests API, and 9 more. Tagged areas include Access Control, Cloud Security, Cybersecurity, Identity and Access Management, and Network Access.
The Zero Trust Network Access catalog on APIs.io includes 1 JSON-LD context and 1 Spectral governance ruleset.
Zero Trust Network Access’ developer surface includes documentation, developer portal, code examples, and 23 more developer resources.
What this lets a business do 1
Business capabilities this provider's published APIs can perform, derived from its own contracts. Browse all capabilities →
Kin Score
 Kin Score
How this is scored →
scored 2026-11-13 · rubric v0.28.0
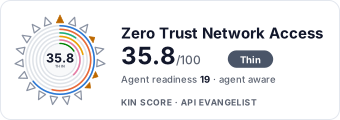 It updates itself when the score changes. Paste this where you link to your API docs:
<a href="https://apis.io/providers/zero-trust-network-access/"><img src="https://apis.io/badge/zero-trust-network-access/card.svg" alt="Zero Trust Network Access on APIs.io — Kin Score by API Evangelist"></a>Other styles, a README pill and a shields.io endpoint are on the badge page.
- MCP Server +12 pts — deployment.mode + probe verdict on the mcp/ manifest, not the pointer; an unprobed slug falls back to authorship Ask about this →
- Agentic Access Contract +10 pts — agentic_access artifact present (x-agentic-access), graded by author Ask about this →
- Idempotency +9 pts — OpenAPI mutating operations declare an idempotency key — a header, a request-body property, or a named de-duplication token whose own description says so (verified); else common[].type matches /idempoten/i (documented) Ask about this →
- Stable Error Semantics +8 pts — OpenAPI $refs a shared error schema across 4xx/5xx responses (verified), else common[].type includes ErrorCatalog / ErrorCodes / DeclineCodes Ask about this →
- A2A Agent Card +8 pts — a2a/
-a2a.yml manifest, graded on conformance.grade against A2A 1.0.0 Ask about this → - Registration Without a Human +6 pts — a `registration_endpoint` in the served RFC 8414 / OIDC discovery document Ask about this →
- Access Clarity scores 12.8 — up to +17.4 composite points Ask about this →
- Developer Ergonomics scores 38.1 — up to +12.4 composite points Ask about this →
- Contract Quality scores 54.1 — up to +11.5 composite points Ask about this →
Standards implemented 3
Standards this provider implements or carries. De facto ones are profiled and measured by the API Commons; formal ones come from the standards directory and are linked by the provider's own tags. The evidence column says how each claim was established — not that it was made.
APIs 12
Individual APIs this provider publishes, each with its own machine-readable definition.
Cloudflare Zero Trust API
Cloudflare Zero Trust (formerly Cloudflare for Teams / Cloudflare Access) provides ZTNA, secure web gateway, browser isolation, CASB, and DLP through a single global edge platfo...
Zscaler Private Access (ZPA) API
Zscaler Private Access is a cloud-native ZTNA service that connects authenticated users to private applications without exposing them to the internet or placing them on the corp...
Netskope Private Access API
Netskope Private Access provides ZTNA as part of the Netskope SASE platform, brokering authenticated access to private applications across cloud and on-premises. The Netskope RE...
Palo Alto Prisma Access (Prisma SASE) API
Palo Alto Networks Prisma Access offers cloud-delivered ZTNA, SWG, and FWaaS as part of the Prisma SASE platform. The Prisma Access REST API exposes operations on remote network...
Tailscale API
Tailscale is a WireGuard-based mesh-VPN ZTNA platform that exposes a REST API for managing devices, ACL policies, tailnet keys, DNS, and audit logs. It implements identity-based...
Twingate API
Twingate is a software-defined ZTNA platform that exposes a GraphQL Admin API for managing remote networks, resources, groups, users, service accounts, and connectors.
Zero Trust Network Access Deployment Groups API
Account-level WARP deployment groups.
Zero Trust Network Access Devices API
WARP devices enrolled in Zero Trust.
Zero Trust Network Access DEX Tests API
Digital Experience Monitoring tests.
Zero Trust Network Access IP Profiles API
WARP device IP profiles.
Zero Trust Network Access Registrations API
Per-user WARP registrations on a device.
Zero Trust Network Access WARP Override API
Global Cloudflare WARP override state.
Scroll for all 12
Open Collections 6
Open, tool-agnostic API collections (OpenAPI-derived and Bruno).
Cloudflare Zero Trust Network Access Deployment Groups API
OPEN COLLECTIONCloudflare Zero Trust Network Access Devices API
OPEN COLLECTIONCloudflare Zero Trust Network Access DEX Tests API
OPEN COLLECTIONCloudflare Zero Trust Network Access IP Profiles API
OPEN COLLECTIONCloudflare Zero Trust Network Access Registrations API
OPEN COLLECTIONCloudflare Zero Trust Network Access WARP Override API
OPEN COLLECTIONZero Trust Network Access API pricing
Not yet checked against Zero Trust Network Access's own pricing page. Compiled by API Evangelist on 2026-05-04; confirm before you rely on a figure. A free plan or tier is listed.
| Plan | Price |
|---|---|
| Free freemium | Free |
| Professional paid | Free |
| Enterprise enterprise | — |
Plan details, limits and sources →
Rate limits
- Free Tier Default: 10 requests per minute
- Free Tier Monthly Quota: 1000 requests per month
- Professional Tier Default: 100 requests per minute
Compiled by API Evangelist, not yet checked against Zero Trust Network Access's documentation. All 5 limits →
Pricing Plans 1
Published pricing tiers and plan structures.
Rate Limits 1
Documented rate limits and quota policies.
Zero Trust Network Access Rate Limits
RATE LIMITSFinOps 1
Cost, billing, and metering signals for API financial operations.
Features 8
Notable capabilities this provider offers.
Identity-Centric Access
Access decisions are based on user and workload identity rather than network location.
Application-Level Tunnels
One-to-one encrypted connections between authenticated users and specific applications.
Device Posture Checks
Continuous evaluation of device health, OS patch level, EDR status, and certificate state.
Context-Aware Policy
Policies factor in time, location, risk score, and behavior in addition to identity.
Application Cloaking
Private applications are dark to the public internet and not advertised by IP or DNS.
SSO and MFA Integration
Native integration with SAML, OIDC, and modern MFA providers.
Microsegmentation
Lateral movement is prevented by issuing scoped, per-application access.
Continuous Authorization
Sessions are reauthenticated and reauthorized as conditions change.
Scroll for all 8
Semantic Vocabularies 1
JSON-LD contexts and semantic vocabularies used across these APIs.
Spectral Rules 1
Spectral governance rulesets for linting and validating these APIs. Counts are the severity each rule declares, not results of running them.
JSON Schema 3
Standalone JSON Schema definitions for this provider's data models.
ZTNA Protected Application
JSON SCHEMAZTNA Device Posture Profile
JSON SCHEMAZTNA Access Policy
JSON SCHEMAJSON Structure 1
JSON Structure definitions describing this provider's data shapes.
Zero Trust Network Access Policy Structure
JSON STRUCTUREExamples 2
Example request and response payloads for these APIs.
Security Posture 2
Authentication, domain security, vulnerability disclosure, and trust-center signals.
Zero Trust Network Access Vulnerability Disclosure
Hackerone · security.txt · contact published
SECURITYUse Cases 6
What developers build with this provider.
VPN Replacement
Replacing legacy site-to-site and remote-access VPNs with identity-aware brokered access.
Third-Party Contractor Access
Granting time-bounded, application-scoped access to vendors and contractors.
M&A Network Integration
Enabling acquired companies to reach internal applications without merging networks.
BYOD Access
Allowing personal and unmanaged devices to access selected applications under posture rules.
Privileged Access
Brokering jump-host and bastion access to sensitive infrastructure.
Multi-Cloud Application Access
Providing consistent ZTNA across applications hosted in AWS, Azure, GCP, and on-premises.
Resources
Get Started 6
Portal, sign-up, and the first successful call
Documentation 6
Reference material describing how the API behaves
Design & Contract 2
Pagination, idempotency, versioning, errors, and events
Build 4
SDKs, sample code, and the tooling you integrate with
Access & Security 3
Authentication, authorization, and security posture
Operate 1
Status, limits, changes, and where to get help
Commercial 2
Pricing, plans, and the legal terms of use
Other 2
Properties that don't map to a standard resource type
Source (apis.yml)
Zero Trust Network Access API — frequently asked questions
Does Zero Trust Network Access have an API?
Yes. APIs.io lists 12 APIs from Zero Trust Network Access, including Cloudflare Zero Trust API, Zscaler Private Access (ZPA) API and Netskope Private Access API, and 9 more.
Is there an OpenAPI specification for the Zero Trust Network Access API?
Yes. APIs.io indexes 6 OpenAPI specifications for Zero Trust Network Access, each linked for download from this page.
How do I authenticate with the Zero Trust Network Access API?
Zero Trust Network Access uses bearer-token authentication.
How much does the Zero Trust Network Access API cost?
APIs.io lists 3 pricing plans for Zero Trust Network Access, with each plan's price, limits and inclusions under Pricing on this page.
Is the Zero Trust Network Access API ready for AI agents?
Zero Trust Network Access has a Kin Score of 35.2 out of 100 (thin) and an Agent Readiness score of 19.1 (agent-aware), scored by API Evangelist on 2026-11-13.
Work with this as data
Every provider here is available over the APIs.io API and to AI agents over MCP.