Splunk is a data platform that enables organizations to search, monitor, analyze, and visualize massive streams of machine-generated data across security, observability, and AI use cases. It offers solutions for security information and event management (SIEM), infrastructure monitoring, application performance monitoring, and AI-driven analytics, helping enterprises turn data into actionable insights and operational intelligence.
Splunk publishes 14 API contracts indexed on the APIs.io network, including Data Inputs API, Index API, Search API, and 11 more. Tagged areas include Analytics, Data Analysis, Logging, Machine Data, and Monitoring.
The Splunk catalog on APIs.io includes 2 JSON-LD contexts and 3 Spectral governance rulesets.
Splunk’s developer surface includes signup flow, API reference, authentication, engineering blog, support, documentation, getting-started guide, and 76 more developer resources.
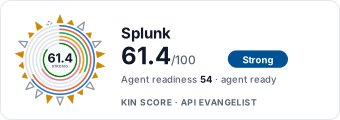
61.4/100strong▬ flatAgent54/100agent readyFront door AI6/6
dominant
Heartbeat88/100
alive
open core · Apache-2.0
Full breakdown ↓
scored 2026-11-06 · rubric v0.27.0 · Show this score on your site →
Regulatory Posture applies to this provider. Its tags matched the
Horizontal (data, software, accessibility, platform) regime, so
Regulatory Posture carries 15 points of the composite.
If this regime is wrong for your business, say so on your
provider repo — the
applicability map is public and we will correct it.
Open Source Surface applies to this provider. This product is open source and we
read its repository directly, so Open Source Surface carries
10 points of the composite. It is scored from what the repository actually
publishes — a security policy, a contribution guide, a release history, a code of conduct — read live from the
provider rather than inferred from our own catalog pointers.
This facet adds; nothing was taken away to make room for it. An open-source project is not excused from
the commercial facets, because exemption would strip it of the points it does earn.
If we have the wrong repository, or this product is not open source, say so on your
provider repo and we
will drop the facet rather than have you publish against it.
Create-or-Update Ergonomics applies to this provider. This API accepts writes, so it
carries 10 points of the composite. It is scored from the published contracts
themselves: whether a caller can create-or-update in one call, whether the write accepts a key the caller already
holds, and whether the response says which branch ran. Without that, every write needs a search-and-branch in
front of it, and the first time that check is skipped a duplicate record is created.
Scored against the observed mean rather than raw — a provider at the catalog average is unchanged by this facet,
not penalised by it.
The six quality facets above are damped to 65 points between them,
because both conditional facets apply and carry
35 points together. That is why each facet's contribution is shown against a damped
maximum: raising a quality facet moves the composite by 65% of its nominal
weight, not 100%. The full arithmetic is at apis.io/rating/.
Show this score on your site.
It updates itself when the score changes. Paste this where you link to your API docs:
<a href="https://apis.io/providers/splunk/"><img src="https://apis.io/badge/splunk/card.svg" alt="Splunk on APIs.io — Kin Score by API Evangelist"></a>
Other styles, a README pill and a shields.io endpoint are on the badge page.
Raise your score.
Agent readiness — checks not met, largest first (exact, from this profile):
MCP Server+12 pts — deployment.mode + probe verdict on the mcp/ manifest, not the pointer; an unprobed slug falls back to authorship
Idempotency+9 pts — OpenAPI mutating operations declare an idempotency key — a header, a request-body property, or a named de-duplication token whose own description says so (verified); else common[].type matches /idempoten/i (documented)
Typed Event Surface+6 pts — AsyncAPI document, OR webhooks/callbacks objects in the as-published OpenAPI, OR common[].type includes Webhooks
Documented Reversibility+6 pts — a reversal operation in the contract, graded up when a window is documented too
Agentic Commerce Well-Known Document+5 pts — a parsing /.well-known/ucp.json or acp.json declaring a version and at least one service, OR (0.27) a live x402 payment challenge from _data/x402-adoption.json — `self` when its endpoints are on the provider's own domain, `platform` when they are on a vendor's
The Kin Score Market layer reads a provider inside its market:
its position, and how deep its integrations go. Depth is only comparable within a position. Provisional and unweighted:
not part of the Kin Score or agent readiness.
Registered MCP server and declares compatibility are report only — not weighted.
Undeclared means we found nothing we can read, so there is no number: we never infer integrations.
Standards this provider implements or carries. De facto ones are profiled and measured by the API Commons; formal ones come from the standards directory and are linked by the provider's own tags. The evidence column says how each claim was established — not that it was made.
The Splunk Cloud Platform REST API provides a subset of the Splunk Enterprise REST API endpoints for managing and interacting with your Splunk Cloud Platform deployment. Access ...
The Admin Config Service (ACS) is a cloud-native API that provides programmatic self-service administration capabilities for Splunk Cloud Platform. Administrators can use the AC...
The Splunk Observability Cloud API provides REST endpoints for sending and managing metrics, traces, and events. It supports infrastructure monitoring, application performance m...
The Splunk SOAR REST API enables programmatic creation, updating, and management of security automation objects including containers, assets, playbooks, indicators, lists, and a...
The Splunk Enterprise Security API provides REST endpoints for accessing and modifying findings, investigations, risk scores, assets, and identities in Splunk Enterprise Securit...
The Splunk IT Service Intelligence (ITSI) REST API allows bulk creation and updating of ITOA interface objects such as entities, services, and KPI base searches. ITSI is a monit...
The Splunk HTTP Event Collector (HEC) is a high-performance REST API data input that accepts JSON or raw text data sent over HTTP or HTTPS. It uses token-based authentication an...
The Splunk Intelligence Management (formerly ThreatStream) API provides REST v2.0 endpoints for managing threat intelligence data including indicators, observables, and intellig...
The Splunk SOAR Playbook Automation API provides Python APIs for developing playbooks and automation within Splunk SOAR. It includes container, playbook, data access, vault, net...
The Splunk AppInspect API validates Splunk apps and add-ons against Splunk best practices and requirements for publishing to Splunkbase or installing on Splunk Cloud Platform. I...
Endpoints for configuring and managing data inputs including monitors, TCP/UDP inputs, scripted inputs, and HTTP Event Collector (HEC) tokens. Data inputs define how Splunk inge...
Endpoints for managing Splunk indexes, which store and organize ingested data. Indexes can be created, modified, listed, and configured for retention and storage policies.
Endpoints for creating, managing, and retrieving search jobs and their results. Splunk search processing language (SPL) queries are submitted as search jobs that run asynchronou...
aid: splunk
name: Splunk
description: Splunk is a data platform that enables organizations to search, monitor, analyze, and visualize massive streams
  of machine-generated data across security, observability, and AI use cases. It offers solutions for security information
  and event management (SIEM), infrastructure monitoring, application performance monitoring, and AI-driven analytics, helping
  enterprises turn data into actionable insights and operational intelligence.
deliveryModel:
  model: open-core
  license: Apache-2.0
  open_source: true
  commercial: true
  callable_host: false
  label: Open core · an OSS project plus a commercial hosted product
  confidence: high
  source:
  - license
  - openapi
  - pricing
  generated: '2026-08-28'
  method: derived
accessModel:
  pricing: paid
  onboarding: unknown
  trial: false
  try_now: false
  public: false
  label: Paid
  confidence: medium
  probe_state: unreadable
  source:
  - plans
  - authentication
  - security
  generated: '2026-11-06'
  method: derived
image: https://www.splunk.com/content/dam/splunk2/images/icons/favicons/favicon.ico
url: https://raw.githubusercontent.com/api-evangelist/splunk/refs/heads/main/apis.yml
created: '2025-01-08'
modified: '2026-08-19'
specificationVersion: '0.23'
type: Index
access: 3rd-Party
position: Consuming
tags:
- Analytics
- Data Analysis
- Logging
- Machine Data
- Monitoring
- Observability
- Platform
- Security
- SIEM
maintainers:
- FN: Kin Lane
  email: kin@apievangelist.com
- name: Splunk Inc.
  email: devinfo@splunk.com
  url: https://www.splunk.com
common:
- type: SecurityTxt
  url: well-known/splunk-apis-security.txt
- type: IntegrationEdges
  url: integrations/splunk-integration-edges.yml
- type: FinOps
  url: finops/splunk-finops.yml
- type: RateLimits
  url: rate-limits/splunk-rate-limits.yml
- type: Plans
  url: plans/splunk-plans-pricing.yml
- type: Spectral
  url: rules/splunk-spectral-rules.yml
- type: Spectral
  url: rules/splunk-rules.yml
- type: Spectral
  url: rules/splunk-jsonschema-spectral-rules.yml
- type: JSONLD
  url: json-ld/splunk-enterprise-rest-context.jsonld
- type: Vocabulary
  url: vocabulary/splunk-vocabulary.yml
- type: AgentSkill
  url: skills/_index.yml
- type: DataModel
  url: data-model/splunk-data-model.yml
- type: Compliance
  url: https://customertrust.splunk.com/
- type: ErrorCatalog
  url: errors/splunk-problem-types.yml
- type: Conformance
  url: conformance/splunk-conformance.yml
- type: LLMsTxt
  url: llms/splunk-llms.txt
- type: AgentCard
  url: a2a/splunk-a2a.yml
- type: SecurityTxt
  url: well-known/splunk-security.txt
- type: SecurityTxt
  url: well-known/splunk-advisory-security.txt
- type: WellKnown
  url: well-known/splunk-well-known.yml
- type: Hosts
  url: hosts/splunk-hosts.yml
- type: Vendors
  url: vendors/splunk-vendors.yml
- type: SignUp
  url: http://idp.login.splunk.com/signin/register?redirecturl=https://docs.splunk.com/Documentation?action=pdfbook&product=SARIAddOn&title=Documentation%253ASARIAddOn%253AInstall%253AGetStarted%253A1.0.0&topic=1&version=1.1.2
- type: Newsroom
  url: https://www.splunk.com/en_us/newsroom/media-kit.html
- type: APIReference
  url: https://agent-observability-docs.splunk.com/llms.txt
- type: Website
  url: https://www.splunk.com/
- type: IssueTracker
  url: https://github.com/signalfx/splunk-otel-collector/issues
- type: Releases
  url: https://github.com/signalfx/splunk-otel-collector/releases
- type: CodeOfConduct
  url: https://github.com/signalfx/splunk-otel-collector/blob/main/CODE_OF_CONDUCT.md
- type: ContributionGuide
  url: https://github.com/signalfx/splunk-otel-collector/blob/main/CONTRIBUTING.md
- type: ParentCompany
  url: https://apis.io/providers/cisco/
  name: Cisco
  x-relationship: acquisition
  x-generated-by: cisco-family:2026-08-19
  x-acquired: 2024
- type: License
  name: Apache-2.0
  url: https://github.com/signalfx/splunk-otel-collector/blob/main/LICENSE
- type: AgenticAccess
  url: agentic-access/splunk-agentic-access.yml
- type: TrustCenter
  url: security/splunk-trust-center.yml
- type: VulnerabilityDisclosure
  url: security/splunk-vulnerability-disclosure.yml
- type: DomainSecurity
  url: security/splunk-domain-security.yml
- type: Authentication
  url: authentication/splunk-authentication.yml
- type: PostmanWorkspace
  url: https://www.postman.com/kinlaneapi/splunk/overview
- type: Arazzo
  url: arazzo/splunk-control-and-cleanup-search-workflow.yml
  name: Splunk Finalize, Read, and Clean Up a Search Job
- type: Arazzo
  url: arazzo/splunk-hec-ingest-and-acknowledge-workflow.yml
  name: Splunk HEC Ingest an Event and Confirm Indexing
- type: Arazzo
  url: arazzo/splunk-provision-index-and-monitor-workflow.yml
  name: Splunk Provision an Index and Attach a Monitor Input
- type: Arazzo
  url: arazzo/splunk-raw-ingest-and-search-workflow.yml
  name: Splunk Ingest Raw Data then Search for It
- type: Arazzo
  url: arazzo/splunk-run-search-job-workflow.yml
  name: Splunk Run a Search Job and Retrieve Results
- type: Arazzo
  url: arazzo/splunk-search-events-workflow.yml
  name: Splunk Search and Retrieve Raw Events
- type: DeveloperPortal
  url: https://dev.splunk.com/
- type: Blog
  url: https://www.splunk.com/en_us/blog
- type: Support
  url: https://www.splunk.com/en_us/support-and-services.html
- type: Documentation
  url: https://community.splunk.com/
  title: Community
- type: GitHubOrganization
  url: https://github.com/splunk
- type: Documentation
  url: https://docs.splunk.com/Documentation
- type: Documentation
  url: https://help.splunk.com/en
  title: Help Center
- type: GettingStarted
  url: https://dev.splunk.com/enterprise/docs
- type: Documentation
  url: https://dev.splunk.com/enterprise/docs/devtools/
  title: Developer Tools
- type: Documentation
  url: https://dev.splunk.com/enterprise/downloads
  title: Downloads
- type: Marketplace
  url: https://splunkbase.splunk.com/
- type: Pricing
  url: https://www.splunk.com/en_us/products/pricing.html
- type: Signup
  url: https://www.splunk.com/en_us/download/splunk-cloud.html
- type: Signup
  url: https://dev.splunk.com/enterprise/dev_license/
  title: Developer License
- type: TermsOfService
  url: https://www.splunk.com/en_us/legal/terms/terms-of-use.html
- type: TermsOfService
  url: https://www.splunk.com/en_us/legal/splunk-general-terms.html
  title: General Terms
- type: ChangeLog
  url: https://help.splunk.com/en/splunk-enterprise/release-notes-and-updates
- type: Authentication
  url: https://docs.splunk.com/Documentation/Splunk/latest/RESTUM/RESTusing
- type: SDKs
  url: https://github.com/splunk/splunk-sdk-python
  title: Python SDK
- type: SDKs
  url: https://github.com/splunk/splunk-sdk-java
  title: Java SDK
- type: SDKs
  url: https://github.com/splunk/splunk-sdk-javascript
  title: JavaScript SDK
- type: SDKs
  url: https://github.com/splunk/splunk-sdk-csharp-pcl
  title: C# SDK
- type: SDKs
  url: https://dev.splunk.com/enterprise/docs/devtools/csharp
  title: C# SDK Documentation
- type: ChangeLog
  url: https://dev.splunk.com/enterprise/docs/whatsnew/
  title: What's New
- type: ChangeLog
  url: https://dev.splunk.com/enterprise/docs/relnotes
  title: Release Notes
- type: Documentation
  url: https://dev.splunk.com/enterprise/docs/devtools/customrestendpoints
  title: Custom REST Endpoints
- type: Authentication
  url: https://docs.splunk.com/Documentation/Splunk/latest/Security/UseAuthTokens
  title: Auth Tokens
- type: PrivacyPolicy
  url: https://www.splunk.com/en_us/legal/privacy-policy.html
- type: Security
  url: https://www.splunk.com/en_us/about-splunk/splunk-data-security-and-privacy.html
- type: GitHubRepository
  url: https://github.com/signalfx/splunk-otel-collector
  title: OpenTelemetry Collector
- type: LinkedIn
  url: https://www.linkedin.com/company/splunk
- type: X
  url: https://twitter.com/splunk
- type: SpectralRules
  url: rules/splunk-spectral-rules.yml
- type: Features
  url: https://www.splunk.com/en_us/products.html
  data:
  - 'Splunk (now Cisco): hundreds of services across Observability + SIEM'
  - 'Detailed pricing: see https://www.splunk.com/en_us/products/pricing.html'
  - 'Service: Splunk Enterprise / Cloud (data ingest)'
  - 'Service: Splunk Observability Cloud (APM, Logs, RUM, Synthetics)'
  - 'Service: Splunk SOAR'
  - 'Service: Splunk Enterprise Security (SIEM)'
  - 'Service: Splunk ITSI'
  - 'Service: Splunk SOC Platform'
  sources:
  - https://www.splunk.com/en_us/products/pricing.html
  - https://focus.finops.org/
  updated: '2026-05-04'
- type: UseCases
  url: https://www.splunk.com/en_us/solutions.html
  data:
  - name: Security Information and Event Management
    description: Centralize security event data for real-time threat detection, investigation, and compliance reporting.
  - name: IT Operations Monitoring
    description: Monitor infrastructure health, application performance, and service availability across hybrid environments.
  - name: Log Management
    description: Collect, index, and analyze log data from servers, applications, and network devices for troubleshooting.
  - name: Incident Response Automation
    description: Automate security incident triage, enrichment, and response using SOAR playbooks and integrations.
  - name: Application Performance Monitoring
    description: Trace application requests end-to-end to identify bottlenecks and optimize performance.
  - name: Compliance and Audit
    description: Generate compliance reports and audit trails from indexed data to meet regulatory requirements.
- type: Integrations
  url: https://splunkbase.splunk.com/
  data:
  - name: AWS
    description: Ingest and analyze AWS CloudTrail, CloudWatch, VPC Flow Logs, and other AWS service data.
  - name: Azure
    description: Collect and analyze Azure activity logs, metrics, and diagnostic data.
  - name: Google Cloud
    description: Ingest Google Cloud audit logs, metrics, and Pub/Sub messages for cloud monitoring.
  - name: Kubernetes
    description: Monitor Kubernetes clusters with metrics, logs, and events from containers and orchestration.
  - name: ServiceNow
    description: Integrate Splunk alerts and incidents with ServiceNow ITSM for ticketing and workflow automation.
  - name: PagerDuty
    description: Trigger PagerDuty incidents from Splunk alerts for on-call notification and escalation.
  - name: Cisco
    description: Collect and analyze Cisco network device logs, firewall events, and security telemetry.
  - name: CrowdStrike
    description: Ingest CrowdStrike Falcon endpoint detection data for correlated threat analysis.
- name: MCP Server
  url: https://github.com/splunk/splunk-mcp-server2
  type: MCPServer
- type: Subsidiary
  url: https://apis.io/providers/signalfx/
  name: SignalFx
  x-relationship: acquisition
  x-generated-by: cisco-family:2026-08-19
  x-acquired: 2019
- type: Subsidiary
  url: https://apis.io/providers/splunk-observability/
  name: Splunk Observability Cloud
  x-relationship: product
  x-generated-by: cisco-family:2026-08-19
- type: Subsidiary
  url: https://apis.io/providers/splunk-soar/
  name: Splunk SOAR
  x-relationship: acquisition
  x-generated-by: cisco-family:2026-08-19
  x-acquired: 2018
- type: Subsidiary
  url: https://apis.io/providers/victorops/
  name: Splunk On-Call (VictorOps)
  x-relationship: acquisition
  x-generated-by: cisco-family:2026-08-19
  x-acquired: 2018
- type: CapabilityMap
  url: capabilities/splunk-capability-edges.yml
  name: Splunk Business Capability Map
apis:
- aid: splunk:splunk
  name: Splunk
  description: API monitoring checks to see if API-connected resources are available, working properly and responding to calls.
  humanURL: https://www.splunk.com/en_us/blog/learn/api-monitoring.html
  tags: []
  properties:
  - type: Documentation
    url: https://www.splunk.com/en_us/blog/learn/api-monitoring.html
- aid: splunk:splunk-cloud-platform-rest-api
  name: Splunk Cloud Platform REST API
  description: The Splunk Cloud Platform REST API provides a subset of the Splunk Enterprise REST API endpoints for managing
    and interacting with your Splunk Cloud Platform deployment. Access requires port 8089 to be opened by Splunk Support.
  humanURL: https://help.splunk.com/en/splunk-cloud-platform/rest-api-reference
  tags:
  - Cloud
  - Data
  - Management
  - REST
  - Search
  properties:
  - type: Documentation
    url: https://help.splunk.com/en/splunk-cloud-platform/rest-api-reference
  - type: GettingStarted
    url: https://docs.splunk.com/Documentation/SplunkCloud/latest/RESTTUT/RESTandCloud
  - type: APIReference
    url: https://docs.splunk.com/Documentation/SplunkCloud/latest/RESTREF/RESTprolog
- aid: splunk:splunk-cloud-admin-config-service-api
  name: Splunk Cloud Admin Config Service (ACS) API
  description: The Admin Config Service (ACS) is a cloud-native API that provides programmatic self-service administration
    capabilities for Splunk Cloud Platform. Administrators can use the ACS API to manage indexes, IP allow lists, HEC tokens,
    users, and roles without assistance from Splunk Support. ACS provides an OpenAPI 3.0 specification.
  humanURL: https://docs.splunk.com/Documentation/SplunkCloud/latest/Config/ACSIntro
  tags:
  - Administration
  - Cloud
  - Configuration
  - Management
  properties:
  - type: Documentation
    url: https://docs.splunk.com/Documentation/SplunkCloud/latest/Config/ACSIntro
  - type: GettingStarted
    url: https://docs.splunk.com/Documentation/SplunkCloud/latest/Config/ACSusage
  - type: APIReference
    url: https://docs.splunk.com/Documentation/SplunkCloud/latest/Config/ACSREF
- aid: splunk:splunk-observability-cloud-api
  name: Splunk Observability Cloud API
  description: The Splunk Observability Cloud API provides REST endpoints for sending and managing metrics, traces, and events.
    It supports infrastructure monitoring, application performance monitoring (APM), real user monitoring, and synthetic monitoring
    use cases.
  humanURL: https://dev.splunk.com/observability/
  tags:
  - APM
  - Metrics
  - Monitoring
  - Observability
  - Traces
  properties:
  - type: Documentation
    url: https://dev.splunk.com/observability/docs
  - type: APIReference
    url: https://dev.splunk.com/observability/reference
  - type: APIReference
    url: https://dev.splunk.com/observability/docs/apibasics/api_list/
    title: API List
  - type: Authentication
    url: https://dev.splunk.com/observability/docs/apibasics/authentication_basics/
  - type: Documentation
    url: https://dev.splunk.com/observability/docs/datamodel/ingest/
    title: Data Ingest
  - type: APIReference
    url: https://dev.splunk.com/observability/reference/api/ingest_data/latest
    title: Ingest Data Reference
  - type: Documentation
    url: https://dev.splunk.com/observability/docs/administration/authtokens
    title: Auth Tokens
- aid: splunk:splunk-soar-rest-api
  name: Splunk SOAR REST API
  description: The Splunk SOAR REST API enables programmatic creation, updating, and management of security automation objects
    including containers, assets, playbooks, indicators, lists, and audit records. REST API requests must be performed over
    HTTPS with token-based or basic authentication.
  humanURL: https://docs.splunk.com/Documentation/SOAR/current/PlatformAPI/Using
  tags:
  - Automation
  - Orchestration
  - Playbooks
  - Security
  - SOAR
  properties:
  - type: Documentation
    url: https://docs.splunk.com/Documentation/SOAR/current/PlatformAPI/Using
  - type: Documentation
    url: https://help.splunk.com/en/splunk-soar/soar-cloud/rest-api-reference/using-the-splunk-soar-rest-api/using-the-rest-api-reference-for-splunk-soar-cloud
    title: SOAR Cloud REST API Reference
  - type: APIReference
    url: https://help.splunk.com/en/splunk-soar/soar-cloud/rest-api-reference/container-endpoints/rest-containers
    title: Container Endpoints
  - type: APIReference
    url: https://help.splunk.com/en/splunk-soar/soar-cloud/rest-api-reference/artifact-endpoints/rest-artifact
    title: Artifact Endpoints
  - type: Documentation
    url: https://help.splunk.com/en/splunk-soar/soar-on-premises/rest-api-reference/7.1.0/using-the-splunk-soar-rest-api/using-the-rest-api-reference-for-splunk-soar-on-premises
    title: SOAR On-Premises REST API Reference
- aid: splunk:splunk-enterprise-security-api
  name: Splunk Enterprise Security API
  description: The Splunk Enterprise Security API provides REST endpoints for accessing and modifying findings, investigations,
    risk scores, assets, and identities in Splunk Enterprise Security. It includes an OpenAPI specification for download.
  humanURL: https://help.splunk.com/en/splunk-enterprise-security-8/api-reference
  tags:
  - Enterprise Security
  - Findings
  - Investigations
  - Security
  - SIEM
  properties:
  - type: Documentation
    url: https://help.splunk.com/en/splunk-enterprise-security-8/api-reference
  - type: APIReference
    url: https://help.splunk.com/en/splunk-enterprise-security-8/rest-api-reference
  - type: GettingStarted
    url: https://dev.splunk.com/enterprise/docs/devtools/enterprisesecurity
  - type: APIReference
    url: https://help.splunk.com/en/splunk-enterprise-security-8/rest-api-reference/8.0/threat-intelligence-endpoints/threat-intelligence-api-reference
    title: Threat Intelligence API
  - type: Documentation
    url: https://dev.splunk.com/enterprise/docs/devtools/enterprisesecurity/threatintelligenceframework/
    title: Threat Intelligence Framework
- aid: splunk:splunk-itsi-rest-api
  name: Splunk IT Service Intelligence (ITSI) REST API
  description: The Splunk IT Service Intelligence (ITSI) REST API allows bulk creation and updating of ITOA interface objects
    such as entities, services, and KPI base searches. ITSI is a monitoring and analytics solution powered by artificial intelligence
    for IT Operations (AIOps).
  humanURL: https://help.splunk.com/en/splunk-it-service-intelligence/splunk-it-service-intelligence/leverage-rest-apis/4.19/itsi-rest-api-schema/itsi-rest-api-schema
  tags:
  - AIOps
  - IT Service Intelligence
  - ITSI
  - Monitoring
  properties:
  - type: Documentation
    url: https://help.splunk.com/en/splunk-it-service-intelligence/splunk-it-service-intelligence/leverage-rest-apis/4.19/itsi-rest-api-schema/itsi-rest-api-schema
  - type: APIReference
    url: https://help.splunk.com/en/splunk-it-service-intelligence/splunk-it-service-intelligence/leverage-rest-apis/4.18/itsi-rest-api-reference/itsi-rest-api-reference
- aid: splunk:splunk-http-event-collector-api
  name: Splunk HTTP Event Collector (HEC) API
  description: The Splunk HTTP Event Collector (HEC) is a high-performance REST API data input that accepts JSON or raw text
    data sent over HTTP or HTTPS. It uses token-based authentication and provides endpoints for sending events (/services/collector/event),
    raw data (/services/collector/raw), and checking indexing status (/services/collector/ack).
  humanURL: https://docs.splunk.com/Documentation/Splunk/latest/Data/UsetheHTTPEventCollector
  tags:
  - Data Ingestion
  - Event
  - HEC
  - Logging
  - REST
  tags_raw:
  - Data Ingestion
  - Events
  - HEC
  - Logging
  - REST
  properties:
  - type: Documentation
    url: https://docs.splunk.com/Documentation/Splunk/latest/Data/UsetheHTTPEventCollector
  - type: APIReference
    url: https://docs.splunk.com/Documentation/SplunkCloud/latest/Data/HECRESTendpoints
  - type: Documentation
    url: https://docs.splunk.com/Documentation/SplunkCloud/latest/Data/FormateventsforHTTPEventCollector
    title: Event Format
  - type: Documentation
    url: https://docs.splunk.com/Documentation/SplunkCloud/latest/Data/HECExamples
    title: HEC Examples
  - type: GettingStarted
    url: https://dev.splunk.com/view/event-collector/SP-CAAAE6M
- aid: splunk:splunk-intelligence-management-api
  name: Splunk Intelligence Management API
  description: The Splunk Intelligence Management (formerly ThreatStream) API provides REST v2.0 endpoints for managing threat
    intelligence data including indicators, observables, and intelligence sources. It supports STIX and TAXII formats for
    sharing cyber threat intelligence over HTTPS.
  humanURL: https://docs.splunk.com/Documentation/SIM/current/Develop/RESTv20
  tags:
  - Indicators
  - Security
  - STIX
  - TAXII
  - Threat Intelligence
  properties:
  - type: Documentation
    url: https://docs.splunk.com/Documentation/SIM/current/Develop/RESTv20
  - type: Documentation
    url: https://docs.splunk.com/Documentation/SIM/current/User/Threatintelsources
    title: Threat Intel Sources
  - type: Documentation
    url: https://docs.splunk.com/Documentation/SIM/current/Intro/UsagePolicy
    title: Usage Policy
- aid: splunk:splunk-soar-playbook-automation-api
  name: Splunk SOAR Playbook Automation API
  description: The Splunk SOAR Playbook Automation API provides Python APIs for developing playbooks and automation within
    Splunk SOAR. It includes container, playbook, data access, vault, network, and session automation APIs for building detailed
    security orchestration workflows.
  humanURL: https://help.splunk.com/en/splunk-soar/soar-cloud/develop-apps/python-playbook-api-reference/overview/about-splunk-soar-cloud-playbook-automation-apis
  tags:
  - Automation
  - Orchestration
  - Playbooks
  - Security
  - SOAR
  properties:
  - type: Documentation
    url: https://help.splunk.com/en/splunk-soar/soar-cloud/develop-apps/python-playbook-api-reference/overview/about-splunk-soar-cloud-playbook-automation-apis
  - type: APIReference
    url: https://help.splunk.com/en/splunk-soar/soar-cloud/develop-apps/python-playbook-api-reference/automation-api/container-automation-api
    title: Container Automation
  - type: APIReference
    url: https://help.splunk.com/en/splunk-soar/soar-cloud/develop-apps/python-playbook-api-reference/automation-api/playbook-automation-api
    title: Playbook Automation
  - type: APIReference
    url: https://help.splunk.com/en/splunk-soar/soar-cloud/develop-apps/python-playbook-api-reference/automation-api/data-access-automation-api
    title: Data Access Automation
  - type: APIReference
    url: https://help.splunk.com/en/splunk-soar/soar-cloud/develop-apps/python-playbook-api-reference/automation-api/vault-automation-api
    title: Vault Automation
- aid: splunk:splunk-appinspect-api
  name: Splunk AppInspect API
  description: The Splunk AppInspect API validates Splunk apps and add-ons against Splunk best practices and requirements
    for publishing to Splunkbase or installing on Splunk Cloud Platform. It provides automated app vetting through a REST
    API.
  humanURL: https://dev.splunk.com/enterprise/docs/relnotes/relnotes-appinspectapi/whatsnew
  tags:
  - Application
  - Cloud
  - Splunkbase
  - Validation
  tags_raw:
  - Apps
  - Cloud
  - Splunkbase
  - Validation
  properties:
  - type: ChangeLog
    url: https://dev.splunk.com/enterprise/docs/relnotes/relnotes-appinspectapi/whatsnew
  - type: APIReference
    url: https://dev.splunk.com/enterprise/reference
- aid: splunk:splunk-data-inputs-api
  name: Splunk Data Inputs API
  description: Endpoints for configuring and managing data inputs including monitors, TCP/UDP inputs, scripted inputs, and
    HTTP Event Collector (HEC) tokens. Data inputs define how Splunk ingests data.
  humanURL: https://www.splunk.com/en_us/blog/learn/api-monitoring.html
  tags:
  - Data Inputs
  properties:
  - type: OpenAPI
    url: openapi/splunk-data-inputs-api-openapi.yml
  - type: Documentation
    url: https://docs.splunk.com/Documentation/Splunk/latest/RESTREF/RESTprolog
  - type: GettingStarted
    url: https://docs.splunk.com/Documentation/Splunk/latest/RESTUM/RESTusing
  - type: APIReference
    url: https://dev.splunk.com/enterprise/reference
  - type: APIReference
    url: https://help.splunk.com/en/splunk-enterprise/leverage-rest-apis/rest-api-reference/10.2/introduction/endpoints-reference-list
  - type: Authentication
    url: https://docs.splunk.com/Documentation/Splunk/latest/RESTUM/RESTusing
  - type: Documentation
    url: https://docs.splunk.com/Documentation/Splunk/latest/RESTREF/RESTsearch
  - type: JSONSchema
    url: json-schema/splunk-search-job-schema.json
  - type: JSONSchema
    url: json-schema/splunk-event-schema.json
  - type: JSONLD
    url: json-ld/splunk-context.jsonld
- aid: splunk:splunk-index-api
  name: Splunk Index API
  description: Endpoints for managing Splunk indexes, which store and organize ingested data. Indexes can be created, modified,
    listed, and configured for retention and storage policies.
  humanURL: https://www.splunk.com/en_us/blog/learn/api-monitoring.html
  tags:
  - Index
  properties:
  - type: OpenAPI
    url: openapi/splunk-index-api-openapi.yml
  - type: Documentation
    url: https://docs.splunk.com/Documentation/Splunk/latest/RESTREF/RESTprolog
  - type: GettingStarted
    url: https://docs.splunk.com/Documentation/Splunk/latest/RESTUM/RESTusing
  - type: APIReference
    url: https://dev.splunk.com/enterprise/reference
  - type: APIReference
    url: https://help.splunk.com/en/splunk-enterprise/leverage-rest-apis/rest-api-reference/10.2/introduction/endpoints-reference-list
  - type: Authentication
    url: https://docs.splunk.com/Documentation/Splunk/latest/RESTUM/RESTusing
  - type: Documentation
    url: https://docs.splunk.com/Documentation/Splunk/latest/RESTREF/RESTsearch
  - type: JSONSchema
    url: json-schema/splunk-search-job-schema.json
  - type: JSONSchema
    url: json-schema/splunk-event-schema.json
  - type: JSONLD
    url: json-ld/splunk-context.jsonld
- aid: splunk:splunk-search-api
  name: Splunk Search API
  description: Endpoints for creating, managing, and retrieving search jobs and their results. Splunk search processing language
    (SPL) queries are submitted as search jobs that run asynchronously.
  humanURL: https://www.splunk.com/en_us/blog/learn/api-monitoring.html
  tags:
  - Search
  properties:
  - type: OpenAPI
    url: openapi/splunk-search-api-openapi.yml
  - type: Documentation
    url: https://docs.splunk.com/Documentation/Splunk/latest/RESTREF/RESTprolog
  - type: GettingStarted
    url: https://docs.splunk.com/Documentation/Splunk/latest/RESTUM/RESTusing
  - type: APIReference
    url: https://dev.splunk.com/enterprise/reference
  - type: APIReference
    url: https://help.splunk.com/en/splunk-enterprise/leverage-rest-apis/rest-api-reference/10.2/introduction/endpoints-reference-list
  - type: Authentication
    url: https://docs.splunk.com/Documentation/Splunk/latest/RESTUM/RESTusing
  - type: Documentation
    url: https://docs.splunk.com/Documentation/Splunk/latest/RESTREF/RESTsearch
  - type: JSONSchema
    url: json-schema/splunk-search-job-schema.json
  - type: JSONSchema
    url: json-schema/splunk-event-schema.json
  - type: JSONLD
    url: json-ld/splunk-context.jsonld
x-parent: cisco
x-relationship: acquisition
x-acquired: 2024
x-coverage:
  state: unreadable
  reason: no-machine-readable-spec
  detail: No OpenAPI or other machine-readable contract was found despite probing common spec URLs on api.splunk.com and docs
    hosts.
  evidence:
  - url: https://api.splunk.com/openapi.json
    status: 404
  checked: '2026-10-03'
x-enrichment:
  date: '2026-10-03'
  status: enriched
  artifacts_added: 26
  pass: modular-v1
  engine: identity=local,contract=local,surfaces=local,docs=local,regulatory=local
Splunk API — frequently asked questions
Does Splunk have an API?
Yes. APIs.io lists 14 APIs from Splunk, including Splunk, Splunk Cloud Platform REST API and Splunk Cloud Admin Config Service (ACS) API, and 11 more.
Is there an OpenAPI specification for the Splunk API?
Yes. APIs.io indexes 3 OpenAPI specifications for Splunk, each linked for download from this page.
How do I authenticate with the Splunk API?
Splunk documents its authentication (apiKey/http · 3 schemes). The details are profiled on APIs.io as Splunk Authentication.
How much does the Splunk API cost?
Splunk publishes its prices; its Splunk Cloud Platform plan is Get a quote as of 2026-10-28. APIs.io lists 18 pricing plans for Splunk, with each plan's price, limits and inclusions under Pricing on this page.
Does Splunk have an MCP server?
Yes. APIs.io lists 1 MCP server for Splunk.
Is the Splunk API ready for AI agents?
Splunk has a Kin Score of 61.4 out of 100 (strong) and an Agent Readiness score of 53.5 (agent-ready), scored by API Evangelist on 2026-11-06.
Calls without X-API-Key need no key. Calls with it need a paid plan — get a key.
Get an API key
Free tier, no form to fill in. Signing in shares your email address with us — we
store it to create your key and to recognise you if you sign in with another
provider. See our Privacy Policy and
Terms.
 Kin Score
How this is scored →
 It updates itself when the score changes. Paste this where you link to your API docs: